mirror of
https://github.com/Security-Onion-Solutions/securityonion.git
synced 2026-10-05 14:05:00 +02:00
Compare commits
922
Commits
| Author | SHA1 | Date | |
|---|---|---|---|
 Mike Reeves |
37116a9bdd | ||
 Jason Ertel |
6297a2632b | ||
 Jason Ertel |
5cc752f128 | ||
|
Mike Reeves
|
68d95cd1cb | ||
|
Mike Reeves
|
1a68c3cd24 | ||
 Josh Patterson |
87eec4ae88 | ||
|
m0duspwnens
|
676696b24a | ||
|
m0duspwnens
|
da27fce95f | ||
 weslambert |
8acc37a7d1 | ||
|
weslambert
|
5f1b467e64 | ||
|
weslambert
|
fe7fb7f54d | ||
|
Wes
|
577bfac886 | ||
|
Josh Patterson
|
468b6e4831 | ||
|
Josh Patterson
|
c75d209d7f | ||
 Josh Brower |
b29b264d5c | ||
|
Josh Brower
|
c99e7da5a7 | ||
|
Josh Patterson
|
60d66b973c | ||
|
m0duspwnens
|
304830d2ee | ||
|
m0duspwnens
|
d7285d69a7 | ||
|
weslambert
|
7cdd1f89d7 | ||
|
weslambert
|
b7cab1d118 | ||
|
weslambert
|
f03a472ee5 | ||
|
Mike Reeves
|
c7a0801eed | ||
|
Josh Brower
|
5e0015e9ac | ||
|
Josh Brower
|
5a72c558cb | ||
|
Josh Brower
|
a6e907f76c | ||
|
Josh Brower
|
2d3eb22057 | ||
|
Josh Brower
|
8437fcd94c | ||
|
Josh Brower
|
1b25db4573 | ||
|
m0duspwnens
|
f8ed2e6e8e | ||
|
m0duspwnens
|
f22c61a0a2 | ||
|
m0duspwnens
|
5069d1163c | ||
|
Josh Brower
|
31edf2e8ea | ||
|
Wes
|
6b8893ded5 | ||
|
m0duspwnens
|
1f8b7bda89 | ||
|
m0duspwnens
|
59233d6550 | ||
|
m0duspwnens
|
1ac72e5b24 | ||
|
Josh Brower
|
7805ca8beb | ||
|
m0duspwnens
|
47b2481cdd | ||
|
m0duspwnens
|
fa933d3f53 | ||
|
m0duspwnens
|
f4dc73a206 | ||
 Doug Burks |
437c9cab68 | ||
|
Wes
|
6da96a733f | ||
|
Doug Burks
|
82796370ce | ||
|
Josh Brower
|
8c16feb772 | ||
|
Josh Brower
|
ce1f363424 | ||
|
Josh Brower
|
e8860a7d2c | ||
|
Josh Brower
|
beb26596fd | ||
|
m0duspwnens
|
6a5ff04804 | ||
|
Josh Brower
|
ff3bb11fbb | ||
|
m0duspwnens
|
8be5082b60 | ||
 coreyogburn |
5faa4f0a30 | ||
 Corey Ogburn |
da7770a900 | ||
|
weslambert
|
8178338971 | ||
|
weslambert
|
79ed17b506 | ||
|
Josh Patterson
|
2785587840 | ||
|
weslambert
|
9f95306458 | ||
|
m0duspwnens
|
55bed0771b | ||
|
Wes
|
0b5ee49873 | ||
|
Jason Ertel
|
1646459052 | ||
|
Jason Ertel
|
8ec003d89f | ||
|
Jason Ertel
|
224f0606c2 | ||
|
Wes
|
910125f13a | ||
|
Jason Ertel
|
5eca1acbeb | ||
|
Wes
|
d551faeb16 | ||
|
Josh Patterson
|
6a6afeef75 | ||
|
m0duspwnens
|
869f60ccaa | ||
|
m0duspwnens
|
12c82d2812 | ||
|
m0duspwnens
|
a2b50c6d40 | ||
|
m0duspwnens
|
ab7ae6cddd | ||
|
m0duspwnens
|
7a9a12ae3d | ||
|
m0duspwnens
|
b49a296276 | ||
|
Josh Patterson
|
9b9321d23a | ||
|
m0duspwnens
|
1922ad95d5 | ||
|
Josh Patterson
|
9de8814412 | ||
|
Josh Brower
|
35e7659904 | ||
|
weslambert
|
d31ea4097d | ||
|
Wes
|
c277b7acfa | ||
|
m0duspwnens
|
97a9e0989d | ||
|
Wes
|
6bdccec6b1 | ||
|
m0duspwnens
|
35945ed224 | ||
|
m0duspwnens
|
7319d7ae9b | ||
|
Wes
|
8b38cbe8cf | ||
|
Wes
|
35ea084466 | ||
|
Jason Ertel
|
c89582ffb6 | ||
|
Jason Ertel
|
d6db94a4d4 | ||
|
Wes
|
e2acf027a9 | ||
|
m0duspwnens
|
d6d8ba7479 | ||
|
m0duspwnens
|
41a4321b03 | ||
|
Jason Ertel
|
2ae049071d | ||
|
Jason Ertel
|
e82df53997 | ||
|
Wes
|
273e78da94 | ||
|
Wes
|
446376395e | ||
|
Wes
|
a13001dce0 | ||
|
Wes
|
8819e1d4d6 | ||
|
Josh Brower
|
1baea3bcd5 | ||
|
Josh Patterson
|
1c37c05824 | ||
|
m0duspwnens
|
cd1db36c13 | ||
|
m0duspwnens
|
5898c9ef31 | ||
|
Jason Ertel
|
951f04c265 | ||
|
Josh Brower
|
4b069d91ab | ||
|
Josh Brower
|
7561ec0512 | ||
|
Josh Patterson
|
eef1b40436 | ||
|
m0duspwnens
|
34db6fb823 | ||
|
m0duspwnens
|
eeaf077baf | ||
|
m0duspwnens
|
120d21c0da | ||
|
m0duspwnens
|
66457ad8f8 | ||
|
m0duspwnens
|
69670c481d | ||
|
m0duspwnens
|
cae011babb | ||
|
m0duspwnens
|
02ea939abc | ||
|
m0duspwnens
|
be028aa23e | ||
|
m0duspwnens
|
24b7f7a7ce | ||
|
m0duspwnens
|
12cce111db | ||
|
weslambert
|
add72d7a5c | ||
|
Josh Brower
|
c7a1d4758b | ||
|
Wes
|
8436b647dd | ||
|
Doug Burks
|
77e6ee3c36 | ||
|
Doug Burks
|
3e71663669 | ||
|
Mike Reeves
|
984971c63c | ||
|
Mike Reeves
|
6adef20a06 | ||
|
Mike Reeves
|
cb8faf7c5f | ||
|
Mike Reeves
|
740723ecd6 | ||
|
Mike Reeves
|
d70371c540 | ||
|
Mike Reeves
|
b6986d5c61 | ||
|
Mike Reeves
|
02e6e11be7 | ||
|
Mike Reeves
|
d26484fe1a | ||
|
Mike Reeves
|
12d10d7d42 | ||
|
Mike Reeves
|
7ea37ac2dd | ||
|
Mike Reeves
|
7aae72cfcf | ||
|
Mike Reeves
|
ec427cde08 | ||
|
weslambert
|
c2efd7ef64 | ||
|
Mike Reeves
|
77c58e665e | ||
|
Mike Reeves
|
9530901d1d | ||
|
Doug Burks
|
e83afa3e30 | ||
|
Doug Burks
|
70fb28a8b3 | ||
|
Josh Brower
|
8355432356 | ||
|
Josh Brower
|
2247cafe5f | ||
|
Josh Brower
|
85a8da6331 | ||
|
Josh Brower
|
ddabab253c | ||
|
Jason Ertel
|
2e42eddbc2 | ||
|
Jason Ertel
|
07a590dda8 | ||
|
Mike Reeves
|
ec8eac3430 | ||
|
weslambert
|
05b84327b8 | ||
|
Mike Reeves
|
0607532e4a | ||
|
Mike Reeves
|
3018886f72 | ||
|
weslambert
|
e02bdffe34 | ||
|
Mike Reeves
|
5073d62ee8 | ||
|
weslambert
|
e2ff48164b | ||
|
Mike Reeves
|
43832f9c34 | ||
|
Mike Reeves
|
5da5a04025 | ||
|
Mike Reeves
|
25b51135fc | ||
|
weslambert
|
aa91c1fef2 | ||
|
Mike Reeves
|
801a5a6824 | ||
|
Mike Reeves
|
f63c26b7f2 | ||
|
Josh Brower
|
336a40d646 | ||
|
Josh Brower
|
bb0cfc5253 | ||
|
coreyogburn
|
106aaa9c3e | ||
|
weslambert
|
ff7db0be63 | ||
|
Wes
|
b96d3473f2 | ||
|
Corey Ogburn
|
fb27e7c479 | ||
|
Corey Ogburn
|
261acee8a0 | ||
|
Josh Brower
|
a9585b2a7f | ||
|
Wes
|
62fa15c63e | ||
|
weslambert
|
e995576b1d | ||
|
Jason Ertel
|
d247c9d704 | ||
|
Jason Ertel
|
b21b545756 | ||
|
Wes
|
5e8748c436 | ||
|
Wes
|
e2cca917c1 | ||
|
Wes
|
d8700137d2 | ||
|
Wes
|
2c42d4b19e | ||
|
Wes
|
a3c7e40c40 | ||
|
Wes
|
94fe456e28 | ||
|
Wes
|
662db41857 | ||
|
Jason Ertel
|
7623dd20b9 | ||
|
Corey Ogburn
|
2b323ab661 | ||
|
Josh Brower
|
8de01625a8 | ||
|
Josh Brower
|
d0d7ab57ca | ||
|
Jason Ertel
|
f4cbe20ddf | ||
|
Jason Ertel
|
0d92a1594a | ||
|
m0duspwnens
|
daaead618e | ||
|
m0duspwnens
|
19469205e1 | ||
|
Jason Ertel
|
cae9e6230f | ||
|
m0duspwnens
|
6c4c815683 | ||
|
Corey Ogburn
|
6769386c86 | ||
|
m0duspwnens
|
36272efda7 | ||
|
weslambert
|
6b97d07a89 | ||
|
coreyogburn
|
da82395dcf | ||
|
Corey Ogburn
|
b5e5bd57ad | ||
|
Josh Patterson
|
ad4fb52b81 | ||
|
m0duspwnens
|
4e849ecc90 | ||
|
weslambert
|
7e37cd0f05 | ||
|
Mike Reeves
|
3952c1a9b7 | ||
|
Mike Reeves
|
c13c37f406 | ||
|
Mike Reeves
|
9240c3c6f0 | ||
|
Mike Reeves
|
2aa01280e7 | ||
|
m0duspwnens
|
1675b787bf | ||
|
Mike Reeves
|
4866eb2315 | ||
|
Mike Reeves
|
f785fb2772 | ||
|
Mike Reeves
|
8c9f863808 | ||
|
Mike Reeves
|
1751e35121 | ||
|
Mike Reeves
|
6676afc7de | ||
|
Mike Reeves
|
699ea1ac3e | ||
|
Mike Reeves
|
90fdb9c465 | ||
|
Mike Reeves
|
48291f5271 | ||
|
Mike Reeves
|
3a41b090c1 | ||
|
Josh Brower
|
139b36b189 | ||
|
Josh Brower
|
6ddf887342 | ||
|
Josh Brower
|
6ba9e057a9 | ||
|
Mike Reeves
|
6600484f8e | ||
|
Mike Reeves
|
b02c38175c | ||
|
Mike Reeves
|
4497f6561f | ||
|
Mike Reeves
|
0fc03baf58 | ||
|
coreyogburn
|
fb81c6e2e3 | ||
|
Corey Ogburn
|
ad28ea275f | ||
|
Corey Ogburn
|
41951659ec | ||
|
Corey Ogburn
|
451a4784a1 | ||
|
Corey Ogburn
|
1b7095fa81 | ||
|
Corey Ogburn
|
89d789fe0f | ||
|
Corey Ogburn
|
49055e260f | ||
|
Corey Ogburn
|
a465039887 | ||
|
Doug Burks
|
b60cf29598 | ||
|
Doug Burks
|
0e09d73aa0 | ||
|
Doug Burks
|
520a5671ca | ||
|
Doug Burks
|
fc824359ed | ||
|
Doug Burks
|
7caa7cec6b | ||
|
Josh Patterson
|
0695140f83 | ||
|
m0duspwnens
|
ed1e2c8908 | ||
|
Jason Ertel
|
594900a8d4 | ||
|
Jason Ertel
|
6894fa4e4d | ||
|
m0duspwnens
|
2334d82d36 | ||
|
Josh Patterson
|
c0a2ea3138 | ||
|
m0duspwnens
|
d4acb1a33a | ||
|
m0duspwnens
|
5de9e5baf4 | ||
|
Wes
|
3a34da354f | ||
|
m0duspwnens
|
469390696e | ||
|
Josh Brower
|
0a4a48b61e | ||
|
Wes
|
58a63e0765 | ||
|
Doug Burks
|
251bc6f45e | ||
|
Doug Burks
|
b84d997f87 | ||
|
Wes
|
b5bccc5e05 | ||
|
Jason Ertel
|
b4e5ac9796 | ||
|
m0duspwnens
|
2db95fe1b4 | ||
|
m0duspwnens
|
934b0f45a1 | ||
|
Jason Ertel
|
a88227d13f | ||
|
Jason Ertel
|
21a7b76352 | ||
|
weslambert
|
03082339ca | ||
|
m0duspwnens
|
8f6226b531 | ||
|
m0duspwnens
|
2c4eccd7e0 | ||
|
Josh Brower
|
fa57494694 | ||
|
weslambert
|
3f1741e75a | ||
|
Wes
|
48331ce35b | ||
|
Wes
|
c2ac60b82e | ||
|
Josh Brower
|
fedfbe9fec | ||
|
Josh Brower
|
9947f9def4 | ||
|
Wes
|
c205438771 | ||
|
Wes
|
8cde05807c | ||
|
Wes
|
2ac0aba916 | ||
|
Wes
|
af003cc2a1 | ||
|
Josh Brower
|
0d4f6b4fe6 | ||
|
Jason Ertel
|
7093254439 | ||
|
Wes
|
bd7644a557 | ||
|
Jason Ertel
|
90b740a997 | ||
|
Wes
|
5547a1b7ab | ||
|
Wes
|
1b90fd8581 | ||
|
Doug Burks
|
bbdf7bb5a7 | ||
|
Doug Burks
|
fb8ad71b27 | ||
|
Wes
|
e43b7607bb | ||
|
Wes
|
a265c06e31 | ||
|
Wes
|
2aa954cb0a | ||
|
Wes
|
73812b11a3 | ||
|
Wes
|
38ab426470 | ||
|
Wes
|
d0a6881c2c | ||
|
m0duspwnens
|
c7c4e65df1 | ||
|
m0duspwnens
|
49b150797d | ||
|
Wes
|
57268ba934 | ||
|
Wes
|
1208915896 | ||
|
Wes
|
42f5ad9939 | ||
|
Doug Burks
|
8e0d895afb | ||
|
Doug Burks
|
998c85e3f8 | ||
|
weslambert
|
32f3ee0b01 | ||
|
Doug Burks
|
a90aed25fb | ||
|
Doug Burks
|
ae14e4870d | ||
|
Doug Burks
|
273a1d7e9c | ||
|
Doug Burks
|
b3f8ed7dcd | ||
|
Wes
|
ad5a424c03 | ||
|
Jason Ertel
|
e06787445c | ||
|
Jason Ertel
|
8a4f5d6dcb | ||
|
Doug Burks
|
81dd951064 | ||
|
Doug Burks
|
c12f138899 | ||
|
Jason Ertel
|
884a7041af | ||
|
Jason Ertel
|
023008c54c | ||
|
Jason Ertel
|
6f7de954d9 | ||
|
Jason Ertel
|
46371aaaf5 | ||
|
Doug Burks
|
1fde2e2755 | ||
|
Doug Burks
|
1aad9d1b2f | ||
|
Doug Burks
|
9703e70163 | ||
|
Doug Burks
|
f6735207d7 | ||
|
Doug Burks
|
e5f76a9c6e | ||
|
weslambert
|
d1c86cb9ff | ||
|
weslambert
|
8ccb24dda2 | ||
|
weslambert
|
932054e9da | ||
|
Josh Brower
|
8b35002169 | ||
|
weslambert
|
f68527d366 | ||
|
Wes
|
81e3d26540 | ||
|
weslambert
|
96b60fa39a | ||
|
weslambert
|
f172a74fbc | ||
|
weslambert
|
c4be56ec7b | ||
|
weslambert
|
96195806ab | ||
|
weslambert
|
88bbd3440d | ||
|
Wes
|
495a9c0783 | ||
|
Wes
|
905bc564fc | ||
|
Wes
|
f6f387428f | ||
|
Jason Ertel
|
db5abcb3cf | ||
|
Jason Ertel
|
27e310c2a1 | ||
|
weslambert
|
236eb0cbcc | ||
|
Wes
|
841d0b4b1f | ||
|
Wes
|
272f97e2d7 | ||
|
Wes
|
eac9a3fc86 | ||
|
Doug Burks
|
32dc26f2e7 | ||
|
Doug Burks
|
1b14142e4c | ||
|
Jason Ertel
|
2fef1d5fa7 | ||
|
Jason Ertel
|
3bbfc3865d | ||
|
Jason Ertel
|
6947fd6414 | ||
|
Doug Burks
|
d3e5be78fd | ||
|
Doug Burks
|
09e005127e | ||
|
Mike Reeves
|
d3ea596deb | ||
|
Mike Reeves
|
d6d315e8d5 | ||
|
Mike Reeves
|
58dc073678 | ||
|
Mike Reeves
|
8c9186d8dd | ||
|
Mike Reeves
|
aee842b912 | ||
|
weslambert
|
3a5a59af59 | ||
|
Josh Patterson
|
8f3a874e61 | ||
|
m0duspwnens
|
66dc6274e6 | ||
|
Wes
|
302e580d8f | ||
|
Mike Reeves
|
4cf60a6054 | ||
|
Mike Reeves
|
8f6d82af97 | ||
|
Mike Reeves
|
8ab54dcead | ||
|
Mike Reeves
|
9704c8917e | ||
|
weslambert
|
540ee156db | ||
|
Wes
|
344e2bf1d0 | ||
|
Wes
|
3441c0684e | ||
|
Wes
|
ed560f19d3 | ||
|
Wes
|
b3f6012856 | ||
|
Wes
|
9ae26ec866 | ||
|
Wes
|
20aaa79476 | ||
|
Wes
|
2bb77251b0 | ||
|
weslambert
|
36791665f3 | ||
|
Josh Patterson
|
4d4744a89b | ||
|
Wes
|
f3be63051b | ||
|
m0duspwnens
|
743ed316f8 | ||
|
Wes
|
e4b4bbcfdc | ||
|
Wes
|
b6e090f29f | ||
|
weslambert
|
25006ed20b | ||
|
Wes
|
4469a93a75 | ||
|
Mike Reeves
|
0027016b5a | ||
|
Mike Reeves
|
0143e2412d | ||
|
Mike Reeves
|
20212414c4 | ||
|
Mike Reeves
|
8a63ed5124 | ||
|
Wes
|
096dadf9bd | ||
|
Wes
|
b441fe662f | ||
|
Wes
|
e5117a343d | ||
|
Wes
|
b9d692eb0e | ||
|
Wes
|
36a7f54160 | ||
|
Josh Brower
|
96134684dc | ||
|
Jason Ertel
|
374ab0779a | ||
|
Jason Ertel
|
d0d1cc9106 | ||
|
Jason Ertel
|
162a32fd08 | ||
|
Wes
|
9035fa3037 | ||
|
Wes
|
b4b87e5620 | ||
|
Wes
|
97c53d70a4 | ||
|
Wes
|
53b4f7bd5c | ||
|
Mike Reeves
|
192c8c78c7 | ||
|
Mike Reeves
|
62a063dae4 | ||
|
Wes
|
79014a53ec | ||
|
Wes
|
e910f04beb | ||
|
Wes
|
ef5b63337b | ||
|
Wes
|
799e92e595 | ||
|
Wes
|
c835c523a9 | ||
|
Josh Brower
|
9ec1492fad | ||
|
Wes
|
5af1bfe142 | ||
|
Jason Ertel
|
482c5324db | ||
|
Mike Reeves
|
3c1f1cd50e | ||
|
Mike Reeves
|
aecd900203 | ||
|
Mike Reeves
|
89f5d9f292 | ||
|
Josh Brower
|
de43a202a3 | ||
|
Josh Brower
|
6176fa7ca5 | ||
|
Mike Reeves
|
9ff27e5b6a | ||
|
Mike Reeves
|
5922fc0e45 | ||
|
Mike Reeves
|
b48e259fee | ||
|
Mike Reeves
|
b4d85a7bf8 | ||
|
Mike Reeves
|
38881231ac | ||
|
Mike Reeves
|
b2d2a9f0ed | ||
|
Jason Ertel
|
32021cf272 | ||
|
Jason Ertel
|
4410e136b1 | ||
|
Jason Ertel
|
81d4584819 | ||
|
Jason Ertel
|
f765dc23ea | ||
|
Jason Ertel
|
657ef97d17 | ||
|
Jason Ertel
|
8f247f962a | ||
|
Josh Patterson
|
bcbdab1682 | ||
|
m0duspwnens
|
5b4ec70ca6 | ||
|
Wes
|
ce114a2601 | ||
|
Wes
|
5de59a879a | ||
|
Jason Ertel
|
a2e6469a38 | ||
|
m0duspwnens
|
5c933910aa | ||
|
m0duspwnens
|
a3c3f08511 | ||
|
Jason Ertel
|
9aa58be286 | ||
|
Jason Ertel
|
db56b3d6a3 | ||
|
Jason Ertel
|
7d6182a18f | ||
|
Jason Ertel
|
074f84ae4d | ||
|
Mike Reeves
|
8ce0d76287 | ||
|
Mike Reeves
|
3be3df00d1 | ||
|
m0duspwnens
|
d99d4756c3 | ||
|
m0duspwnens
|
0d83b13585 | ||
|
m0duspwnens
|
6505d3e2ce | ||
|
Josh Patterson
|
6edfadd18b | ||
|
Josh Patterson
|
9552510c7d | ||
|
Doug Burks
|
36ddcfa4e5 | ||
|
Doug Burks
|
fcc1337e1a | ||
|
Mike Reeves
|
10f9d0f4bd | ||
|
Mike Reeves
|
edf531739c | ||
|
Mike Reeves
|
11d7e66ea0 | ||
|
Mike Reeves
|
caaedee5a7 | ||
|
Mike Reeves
|
1bdd79c578 | ||
|
Mike Reeves
|
c199acc64e | ||
|
Josh Patterson
|
a01704a1d7 | ||
|
Wes
|
53f258b08f | ||
|
Wes
|
a308a39bbe | ||
|
m0duspwnens
|
5c00655ad0 | ||
|
m0duspwnens
|
67a608ea56 | ||
|
Josh Brower
|
01d983fc00 | ||
|
Mike Reeves
|
d6f1bcfdf0 | ||
|
Josh Brower
|
f156573f8d | ||
|
Josh Brower
|
b3e0e68896 | ||
|
Mike Reeves
|
86803f1fb5 | ||
|
Jason Ertel
|
aad08a830b | ||
|
Mike Reeves
|
c9db6c0f18 | ||
|
Jason Ertel
|
d9a9c8738c | ||
|
Mike Reeves
|
cb0ed9ae6d | ||
|
Josh Brower
|
4f72fca2d7 | ||
|
Josh Patterson
|
1dc426b8ce | ||
|
m0duspwnens
|
8995012c80 | ||
|
Mike Reeves
|
2c4ba2e8b2 | ||
|
Mike Reeves
|
c42959d040 | ||
|
Mike Reeves
|
fa6dcd7f83 | ||
|
Josh Brower
|
9c6365aa2f | ||
|
Josh Patterson
|
6e4c4febfb | ||
|
m0duspwnens
|
732d2aadf8 | ||
|
Mike Reeves
|
cace817c79 | ||
|
Josh Brower
|
e1c361e555 | ||
|
Josh Brower
|
502277b1b7 | ||
 bryant-treacle |
57f5a22f0f | ||
|
Josh Patterson
|
4b18a0e758 | ||
|
Josh Brower
|
f6a9a764de | ||
|
m0duspwnens
|
e65214b097 | ||
|
m0duspwnens
|
cc47f9a595 | ||
|
m0duspwnens
|
eb633be437 | ||
|
Josh Brower
|
df0dc2e4d1 | ||
|
Josh Brower
|
766f4dd661 | ||
|
Jason Ertel
|
f53fb69ffb | ||
|
Jason Ertel
|
ba0ec18a33 | ||
|
weslambert
|
79182cecfd | ||
|
weslambert
|
8cf82c4b6a | ||
|
weslambert
|
78d4586033 | ||
|
Jason Ertel
|
02cf1074f2 | ||
|
Jason Ertel
|
a881cab469 | ||
|
weslambert
|
00bd93c026 | ||
|
weslambert
|
2c10ad7eec | ||
|
weslambert
|
167051af28 | ||
|
weslambert
|
eb9c5e9af0 | ||
|
Jason Ertel
|
2f942a3e37 | ||
|
Jason Ertel
|
03f97b309a | ||
|
weslambert
|
c6a962a46b | ||
|
weslambert
|
1ddf45bbbe | ||
|
Doug Burks
|
f0c4cebaca | ||
|
Doug Burks
|
87c42ece00 | ||
|
Doug Burks
|
4f8fcd3369 | ||
|
bryant-treacle
|
5b2d91b5b5 | ||
|
bryant-treacle
|
a84322f9b7 | ||
|
bryant-treacle
|
2de95bcb63 | ||
|
bryant-treacle
|
1e9e2facde | ||
|
bryant-treacle
|
592c67d1f2 | ||
|
bryant-treacle
|
e91dd29cb2 | ||
|
bryant-treacle
|
13c9142814 | ||
|
bryant-treacle
|
ef4f2491f3 | ||
|
bryant-treacle
|
645555b990 | ||
|
bryant-treacle
|
839275814c | ||
|
bryant-treacle
|
9b973e07e2 | ||
|
Josh Patterson
|
0027385da9 | ||
|
m0duspwnens
|
4ef77f9050 | ||
|
Mike Reeves
|
debbdec350 | ||
|
Mike Reeves
|
bf4ac0c2dd | ||
|
Mike Reeves
|
cb9e7e63db | ||
|
Mike Reeves
|
32560af767 | ||
|
Mike Reeves
|
1e5ac61ff5 | ||
|
Mike Reeves
|
5315c51197 | ||
|
Mike Reeves
|
8917f9b9d2 | ||
|
Mike Reeves
|
c0dc05f26a | ||
|
Mike Reeves
|
2aa801d906 | ||
|
weslambert
|
c192ec9109 | ||
|
Mike Reeves
|
7ab31e36af | ||
|
Mike Reeves
|
0fd9fb9294 | ||
|
Josh Patterson
|
059f80bfc4 | ||
|
m0duspwnens
|
bab2f7282c | ||
|
m0duspwnens
|
02920b5ac9 | ||
|
m0duspwnens
|
25b0934cda | ||
|
Wes
|
d3c7ea4805 | ||
|
Wes
|
82c3d78672 | ||
|
Josh Brower
|
97b68609bc | ||
|
Josh Patterson
|
1d611e618f | ||
|
m0duspwnens
|
f4b8d385ee | ||
|
Jason Ertel
|
b7e0923ec4 | ||
|
Jason Ertel
|
4930ae4ba6 | ||
|
Josh Brower
|
d11479ec5f | ||
|
Josh Brower
|
901e3c4a20 | ||
|
Josh Patterson
|
81842462ba | ||
|
m0duspwnens
|
e15c14cc2e | ||
|
m0duspwnens
|
f7ddf57f39 | ||
|
Josh Brower
|
47e67fda46 | ||
|
Josh Brower
|
7d0251952c | ||
|
Josh Brower
|
5536f5a8c2 | ||
|
Josh Patterson
|
2c932fae9d | ||
|
Josh Brower
|
24445cf36a | ||
|
m0duspwnens
|
0feb25c962 | ||
|
m0duspwnens
|
3abb4d79ba | ||
|
Josh Patterson
|
1df183deb3 | ||
|
m0duspwnens
|
77834c1e58 | ||
|
Josh Patterson
|
d6207705cd | ||
|
m0duspwnens
|
e4b61aa08d | ||
|
Josh Patterson
|
736ff2930d | ||
|
m0duspwnens
|
6aff526d9e | ||
|
Josh Brower
|
8101171c97 | ||
|
Josh Brower
|
000507c366 | ||
|
Josh Patterson
|
82fdee45aa | ||
|
m0duspwnens
|
2419fa43b6 | ||
|
m0duspwnens
|
acc7619023 | ||
|
Jason Ertel
|
dcd761ad74 | ||
|
Jason Ertel
|
9871ecd223 | ||
|
Josh Patterson
|
56a7fdcfcd | ||
|
m0duspwnens
|
6325f6db16 | ||
|
m0duspwnens
|
b253cd45ca | ||
|
Jason Ertel
|
1724565331 | ||
|
Jason Ertel
|
00a7beaca2 | ||
|
Mike Reeves
|
c129bba7e5 | ||
|
Mike Reeves
|
fb298224fc | ||
|
Josh Brower
|
1feed47185 | ||
|
Josh Brower
|
923de356e1 | ||
|
Jason Ertel
|
cea9af4e01 | ||
|
Jason Ertel
|
0f6d894322 | ||
|
Josh Brower
|
9f879164ec | ||
|
Jason Ertel
|
1ddc4b6ff8 | ||
|
Jason Ertel
|
58f80120bd | ||
|
m0duspwnens
|
a0e08e4f41 | ||
|
m0duspwnens
|
2813d67670 | ||
|
m0duspwnens
|
c49b134122 | ||
|
Mike Reeves
|
48ce377b02 | ||
|
Josh Brower
|
40de01e8c4 | ||
|
Mike Reeves
|
2fe88a1e66 | ||
|
Mike Reeves
|
214117e0e0 | ||
|
Josh Brower
|
bc2d3e43f0 | ||
|
Josh Brower
|
b3528b2139 | ||
|
Josh Brower
|
7ecd067e2b | ||
|
Josh Brower
|
576c1d7cc1 | ||
|
m0duspwnens
|
6320528263 | ||
|
Josh Brower
|
6528632861 | ||
|
m0duspwnens
|
928b3b5471 | ||
|
m0duspwnens
|
f1c8467e9b | ||
|
m0duspwnens
|
f5337eba1a | ||
|
Jason Ertel
|
de28e15805 | ||
|
Jason Ertel
|
09ba15f9bb | ||
|
Jason Ertel
|
ba9892941d | ||
|
Josh Brower
|
b381c51246 | ||
|
Josh Brower
|
64726af69c | ||
|
m0duspwnens
|
7a4fea7a12 | ||
|
m0duspwnens
|
db47256cdd | ||
|
m0duspwnens
|
ba2392997b | ||
|
m0duspwnens
|
1a1bcb3526 | ||
|
m0duspwnens
|
997e6c141a | ||
|
Doug Burks
|
9a3c997779 | ||
|
Doug Burks
|
53ed4d49c2 | ||
|
m0duspwnens
|
0cee5b54a1 | ||
|
m0duspwnens
|
3f8e15d16f | ||
|
Doug Burks
|
f8f6a1433a | ||
|
Doug Burks
|
83188401c5 | ||
|
Doug Burks
|
b01367a294 | ||
|
Doug Burks
|
d8e0e320f4 | ||
|
m0duspwnens
|
b033f0d20f | ||
|
m0duspwnens
|
b71b4225c4 | ||
|
m0duspwnens
|
2a39f5f0b5 | ||
|
m0duspwnens
|
e27e690bc8 | ||
|
m0duspwnens
|
57371ffe5a | ||
|
m0duspwnens
|
4440ecd433 | ||
|
m0duspwnens
|
277ad61920 | ||
|
m0duspwnens
|
0860b1501e | ||
|
m0duspwnens
|
b06610088a | ||
|
m0duspwnens
|
aa2f168b73 | ||
|
m0duspwnens
|
d1f7e5f4a7 | ||
|
m0duspwnens
|
05a81596e5 | ||
|
m0duspwnens
|
00d1ca0b62 | ||
|
Josh Brower
|
dbd4a5bd98 | ||
|
Doug Burks
|
3db34a3346 | ||
|
Doug Burks
|
f9890778ad | ||
|
m0duspwnens
|
e342dae818 | ||
|
Mike Reeves
|
64e294ef48 | ||
|
Mike Reeves
|
992bbdfac1 | ||
|
Mike Reeves
|
a4cd695cc8 | ||
|
Doug Burks
|
9f85b3cb4f | ||
|
Doug Burks
|
e9fd7d8b8b | ||
|
m0duspwnens
|
fa1a428133 | ||
|
m0duspwnens
|
8e18986671 | ||
|
m0duspwnens
|
a3b97b40ba | ||
|
Doug Burks
|
634dd9907d | ||
|
Doug Burks
|
1d12dcd243 | ||
|
Jason Ertel
|
2ec8d6abf0 | ||
|
Jason Ertel
|
98c19e5934 | ||
|
m0duspwnens
|
03e7636a18 | ||
|
m0duspwnens
|
6ce9561ba7 | ||
|
m0duspwnens
|
b80dd996cc | ||
|
m0duspwnens
|
63cea88c1d | ||
|
m0duspwnens
|
f41c75c633 | ||
|
m0duspwnens
|
20f706f165 | ||
|
m0duspwnens
|
c74b440922 | ||
|
Mike Reeves
|
badaab94de | ||
|
Mike Reeves
|
2be6c603ab | ||
|
Jason Ertel
|
7700a5a1bf | ||
|
Jason Ertel
|
687a89e30b | ||
|
m0duspwnens
|
06a0492226 | ||
|
m0duspwnens
|
4e4034e054 | ||
|
m0duspwnens
|
5b06aa518e | ||
|
m0duspwnens
|
c91fb438bb | ||
|
m0duspwnens
|
54c9a3ec71 | ||
|
Mike Reeves
|
cc1babbea6 | ||
|
Mike Reeves
|
bde67266d4 | ||
|
Josh Brower
|
1de1e2fdc2 | ||
|
Josh Brower
|
2293574f2e | ||
|
Mike Reeves
|
3077c21bd9 | ||
|
Mike Reeves
|
a52ca6e298 | ||
|
m0duspwnens
|
02e1a29f0c | ||
|
m0duspwnens
|
1b9ed1c72b | ||
|
Mike Reeves
|
9564158c32 | ||
|
m0duspwnens
|
ce1f75aab6 | ||
|
m0duspwnens
|
a0ce46e702 | ||
|
Mike Reeves
|
f501fac9cd | ||
|
Mike Reeves
|
8b95edd91a | ||
|
m0duspwnens
|
c5e5763014 | ||
|
m0duspwnens
|
2322ed4b6d | ||
|
m0duspwnens
|
38d69701a4 | ||
|
m0duspwnens
|
4dc0f06331 | ||
|
m0duspwnens
|
ec7bcd9b0c | ||
|
Doug Burks
|
24140c4cda | ||
|
m0duspwnens
|
6909d3ed14 | ||
|
Doug Burks
|
cf5feafb1e | ||
|
Josh Brower
|
ebc20a86eb | ||
|
Mike Reeves
|
e792fbe023 | ||
|
Mike Reeves
|
02b619193d | ||
|
Mike Reeves
|
e5aab3b707 | ||
|
Mike Reeves
|
089fcbd0c5 | ||
|
Josh Brower
|
62bafb94f9 | ||
|
m0duspwnens
|
9d6fb98e3b | ||
|
m0duspwnens
|
7bd9a84aa1 | ||
|
m0duspwnens
|
328b714306 | ||
|
m0duspwnens
|
2a979197a0 | ||
|
Jason Ertel
|
6f7f09f1cd | ||
|
m0duspwnens
|
f9804c218d | ||
|
Jason Ertel
|
dfc4498921 | ||
|
m0duspwnens
|
9049f9cf03 | ||
|
Jason Ertel
|
79a5f3a89f | ||
|
Jason Ertel
|
c7cb11e919 | ||
|
Jason Ertel
|
da81d93930 | ||
|
Jason Ertel
|
44344612b7 | ||
|
Jason Ertel
|
7ac4bc52a3 | ||
|
m0duspwnens
|
9aaa33c224 | ||
|
weslambert
|
a13e6257c3 | ||
|
m0duspwnens
|
ef18cb3704 | ||
|
m0duspwnens
|
d5c7eec4ef | ||
|
m0duspwnens
|
a2c444e03b | ||
|
Jason Ertel
|
40c3f9a156 | ||
|
Jason Ertel
|
bd23d1ab7b | ||
|
weslambert
|
a1e0041b14 | ||
|
weslambert
|
7483dbf442 | ||
|
Wes
|
0f30e787b3 | ||
|
m0duspwnens
|
5d50dbb69e | ||
|
Mike Reeves
|
867ea5a1ac | ||
|
Doug Burks
|
52cfc59113 | ||
|
Mike Reeves
|
789eafa8c2 | ||
|
Doug Burks
|
ed712477d6 | ||
|
Mike Reeves
|
e3cb0a9953 | ||
|
m0duspwnens
|
743bbfea35 | ||
|
m0duspwnens
|
e8a5a5bffb | ||
|
m0duspwnens
|
a97fa9675b | ||
|
Mike Reeves
|
2418d9a096 | ||
|
m0duspwnens
|
2a8ed24045 | ||
|
Mike Reeves
|
f1c91e91b1 | ||
|
m0duspwnens
|
5405bc4e20 | ||
|
m0duspwnens
|
47a580d110 | ||
|
Mike Reeves
|
61a43f7df5 | ||
|
Mike Reeves
|
21ffcbf2fd | ||
|
Mike Reeves
|
563c0631ba | ||
|
Mike Reeves
|
77cbf35625 | ||
|
Mike Reeves
|
d7972032e4 | ||
|
Mike Reeves
|
f6dcefe0f8 | ||
|
Mike Reeves
|
d5a1406095 | ||
|
Josh Patterson
|
3d3be6bd29 | ||
|
m0duspwnens
|
52fec5fef0 | ||
|
m0duspwnens
|
ddb776c80e | ||
|
Mike Reeves
|
469258ee5e | ||
|
Mike Reeves
|
4fec2a18a5 | ||
|
weslambert
|
c7ed29dfa8 | ||
|
Mike Reeves
|
80cbe5f6e8 | ||
|
Mike Reeves
|
a64eb0ba97 | ||
|
Josh Patterson
|
dbb1b82e1b | ||
|
m0duspwnens
|
f34627f709 | ||
|
Josh Patterson
|
59451fc4d0 | ||
|
m0duspwnens
|
dc77b20723 | ||
|
Josh Patterson
|
51869ce5b2 | ||
|
m0duspwnens
|
98705608a6 | ||
|
Mike Reeves
|
8055088d25 | ||
|
Mike Reeves
|
d0cfaaeb26 | ||
|
Mike Reeves
|
fbacfce0e4 | ||
|
m0duspwnens
|
082704ce1f | ||
|
m0duspwnens
|
71b6311edc | ||
|
Mike Reeves
|
7e71c60334 | ||
|
Mike Reeves
|
c5c2600799 | ||
|
Josh Brower
|
c6c3cc82e4 | ||
|
Josh Brower
|
b17b68034e | ||
|
Mike Reeves
|
cbd1c05929 | ||
|
m0duspwnens
|
b14d33ced8 | ||
|
Mike Reeves
|
a5b1660778 | ||
|
Mike Reeves
|
d5c4a2887e | ||
|
Josh Brower
|
b4b84038ed | ||
|
Josh Patterson
|
85ce0bb472 | ||
|
m0duspwnens
|
b0bd64bc10 | ||
|
Josh Brower
|
17dd21703d | ||
|
m0duspwnens
|
767c922083 | ||
|
Josh Brower
|
a57ba7e35d | ||
|
Josh Brower
|
81c1678ec7 | ||
|
m0duspwnens
|
1593da4597 | ||
|
m0duspwnens
|
8359f1983c | ||
|
Josh Brower
|
87a20ffede | ||
|
m0duspwnens
|
c597766390 | ||
|
Mike Reeves
|
3d10a60502 | ||
|
Mike Reeves
|
220c534ad4 | ||
|
Mike Reeves
|
c7604e893e | ||
|
Josh Brower
|
b56486d88e | ||
|
Josh Brower
|
c99f19251b | ||
|
Josh Brower
|
544fa824ea | ||
|
Mike Reeves
|
dd034edad6 | ||
|
Mike Reeves
|
2419cf86ee | ||
|
m0duspwnens
|
61f9573ace | ||
|
Mike Reeves
|
7595072e85 | ||
|
Mike Reeves
|
e60e21d9ff | ||
|
Jason Ertel
|
b46a5c4b2a | ||
|
Jason Ertel
|
40ff2677c4 | ||
|
m0duspwnens
|
80b40503fb | ||
|
m0duspwnens
|
6a501efa75 | ||
|
m0duspwnens
|
1f6463a9bb | ||
|
Mike Reeves
|
2d4f4791e0 | ||
|
Mike Reeves
|
102906f5dd | ||
|
Jason Ertel
|
6c151d3ebd | ||
|
Jason Ertel
|
17e6f5b899 | ||
|
Mike Reeves
|
a38495ce39 | ||
|
Mike Reeves
|
38629a7676 | ||
|
m0duspwnens
|
9a4ae2b832 | ||
|
m0duspwnens
|
3fdcb92dfe | ||
|
m0duspwnens
|
725f5414ba | ||
|
Jason Ertel
|
73aceb9697 | ||
|
Jason Ertel
|
03c89a02ad | ||
|
Jason Ertel
|
666d4ea260 | ||
|
Jason Ertel
|
4c58aa2ccf | ||
|
Mike Reeves
|
26619e5f8d | ||
|
bryant-treacle
|
57d90a62f7 | ||
|
bryant-treacle
|
a8b8a1d0b7 | ||
|
Mike Reeves
|
e4375a6568 | ||
|
Mike Reeves
|
b8f9a9a311 | ||
|
Mike Reeves
|
3d7f2bc691 | ||
|
Mike Reeves
|
e799edaf49 | ||
|
Mike Reeves
|
be003f7ee4 | ||
|
Mike Reeves
|
868cb8183c | ||
|
Mike Reeves
|
b3f94961ea | ||
|
bryant-treacle
|
12120e94c8 | ||
|
bryant-treacle
|
49a60bac76 | ||
|
bryant-treacle
|
f07f0775ac | ||
|
bryant-treacle
|
e93e58fedb | ||
|
Jason Ertel
|
8459054ff8 | ||
|
Jason Ertel
|
43ec897397 | ||
|
Mike Reeves
|
4b73f859d1 | ||
|
Jason Ertel
|
969cf25818 | ||
|
Jason Ertel
|
e25bbd8a0d | ||
|
Mike Reeves
|
5b11c41434 | ||
|
Mike Reeves
|
99f21ce46f | ||
|
Mike Reeves
|
9dc31b6db4 | ||
|
Mike Reeves
|
083d96fab2 | ||
|
Mike Reeves
|
f21e717dcd | ||
|
Mike Reeves
|
87e9d2997b | ||
|
Josh Patterson
|
288b5ac4d2 | ||
|
m0duspwnens
|
533c3b7569 | ||
|
weslambert
|
32874d2e9d | ||
|
Wes
|
fca7753f73 | ||
|
Doug Burks
|
fcdb02d61e | ||
|
Doug Burks
|
4dcc79d245 | ||
|
weslambert
|
6c7b4e5492 | ||
|
Wes
|
a341f1b7b7 | ||
|
weslambert
|
01bd3545d0 | ||
|
Wes
|
d823d5dcc9 | ||
|
Josh Patterson
|
9fed2ac616 | ||
|
m0duspwnens
|
d5ab8ff191 | ||
|
m0duspwnens
|
2b28283095 | ||
|
Josh Brower
|
499b889b56 | ||
|
Josh Brower
|
aa5063c5df | ||
|
m0duspwnens
|
9f07388fa4 | ||
|
m0duspwnens
|
cd674947bb | ||
|
m0duspwnens
|
976ad4152d | ||
|
Josh Brower
|
2633f348ac | ||
|
Josh Brower
|
1ab72e9288 | ||
|
Josh Brower
|
ef92fba867 | ||
|
Josh Brower
|
36c96c4beb | ||
|
Josh Brower
|
d79ad53daf | ||
|
Josh Brower
|
4c4b873eca | ||
|
Josh Patterson
|
a062939705 | ||
|
Jason Ertel
|
3f14885539 | ||
|
Jason Ertel
|
393077ba9e | ||
|
m0duspwnens
|
b0f9585da1 | ||
|
m0duspwnens
|
7c8ba04820 | ||
|
Josh Brower
|
31f83c6dee | ||
|
Josh Brower
|
8cccaef664 | ||
|
Josh Brower
|
1944d09978 | ||
|
Josh Brower
|
a7d282b412 | ||
|
Jason Ertel
|
aade62491c | ||
|
Jason Ertel
|
b901555793 | ||
|
Josh Patterson
|
debe146dcf | ||
|
Josh Patterson
|
c8ef8cc88e | ||
|
Jason Ertel
|
9bd176621d | ||
|
Jason Ertel
|
05baaacc83 | ||
|
Jason Ertel
|
9bc44c122f | ||
|
Jason Ertel
|
1fdd8acd0c | ||
|
Josh Brower
|
92a6eac976 | ||
|
Jason Ertel
|
dc227df229 | ||
|
Jason Ertel
|
ff35a58f3f | ||
|
Josh Patterson
|
64fde6b02e | ||
|
m0duspwnens
|
1047462898 | ||
|
m0duspwnens
|
76ba89c356 | ||
|
weslambert
|
f3b4ee6a0b | ||
|
Wes
|
d6421ee7cc | ||
|
Doug Burks
|
148ef5833e | ||
|
Doug Burks
|
a67cbb3276 | ||
|
m0duspwnens
|
0485c83388 | ||
|
Jason Ertel
|
a8d3363a6f | ||
|
Jason Ertel
|
dba7b84adb | ||
|
Josh Brower
|
2567ceea74 | ||
|
Josh Brower
|
4ec31dbf35 | ||
|
m0duspwnens
|
e4e326cd06 | ||
|
m0duspwnens
|
0d17f4f486 | ||
|
Mike Reeves
|
7838393b9f | ||
|
m0duspwnens
|
c90c72dbba | ||
|
Mike Reeves
|
04eb73ac27 | ||
|
m0duspwnens
|
de082f6100 | ||
|
weslambert
|
2c44c8e468 | ||
|
Wes
|
06b60ca96b | ||
|
Wes
|
4d64a9777e | ||
|
m0duspwnens
|
26a12477ac | ||
|
weslambert
|
43447e5df5 | ||
|
m0duspwnens
|
c66f595666 | ||
|
m0duspwnens
|
ad64b873c0 | ||
|
Wes
|
c6be0a48a1 | ||
|
weslambert
|
5eb0364a98 | ||
|
Wes
|
8d0074c712 | ||
|
Jason Ertel
|
3883a89212 | ||
|
Jason Ertel
|
cfa61a6c26 | ||
|
Jason Ertel
|
7f28cdd2a3 | ||
|
m0duspwnens
|
9ea3eaafae | ||
|
m0duspwnens
|
16249cc80d | ||
|
m0duspwnens
|
2589670755 | ||
|
Josh Brower
|
17bc96c3b3 | ||
|
Josh Patterson
|
b87ee4904f | ||
|
m0duspwnens
|
7519a8c39d | ||
|
m0duspwnens
|
df4bf95b93 | ||
|
m0duspwnens
|
602e00058a | ||
|
Josh Patterson
|
6aba7b6bcf | ||
|
Josh Patterson
|
ff7aaa95e1 | ||
|
m0duspwnens
|
f166919160 | ||
|
m0duspwnens
|
aecbfd28ee | ||
|
m0duspwnens
|
b24e3ff6c4 | ||
|
Josh Brower
|
cda67b2894 | ||
|
m0duspwnens
|
6040c5062b | ||
|
m0duspwnens
|
d83266c546 | ||
|
m0duspwnens
|
6039a1430e | ||
|
Josh Brower
|
c2d4e870c8 | ||
|
Josh Patterson
|
1faceddc40 | ||
|
Josh Patterson
|
471f467e63 | ||
|
m0duspwnens
|
a0d8be4dc6 | ||
|
Josh Brower
|
035451cdb8 | ||
|
Josh Brower
|
af392681e3 | ||
|
Josh Brower
|
a0bb6a700a | ||
|
Josh Brower
|
ad000550a6 | ||
|
m0duspwnens
|
0fc6a74b6d | ||
|
m0duspwnens
|
0b96635bcc | ||
|
Doug Burks
|
5b2e39f80d | ||
|
Doug Burks
|
a8b6470a14 | ||
|
Doug Burks
|
e945f1c38f | ||
|
Doug Burks
|
d0dff9572d | ||
|
Doug Burks
|
68e8c159ce | ||
|
Josh Brower
|
a8038c90ce | ||
|
Josh Brower
|
91c990e30a | ||
|
Josh Brower
|
b6b49c876b | ||
|
Doug Burks
|
cf98a95dd1 | ||
|
Doug Burks
|
921e79c56c | ||
|
weslambert
|
2cfbf30f05 | ||
|
weslambert
|
3e08506c4e | ||
|
Wes
|
d4cba6908e | ||
|
Wes
|
dfd3456343 | ||
|
Wes
|
3cd1598067 | ||
|
m0duspwnens
|
1be86cdf8e | ||
|
Mike Reeves
|
bdae8d5017 | ||
|
Mike Reeves
|
d5e17da9d3 | ||
|
Josh Brower
|
e4b10aa28c | ||
|
Josh Brower
|
1c1b079058 | ||
|
Josh Brower
|
967a0807ad | ||
|
Josh Brower
|
b8d8a5fd6b | ||
|
Josh Brower
|
18a54b86f4 | ||
|
Josh Brower
|
17af095e14 | ||
|
Josh Brower
|
a71cbcfc9b | ||
|
Josh Brower
|
29aa6dceed | ||
|
Josh Brower
|
81ee333b07 |
No files matched your search
@@ -1,47 +1,47 @@
|
||||
### 2.3.120-20220425 ISO image built on 2022/04/25
|
||||
### 2.4.3-20230711 ISO image built on 2023/07/11
|
||||
|
||||
|
||||
|
||||
### Download and Verify
|
||||
|
||||
2.3.120-20220425 ISO image:
|
||||
https://download.securityonion.net/file/securityonion/securityonion-2.3.120-20220425.iso
|
||||
2.4.3-20230711 ISO image:
|
||||
https://download.securityonion.net/file/securityonion/securityonion-2.4.3-20230711.iso
|
||||
|
||||
MD5: C99729E452B064C471BEF04532F28556
|
||||
SHA1: 60BF07D5347C24568C7B793BFA9792E98479CFBF
|
||||
SHA256: CD17D0D7CABE21D45FA45E1CF91C5F24EB9608C79FF88480134E5592AFDD696E
|
||||
MD5: F481ED39E02A5AF05EB50D319D97A6C7
|
||||
SHA1: 20F9BAA8F73A44C21A8DFE81F36247BCF33CEDA6
|
||||
SHA256: D805522E02CD4941641385F6FF86FAAC240DA6C5FD98F78460348632C7C631B0
|
||||
|
||||
Signature for ISO image:
|
||||
https://github.com/Security-Onion-Solutions/securityonion/raw/master/sigs/securityonion-2.3.120-20220425.iso.sig
|
||||
https://github.com/Security-Onion-Solutions/securityonion/raw/2.4/main/sigs/securityonion-2.4.3-20230711.iso.sig
|
||||
|
||||
Signing key:
|
||||
https://raw.githubusercontent.com/Security-Onion-Solutions/securityonion/master/KEYS
|
||||
https://raw.githubusercontent.com/Security-Onion-Solutions/securityonion/2.4/main/KEYS
|
||||
|
||||
For example, here are the steps you can use on most Linux distributions to download and verify our Security Onion ISO image.
|
||||
|
||||
Download and import the signing key:
|
||||
```
|
||||
wget https://raw.githubusercontent.com/Security-Onion-Solutions/securityonion/master/KEYS -O - | gpg --import -
|
||||
wget https://raw.githubusercontent.com/Security-Onion-Solutions/securityonion/2.4/main/KEYS -O - | gpg --import -
|
||||
```
|
||||
|
||||
Download the signature file for the ISO:
|
||||
```
|
||||
wget https://github.com/Security-Onion-Solutions/securityonion/raw/master/sigs/securityonion-2.3.120-20220425.iso.sig
|
||||
wget https://github.com/Security-Onion-Solutions/securityonion/raw/2.4/main/sigs/securityonion-2.4.3-20230711.iso.sig
|
||||
```
|
||||
|
||||
Download the ISO image:
|
||||
```
|
||||
wget https://download.securityonion.net/file/securityonion/securityonion-2.3.120-20220425.iso
|
||||
wget https://download.securityonion.net/file/securityonion/securityonion-2.4.3-20230711.iso
|
||||
```
|
||||
|
||||
Verify the downloaded ISO image using the signature file:
|
||||
```
|
||||
gpg --verify securityonion-2.3.120-20220425.iso.sig securityonion-2.3.120-20220425.iso
|
||||
gpg --verify securityonion-2.4.3-20230711.iso.sig securityonion-2.4.3-20230711.iso
|
||||
```
|
||||
|
||||
The output should show "Good signature" and the Primary key fingerprint should match what's shown below:
|
||||
```
|
||||
gpg: Signature made Mon 25 Apr 2022 08:20:40 AM EDT using RSA key ID FE507013
|
||||
gpg: Signature made Tue 11 Jul 2023 06:23:37 PM EDT using RSA key ID FE507013
|
||||
gpg: Good signature from "Security Onion Solutions, LLC <info@securityonionsolutions.com>"
|
||||
gpg: WARNING: This key is not certified with a trusted signature!
|
||||
gpg: There is no indication that the signature belongs to the owner.
|
||||
@@ -49,4 +49,4 @@ Primary key fingerprint: C804 A93D 36BE 0C73 3EA1 9644 7C10 60B7 FE50 7013
|
||||
```
|
||||
|
||||
Once you've verified the ISO image, you're ready to proceed to our Installation guide:
|
||||
https://docs.securityonion.net/en/2.3/installation.html
|
||||
https://docs.securityonion.net/en/2.4/installation.html
|
||||
@@ -1,20 +1,26 @@
|
||||
## Security Onion 2.4
|
||||
## Security Onion 2.4 Beta 4
|
||||
|
||||
Security Onion 2.4 is here!
|
||||
Security Onion 2.4 Beta 4 is here!
|
||||
|
||||
## Screenshots
|
||||
|
||||
Alerts
|
||||

|
||||
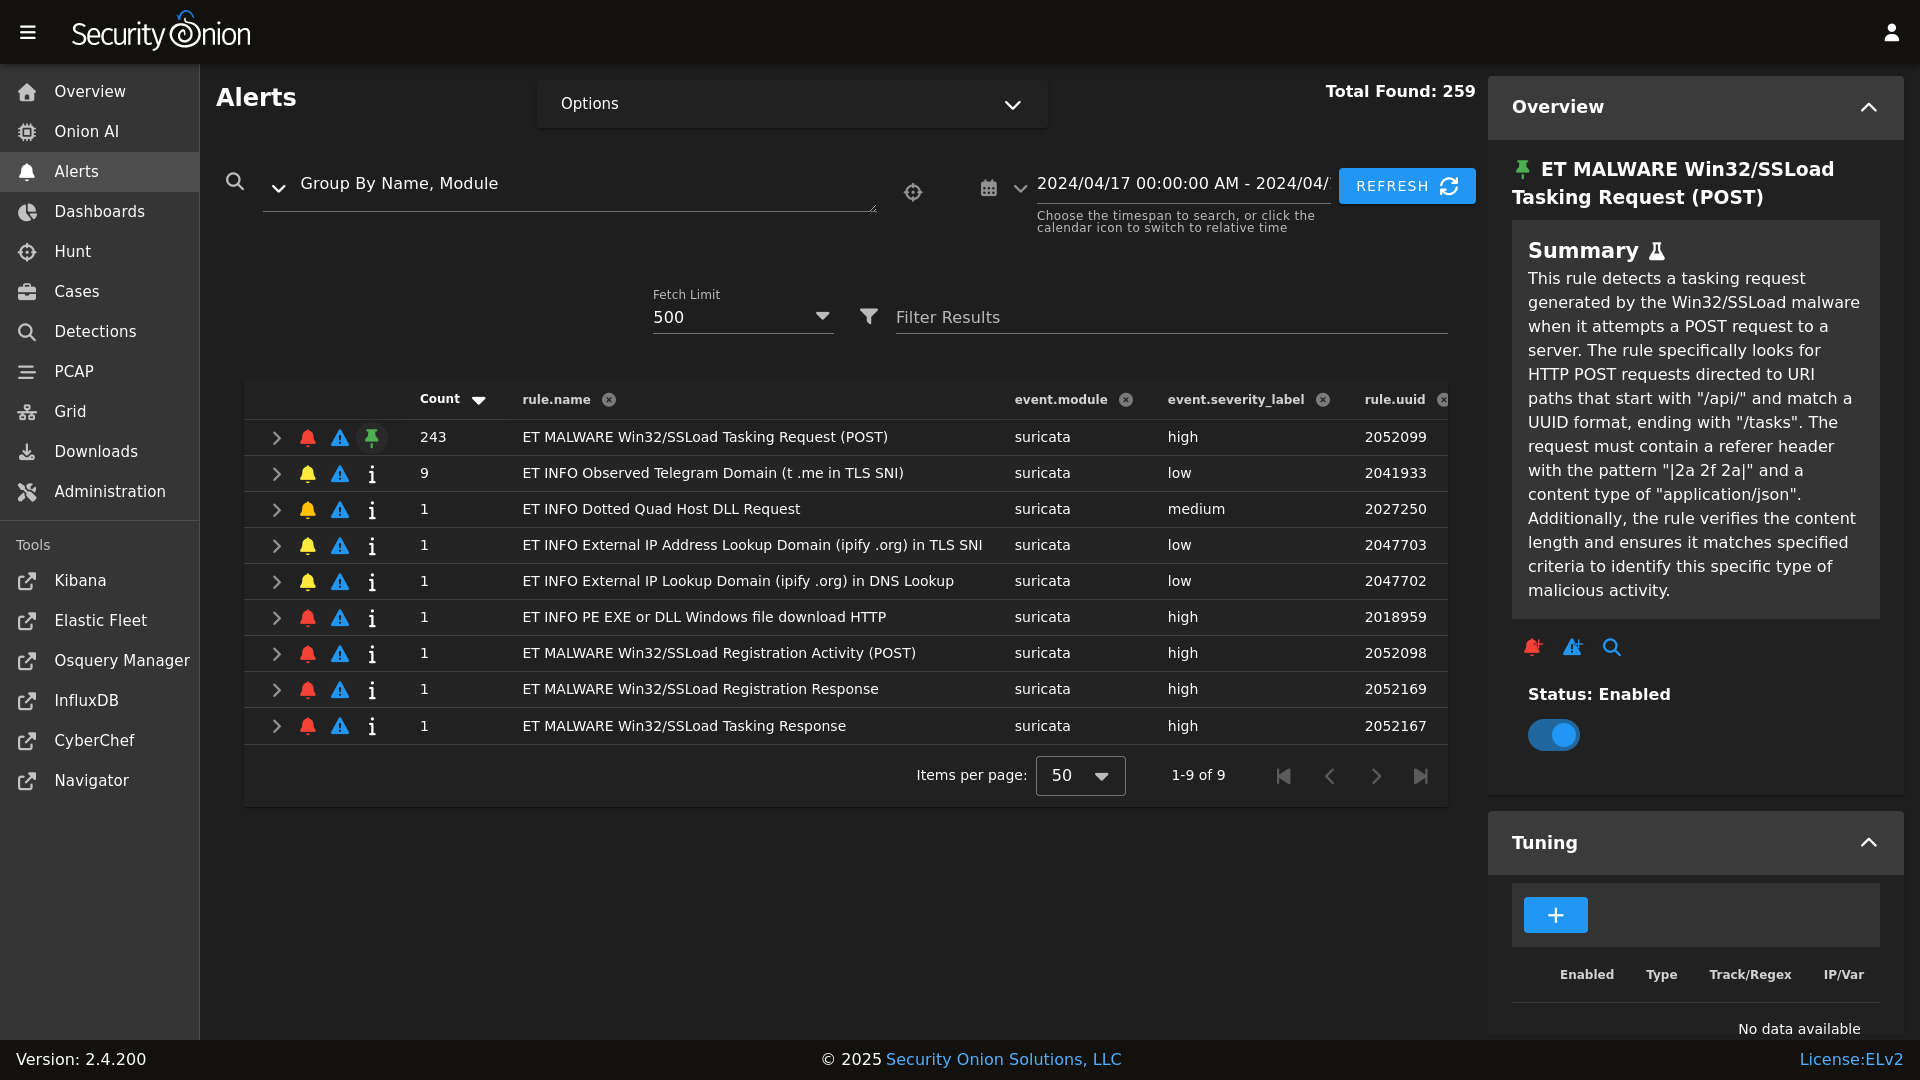
|
||||
|
||||
Dashboards
|
||||

|
||||

|
||||
|
||||
Hunt
|
||||

|
||||

|
||||
|
||||
Cases
|
||||

|
||||
PCAP
|
||||

|
||||
|
||||
Grid
|
||||

|
||||
|
||||
Config
|
||||

|
||||
|
||||
### Release Notes
|
||||
|
||||
|
||||
@@ -1,13 +0,0 @@
|
||||
logrotate:
|
||||
conf: |
|
||||
daily
|
||||
rotate 14
|
||||
missingok
|
||||
copytruncate
|
||||
compress
|
||||
create
|
||||
extension .log
|
||||
dateext
|
||||
dateyesterday
|
||||
group_conf: |
|
||||
su root socore
|
||||
@@ -1,42 +0,0 @@
|
||||
logstash:
|
||||
pipelines:
|
||||
helix:
|
||||
config:
|
||||
- so/0010_input_hhbeats.conf
|
||||
- so/1033_preprocess_snort.conf
|
||||
- so/1100_preprocess_bro_conn.conf
|
||||
- so/1101_preprocess_bro_dhcp.conf
|
||||
- so/1102_preprocess_bro_dns.conf
|
||||
- so/1103_preprocess_bro_dpd.conf
|
||||
- so/1104_preprocess_bro_files.conf
|
||||
- so/1105_preprocess_bro_ftp.conf
|
||||
- so/1106_preprocess_bro_http.conf
|
||||
- so/1107_preprocess_bro_irc.conf
|
||||
- so/1108_preprocess_bro_kerberos.conf
|
||||
- so/1109_preprocess_bro_notice.conf
|
||||
- so/1110_preprocess_bro_rdp.conf
|
||||
- so/1111_preprocess_bro_signatures.conf
|
||||
- so/1112_preprocess_bro_smtp.conf
|
||||
- so/1113_preprocess_bro_snmp.conf
|
||||
- so/1114_preprocess_bro_software.conf
|
||||
- so/1115_preprocess_bro_ssh.conf
|
||||
- so/1116_preprocess_bro_ssl.conf
|
||||
- so/1117_preprocess_bro_syslog.conf
|
||||
- so/1118_preprocess_bro_tunnel.conf
|
||||
- so/1119_preprocess_bro_weird.conf
|
||||
- so/1121_preprocess_bro_mysql.conf
|
||||
- so/1122_preprocess_bro_socks.conf
|
||||
- so/1123_preprocess_bro_x509.conf
|
||||
- so/1124_preprocess_bro_intel.conf
|
||||
- so/1125_preprocess_bro_modbus.conf
|
||||
- so/1126_preprocess_bro_sip.conf
|
||||
- so/1127_preprocess_bro_radius.conf
|
||||
- so/1128_preprocess_bro_pe.conf
|
||||
- so/1129_preprocess_bro_rfb.conf
|
||||
- so/1130_preprocess_bro_dnp3.conf
|
||||
- so/1131_preprocess_bro_smb_files.conf
|
||||
- so/1132_preprocess_bro_smb_mapping.conf
|
||||
- so/1133_preprocess_bro_ntlm.conf
|
||||
- so/1134_preprocess_bro_dce_rpc.conf
|
||||
- so/8001_postprocess_common_ip_augmentation.conf
|
||||
- so/9997_output_helix.conf.jinja
|
||||
@@ -4,6 +4,7 @@ logstash:
|
||||
- 0.0.0.0:3765:3765
|
||||
- 0.0.0.0:5044:5044
|
||||
- 0.0.0.0:5055:5055
|
||||
- 0.0.0.0:5056:5056
|
||||
- 0.0.0.0:5644:5644
|
||||
- 0.0.0.0:6050:6050
|
||||
- 0.0.0.0:6051:6051
|
||||
|
||||
@@ -1,8 +0,0 @@
|
||||
logstash:
|
||||
pipelines:
|
||||
manager:
|
||||
config:
|
||||
- so/0011_input_endgame.conf
|
||||
- so/0012_input_elastic_agent.conf
|
||||
- so/9999_output_redis.conf.jinja
|
||||
|
||||
@@ -2,7 +2,7 @@
|
||||
{% set cached_grains = salt.saltutil.runner('cache.grains', tgt='*') %}
|
||||
{% for minionid, ip in salt.saltutil.runner(
|
||||
'mine.get',
|
||||
tgt='G@role:so-manager or G@role:so-managersearch or G@role:so-standalone or G@role:so-searchnode or G@role:so-heavynode or G@role:so-receiver or G@role:so-helix ',
|
||||
tgt='G@role:so-manager or G@role:so-managersearch or G@role:so-standalone or G@role:so-searchnode or G@role:so-heavynode or G@role:so-receiver or G@role:so-fleet ',
|
||||
fun='network.ip_addrs',
|
||||
tgt_type='compound') | dictsort()
|
||||
%}
|
||||
|
||||
@@ -1,8 +0,0 @@
|
||||
logstash:
|
||||
pipelines:
|
||||
receiver:
|
||||
config:
|
||||
- so/0011_input_endgame.conf
|
||||
- so/0012_input_elastic_agent.conf
|
||||
- so/9999_output_redis.conf.jinja
|
||||
|
||||
@@ -1,7 +0,0 @@
|
||||
logstash:
|
||||
pipelines:
|
||||
search:
|
||||
config:
|
||||
- so/0900_input_redis.conf.jinja
|
||||
- so/9805_output_elastic_agent.conf.jinja
|
||||
- so/9900_output_endgame.conf.jinja
|
||||
@@ -0,0 +1,14 @@
|
||||
# Copyright Jason Ertel (github.com/jertel).
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with
|
||||
# the Elastic License 2.0.
|
||||
|
||||
# Note: Per the Elastic License 2.0, the second limitation states:
|
||||
#
|
||||
# "You may not move, change, disable, or circumvent the license key functionality
|
||||
# in the software, and you may not remove or obscure any functionality in the
|
||||
# software that is protected by the license key."
|
||||
|
||||
# This file is generated by Security Onion and contains a list of license-enabled features.
|
||||
features: []
|
||||
+141
-65
@@ -1,44 +1,26 @@
|
||||
base:
|
||||
'*':
|
||||
- patch.needs_restarting
|
||||
- ntp.soc_ntp
|
||||
- ntp.adv_ntp
|
||||
- logrotate
|
||||
- global.soc_global
|
||||
- global.adv_global
|
||||
- docker.soc_docker
|
||||
- docker.adv_docker
|
||||
- firewall.soc_firewall
|
||||
- firewall.adv_firewall
|
||||
- influxdb.token
|
||||
- logrotate.soc_logrotate
|
||||
- logrotate.adv_logrotate
|
||||
- nginx.soc_nginx
|
||||
- nginx.adv_nginx
|
||||
- node_data.ips
|
||||
- ntp.soc_ntp
|
||||
- ntp.adv_ntp
|
||||
- patch.needs_restarting
|
||||
- patch.soc_patch
|
||||
- patch.adv_patch
|
||||
- sensoroni.soc_sensoroni
|
||||
- sensoroni.adv_sensoroni
|
||||
- telegraf.soc_telegraf
|
||||
- telegraf.adv_telegraf
|
||||
- influxdb.token
|
||||
- node_data.ips
|
||||
|
||||
'* and not *_eval and not *_import':
|
||||
- logstash.nodes
|
||||
|
||||
'*_eval or *_heavynode or *_sensor or *_standalone or *_import':
|
||||
- match: compound
|
||||
- zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
|
||||
'*_managersearch or *_heavynode':
|
||||
- match: compound
|
||||
- logstash
|
||||
- logstash.manager
|
||||
- logstash.search
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticsearch.index_templates
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
|
||||
'*_manager':
|
||||
- logstash
|
||||
- logstash.manager
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticsearch.index_templates
|
||||
|
||||
'*_manager or *_managersearch':
|
||||
- match: compound
|
||||
@@ -49,14 +31,20 @@ base:
|
||||
- kibana.secrets
|
||||
{% endif %}
|
||||
- secrets
|
||||
- soc_global
|
||||
- adv_global
|
||||
- manager.soc_manager
|
||||
- manager.adv_manager
|
||||
- idstools.soc_idstools
|
||||
- idstools.adv_idstools
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- soc.soc_soc
|
||||
- soc.adv_soc
|
||||
- soc.license
|
||||
- soctopus.soc_soctopus
|
||||
- soctopus.adv_soctopus
|
||||
- kibana.soc_kibana
|
||||
- kibana.adv_kibana
|
||||
- kratos.soc_kratos
|
||||
- kratos.adv_kratos
|
||||
- redis.soc_redis
|
||||
@@ -65,17 +53,31 @@ base:
|
||||
- influxdb.adv_influxdb
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
- elasticfleet.soc_elasticfleet
|
||||
- elasticfleet.adv_elasticfleet
|
||||
- elastalert.soc_elastalert
|
||||
- elastalert.adv_elastalert
|
||||
- backup.soc_backup
|
||||
- backup.adv_backup
|
||||
- firewall.soc_firewall
|
||||
- firewall.adv_firewall
|
||||
- curator.soc_curator
|
||||
- curator.adv_curator
|
||||
- soctopus.soc_soctopus
|
||||
- soctopus.adv_soctopus
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_sensor':
|
||||
- healthcheck.sensor
|
||||
- soc_global
|
||||
- adv_global
|
||||
- strelka.soc_strelka
|
||||
- strelka.adv_strelka
|
||||
- zeek.soc_zeek
|
||||
- zeek.adv_zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
- pcap.soc_pcap
|
||||
- pcap.adv_pcap
|
||||
- suricata.soc_suricata
|
||||
- suricata.adv_suricata
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
@@ -89,15 +91,28 @@ base:
|
||||
{% if salt['file.file_exists']('/opt/so/saltstack/local/pillar/kibana/secrets.sls') %}
|
||||
- kibana.secrets
|
||||
{% endif %}
|
||||
- soc_global
|
||||
- kratos.soc_kratos
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
- elasticfleet.soc_elasticfleet
|
||||
- elasticfleet.adv_elasticfleet
|
||||
- elastalert.soc_elastalert
|
||||
- elastalert.adv_elastalert
|
||||
- manager.soc_manager
|
||||
- manager.adv_manager
|
||||
- idstools.soc_idstools
|
||||
- idstools.adv_idstools
|
||||
- soc.soc_soc
|
||||
- soc.adv_soc
|
||||
- soc.license
|
||||
- soctopus.soc_soctopus
|
||||
- soctopus.adv_soctopus
|
||||
- kibana.soc_kibana
|
||||
- kibana.adv_kibana
|
||||
- strelka.soc_strelka
|
||||
- strelka.adv_strelka
|
||||
- curator.soc_curator
|
||||
- curator.adv_curator
|
||||
- kratos.soc_kratos
|
||||
- kratos.adv_kratos
|
||||
- redis.soc_redis
|
||||
@@ -106,15 +121,19 @@ base:
|
||||
- influxdb.adv_influxdb
|
||||
- backup.soc_backup
|
||||
- backup.adv_backup
|
||||
- firewall.soc_firewall
|
||||
- firewall.adv_firewall
|
||||
- zeek.soc_zeek
|
||||
- zeek.adv_zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
- pcap.soc_pcap
|
||||
- pcap.adv_pcap
|
||||
- suricata.soc_suricata
|
||||
- suricata.adv_suricata
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_standalone':
|
||||
- logstash
|
||||
- logstash.manager
|
||||
- logstash.search
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticsearch.index_templates
|
||||
@@ -126,7 +145,6 @@ base:
|
||||
{% endif %}
|
||||
- secrets
|
||||
- healthcheck.standalone
|
||||
- soc_global
|
||||
- idstools.soc_idstools
|
||||
- idstools.adv_idstools
|
||||
- kratos.soc_kratos
|
||||
@@ -137,51 +155,82 @@ base:
|
||||
- influxdb.adv_influxdb
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
- elasticfleet.soc_elasticfleet
|
||||
- elasticfleet.adv_elasticfleet
|
||||
- elastalert.soc_elastalert
|
||||
- elastalert.adv_elastalert
|
||||
- manager.soc_manager
|
||||
- manager.adv_manager
|
||||
- soc.soc_soc
|
||||
- soc.adv_soc
|
||||
- soc.license
|
||||
- soctopus.soc_soctopus
|
||||
- soctopus.adv_soctopus
|
||||
- kibana.soc_kibana
|
||||
- kibana.adv_kibana
|
||||
- strelka.soc_strelka
|
||||
- strelka.adv_strelka
|
||||
- curator.soc_curator
|
||||
- curator.adv_curator
|
||||
- backup.soc_backup
|
||||
- backup.adv_backup
|
||||
- firewall.soc_firewall
|
||||
- firewall.adv_firewall
|
||||
- zeek.soc_zeek
|
||||
- zeek.adv_zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
- pcap.soc_pcap
|
||||
- pcap.adv_pcap
|
||||
- suricata.soc_suricata
|
||||
- suricata.adv_suricata
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_heavynode':
|
||||
- elasticsearch.auth
|
||||
- soc_global
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
- curator.soc_curator
|
||||
- curator.adv_curator
|
||||
- redis.soc_redis
|
||||
- redis.adv_redis
|
||||
- zeek.soc_zeek
|
||||
- zeek.adv_zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
- pcap.soc_pcap
|
||||
- pcap.adv_pcap
|
||||
- suricata.soc_suricata
|
||||
- suricata.adv_suricata
|
||||
- strelka.soc_strelka
|
||||
- strelka.adv_strelka
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_idh':
|
||||
- soc_global
|
||||
- adv_global
|
||||
- idh.soc_idh
|
||||
- idh.adv_idh
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_searchnode':
|
||||
- logstash
|
||||
- logstash.search
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticsearch.index_templates
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
{% if salt['file.file_exists']('/opt/so/saltstack/local/pillar/elasticsearch/auth.sls') %}
|
||||
- elasticsearch.auth
|
||||
{% endif %}
|
||||
- redis.soc_redis
|
||||
- soc_global
|
||||
- adv_global
|
||||
- redis.adv_redis
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_receiver':
|
||||
- logstash
|
||||
- logstash.receiver
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
{% if salt['file.file_exists']('/opt/so/saltstack/local/pillar/elasticsearch/auth.sls') %}
|
||||
@@ -189,8 +238,6 @@ base:
|
||||
{% endif %}
|
||||
- redis.soc_redis
|
||||
- redis.adv_redis
|
||||
- soc_global
|
||||
- adv_global
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
@@ -206,11 +253,21 @@ base:
|
||||
- kratos.soc_kratos
|
||||
- elasticsearch.soc_elasticsearch
|
||||
- elasticsearch.adv_elasticsearch
|
||||
- elasticfleet.soc_elasticfleet
|
||||
- elasticfleet.adv_elasticfleet
|
||||
- elastalert.soc_elastalert
|
||||
- elastalert.adv_elastalert
|
||||
- manager.soc_manager
|
||||
- manager.adv_manager
|
||||
- soc.soc_soc
|
||||
- soc_global
|
||||
- adv_global
|
||||
- soc.adv_soc
|
||||
- soc.license
|
||||
- soctopus.soc_soctopus
|
||||
- soctopus.adv_soctopus
|
||||
- kibana.soc_kibana
|
||||
- kibana.adv_kibana
|
||||
- curator.soc_curator
|
||||
- curator.adv_curator
|
||||
- backup.soc_backup
|
||||
- backup.adv_backup
|
||||
- kratos.soc_kratos
|
||||
@@ -219,11 +276,30 @@ base:
|
||||
- redis.adv_redis
|
||||
- influxdb.soc_influxdb
|
||||
- influxdb.adv_influxdb
|
||||
- firewall.soc_firewall
|
||||
- firewall.adv_firewall
|
||||
- zeek.soc_zeek
|
||||
- zeek.adv_zeek
|
||||
- bpf.soc_bpf
|
||||
- bpf.adv_bpf
|
||||
- pcap.soc_pcap
|
||||
- pcap.adv_pcap
|
||||
- suricata.soc_suricata
|
||||
- suricata.adv_suricata
|
||||
- strelka.soc_strelka
|
||||
- strelka.adv_strelka
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_workstation':
|
||||
'*_fleet':
|
||||
- backup.soc_backup
|
||||
- backup.adv_backup
|
||||
- logstash.nodes
|
||||
- logstash.soc_logstash
|
||||
- logstash.adv_logstash
|
||||
- elasticfleet.soc_elasticfleet
|
||||
- elasticfleet.adv_elasticfleet
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
|
||||
'*_desktop':
|
||||
- minions.{{ grains.id }}
|
||||
- minions.adv_{{ grains.id }}
|
||||
@@ -3,16 +3,6 @@
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
{% set ZEEKVER = salt['pillar.get']('global:mdengine', '') %}
|
||||
{% set PLAYBOOK = salt['pillar.get']('manager:playbook', '0') %}
|
||||
{% set ELASTALERT = salt['pillar.get']('elastalert:enabled', True) %}
|
||||
{% set ELASTICSEARCH = salt['pillar.get']('elasticsearch:enabled', True) %}
|
||||
{% set KIBANA = salt['pillar.get']('kibana:enabled', True) %}
|
||||
{% set LOGSTASH = salt['pillar.get']('logstash:enabled', True) %}
|
||||
{% set CURATOR = salt['pillar.get']('curator:enabled', True) %}
|
||||
{% set REDIS = salt['pillar.get']('redis:enabled', True) %}
|
||||
{% set STRELKA = salt['pillar.get']('strelka:enabled', '0') %}
|
||||
{% set ISAIRGAP = salt['pillar.get']('global:airgap', False) %}
|
||||
{% import_yaml 'salt/minion.defaults.yaml' as saltversion %}
|
||||
{% set saltversion = saltversion.salt.minion.version %}
|
||||
@@ -35,6 +25,7 @@
|
||||
'soc',
|
||||
'kratos',
|
||||
'elasticfleet',
|
||||
'elastic-fleet-package-registry',
|
||||
'firewall',
|
||||
'idstools',
|
||||
'suricata.manager',
|
||||
@@ -55,23 +46,7 @@
|
||||
'pcap',
|
||||
'suricata',
|
||||
'healthcheck',
|
||||
'schedule',
|
||||
'tcpreplay',
|
||||
'docker_clean'
|
||||
],
|
||||
'so-helixsensor': [
|
||||
'salt.master',
|
||||
'ca',
|
||||
'ssl',
|
||||
'registry',
|
||||
'telegraf',
|
||||
'firewall',
|
||||
'idstools',
|
||||
'suricata.manager',
|
||||
'zeek',
|
||||
'redis',
|
||||
'elasticsearch',
|
||||
'logstash',
|
||||
'elasticagent',
|
||||
'schedule',
|
||||
'tcpreplay',
|
||||
'docker_clean'
|
||||
@@ -105,7 +80,8 @@
|
||||
'schedule',
|
||||
'tcpreplay',
|
||||
'docker_clean',
|
||||
'elasticfleet'
|
||||
'elasticfleet',
|
||||
'elastic-fleet-package-registry'
|
||||
],
|
||||
'so-manager': [
|
||||
'salt.master',
|
||||
@@ -119,6 +95,7 @@
|
||||
'soc',
|
||||
'kratos',
|
||||
'elasticfleet',
|
||||
'elastic-fleet-package-registry',
|
||||
'firewall',
|
||||
'idstools',
|
||||
'suricata.manager',
|
||||
@@ -137,6 +114,7 @@
|
||||
'influxdb',
|
||||
'soc',
|
||||
'kratos',
|
||||
'elastic-fleet-package-registry',
|
||||
'elasticfleet',
|
||||
'firewall',
|
||||
'manager',
|
||||
@@ -166,6 +144,7 @@
|
||||
'influxdb',
|
||||
'soc',
|
||||
'kratos',
|
||||
'elastic-fleet-package-registry',
|
||||
'elasticfleet',
|
||||
'firewall',
|
||||
'idstools',
|
||||
@@ -191,6 +170,16 @@
|
||||
'tcpreplay',
|
||||
'docker_clean'
|
||||
],
|
||||
'so-fleet': [
|
||||
'ssl',
|
||||
'telegraf',
|
||||
'firewall',
|
||||
'logstash',
|
||||
'healthcheck',
|
||||
'schedule',
|
||||
'elasticfleet',
|
||||
'docker_clean'
|
||||
],
|
||||
'so-receiver': [
|
||||
'ssl',
|
||||
'telegraf',
|
||||
@@ -198,31 +187,31 @@
|
||||
'schedule',
|
||||
'docker_clean'
|
||||
],
|
||||
'so-workstation': [
|
||||
'so-desktop': [
|
||||
],
|
||||
}, grain='role') %}
|
||||
|
||||
{% if (PLAYBOOK != 0) and grains.role in ['so-eval', 'so-manager', 'so-managersearch', 'so-standalone'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-managersearch', 'so-standalone'] %}
|
||||
{% do allowed_states.append('mysql') %}
|
||||
{% endif %}
|
||||
|
||||
{%- if ZEEKVER != 'SURICATA' and grains.role in ['so-sensor', 'so-eval', 'so-standalone', 'so-heavynode'] %}
|
||||
{%- if grains.role in ['so-sensor', 'so-eval', 'so-standalone', 'so-heavynode'] %}
|
||||
{% do allowed_states.append('zeek') %}
|
||||
{%- endif %}
|
||||
|
||||
{% if STRELKA and grains.role in ['so-sensor', 'so-eval', 'so-standalone', 'so-heavynode'] %}
|
||||
{% if grains.role in ['so-sensor', 'so-eval', 'so-standalone', 'so-heavynode'] %}
|
||||
{% do allowed_states.append('strelka') %}
|
||||
{% endif %}
|
||||
|
||||
{% if ELASTICSEARCH and grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-searchnode', 'so-managersearch', 'so-heavynode', 'so-import'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-searchnode', 'so-managersearch', 'so-heavynode', 'so-import'] %}
|
||||
{% do allowed_states.append('elasticsearch') %}
|
||||
{% endif %}
|
||||
|
||||
{% if ELASTICSEARCH and grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch', 'so-import'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch', 'so-import'] %}
|
||||
{% do allowed_states.append('elasticsearch.auth') %}
|
||||
{% endif %}
|
||||
|
||||
{% if KIBANA and grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch', 'so-import'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch', 'so-import'] %}
|
||||
{% do allowed_states.append('kibana') %}
|
||||
{% do allowed_states.append('kibana.secrets') %}
|
||||
{% endif %}
|
||||
@@ -231,23 +220,19 @@
|
||||
{% do allowed_states.append('curator') %}
|
||||
{% endif %}
|
||||
|
||||
{% if ELASTALERT and grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch'] %}
|
||||
{% do allowed_states.append('elastalert') %}
|
||||
{% endif %}
|
||||
|
||||
{% if (PLAYBOOK !=0) and grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch'] %}
|
||||
{% if grains.role in ['so-eval', 'so-manager', 'so-standalone', 'so-managersearch'] %}
|
||||
{% do allowed_states.append('playbook') %}
|
||||
{% endif %}
|
||||
|
||||
{% if (PLAYBOOK !=0) and grains.role in ['so-eval'] %}
|
||||
{% do allowed_states.append('redis') %}
|
||||
{% endif %}
|
||||
|
||||
{% if LOGSTASH and grains.role in ['so-helixsensor', 'so-manager', 'so-standalone', 'so-searchnode', 'so-managersearch', 'so-heavynode', 'so-receiver'] %}
|
||||
{% if grains.role in ['so-manager', 'so-standalone', 'so-searchnode', 'so-managersearch', 'so-heavynode', 'so-receiver'] %}
|
||||
{% do allowed_states.append('logstash') %}
|
||||
{% endif %}
|
||||
|
||||
{% if REDIS and grains.role in ['so-manager', 'so-standalone', 'so-managersearch', 'so-heavynode', 'so-receiver'] %}
|
||||
{% if grains.role in ['so-manager', 'so-standalone', 'so-managersearch', 'so-heavynode', 'so-receiver', 'so-eval'] %}
|
||||
{% do allowed_states.append('redis') %}
|
||||
{% endif %}
|
||||
|
||||
|
||||
@@ -25,6 +25,7 @@ config_backup_script:
|
||||
so_config_backup:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-config-backup > /dev/null 2>&1
|
||||
- identifier: so_config_backup
|
||||
- user: root
|
||||
- minute: '1'
|
||||
- hour: '0'
|
||||
|
||||
+2
-3
@@ -18,9 +18,8 @@ include:
|
||||
pki_private_key:
|
||||
x509.private_key_managed:
|
||||
- name: /etc/pki/ca.key
|
||||
- bits: 4096
|
||||
- keysize: 4096
|
||||
- passphrase:
|
||||
- cipher: aes_256_cbc
|
||||
- backup: True
|
||||
{% if salt['file.file_exists']('/etc/pki/ca.key') -%}
|
||||
- prereq:
|
||||
@@ -39,7 +38,7 @@ pki_public_ca_crt:
|
||||
- keyUsage: "critical cRLSign, keyCertSign"
|
||||
- extendedkeyUsage: "serverAuth, clientAuth"
|
||||
- subjectKeyIdentifier: hash
|
||||
- authorityKeyIdentifier: keyid,issuer:always
|
||||
- authorityKeyIdentifier: keyid:always, issuer
|
||||
- days_valid: 3650
|
||||
- days_remaining: 0
|
||||
- backup: True
|
||||
|
||||
@@ -1,2 +0,0 @@
|
||||
#!/bin/bash
|
||||
/usr/sbin/logrotate -f /opt/so/conf/log-rotate.conf > /dev/null 2>&1
|
||||
@@ -1,2 +0,0 @@
|
||||
#!/bin/bash
|
||||
/usr/sbin/logrotate -f /opt/so/conf/sensor-rotate.conf > /dev/null 2>&1
|
||||
@@ -1,79 +0,0 @@
|
||||
The following GUI tools are available on the analyst workstation:
|
||||
|
||||
chromium
|
||||
url: https://www.chromium.org/Home
|
||||
To run chromium, click Applications > Internet > Chromium Web Browser
|
||||
|
||||
Wireshark
|
||||
url: https://www.wireshark.org/
|
||||
To run Wireshark, click Applications > Internet > Wireshark Network Analyzer
|
||||
|
||||
NetworkMiner
|
||||
url: https://www.netresec.com
|
||||
To run NetworkMiner, click Applications > Internet > NetworkMiner
|
||||
|
||||
The following CLI tools are available on the analyst workstation:
|
||||
|
||||
bit-twist
|
||||
url: http://bittwist.sourceforge.net
|
||||
To run bit-twist, open a terminal and type: bittwist -h
|
||||
|
||||
chaosreader
|
||||
url: http://chaosreader.sourceforge.net
|
||||
To run chaosreader, open a terminal and type: chaosreader -h
|
||||
|
||||
dnsiff
|
||||
url: https://www.monkey.org/~dugsong/dsniff/
|
||||
To run dsniff, open a terminal and type: dsniff -h
|
||||
|
||||
foremost
|
||||
url: http://foremost.sourceforge.net
|
||||
To run foremost, open a terminal and type: foremost -h
|
||||
|
||||
hping3
|
||||
url: http://www.hping.org/hping3.html
|
||||
To run hping3, open a terminal and type: hping3 -h
|
||||
|
||||
netsed
|
||||
url: http://silicone.homelinux.org/projects/netsed/
|
||||
To run netsed, open a terminal and type: netsed -h
|
||||
|
||||
ngrep
|
||||
url: https://github.com/jpr5/ngrep
|
||||
To run ngrep, open a terminal and type: ngrep -h
|
||||
|
||||
scapy
|
||||
url: http://www.secdev.org/projects/scapy/
|
||||
To run scapy, open a terminal and type: scapy
|
||||
|
||||
ssldump
|
||||
url: http://www.rtfm.com/ssldump/
|
||||
To run ssldump, open a terminal and type: ssldump -h
|
||||
|
||||
sslsplit
|
||||
url: https://github.com/droe/sslsplit
|
||||
To run sslsplit, open a terminal and type: sslsplit -h
|
||||
|
||||
tcpdump
|
||||
url: http://www.tcpdump.org
|
||||
To run tcpdump, open a terminal and type: tcpdump -h
|
||||
|
||||
tcpflow
|
||||
url: https://github.com/simsong/tcpflow
|
||||
To run tcpflow, open a terminal and type: tcpflow -h
|
||||
|
||||
tcpstat
|
||||
url: https://frenchfries.net/paul/tcpstat/
|
||||
To run tcpstat, open a terminal and type: tcpstat -h
|
||||
|
||||
tcptrace
|
||||
url: http://www.tcptrace.org
|
||||
To run tcptrace, open a terminal and type: tcptrace -h
|
||||
|
||||
tcpxtract
|
||||
url: http://tcpxtract.sourceforge.net/
|
||||
To run tcpxtract, open a terminal and type: tcpxtract -h
|
||||
|
||||
whois
|
||||
url: http://www.linux.it/~md/software/
|
||||
To run whois, open a terminal and type: whois -h
|
||||
@@ -1,37 +0,0 @@
|
||||
{%- set logrotate_conf = salt['pillar.get']('logrotate:conf') %}
|
||||
{%- set group_conf = salt['pillar.get']('logrotate:group_conf') %}
|
||||
|
||||
|
||||
/opt/so/log/aptcacher-ng/*.log
|
||||
/opt/so/log/idstools/*.log
|
||||
/opt/so/log/nginx/*.log
|
||||
/opt/so/log/soc/*.log
|
||||
/opt/so/log/kratos/*.log
|
||||
/opt/so/log/kibana/*.log
|
||||
/opt/so/log/influxdb/*.log
|
||||
/opt/so/log/elastalert/*.log
|
||||
/opt/so/log/soctopus/*.log
|
||||
/opt/so/log/curator/*.log
|
||||
/opt/so/log/fleet/*.log
|
||||
/opt/so/log/suricata/*.log
|
||||
/opt/so/log/mysql/*.log
|
||||
/opt/so/log/telegraf/*.log
|
||||
/opt/so/log/redis/*.log
|
||||
/opt/so/log/sensoroni/*.log
|
||||
/opt/so/log/stenographer/*.log
|
||||
/opt/so/log/salt/so-salt-minion-check
|
||||
/opt/so/log/salt/minion
|
||||
/opt/so/log/salt/master
|
||||
/opt/so/log/logscan/*.log
|
||||
/nsm/idh/*.log
|
||||
{
|
||||
{{ logrotate_conf | indent(width=4) }}
|
||||
}
|
||||
|
||||
# Playbook's log directory needs additional configuration
|
||||
# because Playbook requires a more permissive directory
|
||||
/opt/so/log/playbook/*.log
|
||||
{
|
||||
{{ logrotate_conf | indent(width=4) }}
|
||||
{{ group_conf | indent(width=4) }}
|
||||
}
|
||||
@@ -1,22 +0,0 @@
|
||||
/opt/so/log/sensor_clean.log
|
||||
{
|
||||
daily
|
||||
rotate 2
|
||||
missingok
|
||||
nocompress
|
||||
create
|
||||
sharedscripts
|
||||
}
|
||||
|
||||
/nsm/strelka/log/strelka.log
|
||||
{
|
||||
daily
|
||||
rotate 14
|
||||
missingok
|
||||
copytruncate
|
||||
compress
|
||||
create
|
||||
extension .log
|
||||
dateext
|
||||
dateyesterday
|
||||
}
|
||||
+33
-72
@@ -10,6 +10,10 @@ include:
|
||||
- manager.elasticsearch # needed for elastic_curl_config state
|
||||
{% endif %}
|
||||
|
||||
net.core.wmem_default:
|
||||
sysctl.present:
|
||||
- value: 26214400
|
||||
|
||||
# Remove variables.txt from /tmp - This is temp
|
||||
rmvariablesfile:
|
||||
file.absent:
|
||||
@@ -49,13 +53,12 @@ so-status.conf:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- unless: ls /opt/so/conf/so-status/so-status.conf
|
||||
|
||||
sosaltstackperms:
|
||||
socore_opso_perms:
|
||||
file.directory:
|
||||
- name: /opt/so/saltstack
|
||||
- name: /opt/so
|
||||
- user: 939
|
||||
- group: 939
|
||||
- dir_mode: 770
|
||||
|
||||
|
||||
so_log_perms:
|
||||
file.directory:
|
||||
- name: /opt/so/log
|
||||
@@ -97,6 +100,8 @@ alwaysupdated:
|
||||
Etc/UTC:
|
||||
timezone.system
|
||||
|
||||
# Sync curl configuration for Elasticsearch authentication
|
||||
{% if GLOBALS.role in ['so-eval', 'so-heavynode', 'so-import', 'so-manager', 'so-managersearch', 'so-searchnode', 'so-standalone'] %}
|
||||
elastic_curl_config:
|
||||
file.managed:
|
||||
- name: /opt/so/conf/elasticsearch/curl.config
|
||||
@@ -108,22 +113,25 @@ elastic_curl_config:
|
||||
- require:
|
||||
- file: elastic_curl_config_distributed
|
||||
{% endif %}
|
||||
{% endif %}
|
||||
|
||||
# Sync some Utilities
|
||||
utilsyncscripts:
|
||||
|
||||
common_sbin:
|
||||
file.recurse:
|
||||
- name: /usr/sbin
|
||||
- user: root
|
||||
- group: root
|
||||
- source: salt://common/tools/sbin
|
||||
- user: 939
|
||||
- group: 939
|
||||
- file_mode: 755
|
||||
|
||||
common_sbin_jinja:
|
||||
file.recurse:
|
||||
- name: /usr/sbin
|
||||
- source: salt://common/tools/sbin_jinja
|
||||
- user: 939
|
||||
- group: 939
|
||||
- file_mode: 755
|
||||
- template: jinja
|
||||
- source: salt://common/tools/sbin
|
||||
- exclude_pat:
|
||||
- so-common
|
||||
- so-firewall
|
||||
- so-image-common
|
||||
- soup
|
||||
- so-status
|
||||
|
||||
so-status_script:
|
||||
file.managed:
|
||||
@@ -133,60 +141,18 @@ so-status_script:
|
||||
|
||||
{% if GLOBALS.role in GLOBALS.sensor_roles %}
|
||||
# Add sensor cleanup
|
||||
/usr/sbin/so-sensor-clean:
|
||||
so-sensor-clean:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-sensor-clean
|
||||
- identifier: so-sensor-clean
|
||||
- user: root
|
||||
- minute: '*'
|
||||
- hour: '*'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
sensorrotatescript:
|
||||
file.managed:
|
||||
- name: /usr/local/bin/sensor-rotate
|
||||
- source: salt://common/cron/sensor-rotate
|
||||
- mode: 755
|
||||
|
||||
sensorrotateconf:
|
||||
file.managed:
|
||||
- name: /opt/so/conf/sensor-rotate.conf
|
||||
- source: salt://common/files/sensor-rotate.conf
|
||||
- mode: 644
|
||||
|
||||
/usr/local/bin/sensor-rotate:
|
||||
cron.present:
|
||||
- user: root
|
||||
- minute: '1'
|
||||
- hour: '0'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
{% endif %}
|
||||
|
||||
commonlogrotatescript:
|
||||
file.managed:
|
||||
- name: /usr/local/bin/common-rotate
|
||||
- source: salt://common/cron/common-rotate
|
||||
- mode: 755
|
||||
|
||||
commonlogrotateconf:
|
||||
file.managed:
|
||||
- name: /opt/so/conf/log-rotate.conf
|
||||
- source: salt://common/files/log-rotate.conf
|
||||
- template: jinja
|
||||
- mode: 644
|
||||
|
||||
/usr/local/bin/common-rotate:
|
||||
cron.present:
|
||||
- user: root
|
||||
- minute: '1'
|
||||
- hour: '0'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
# Create the status directory
|
||||
sostatusdir:
|
||||
file.directory:
|
||||
@@ -200,17 +166,11 @@ sostatus_log:
|
||||
- name: /opt/so/log/sostatus/status.log
|
||||
- mode: 644
|
||||
|
||||
common_pip_dependencies:
|
||||
pip.installed:
|
||||
- user: root
|
||||
- pkgs:
|
||||
- rich
|
||||
- target: /usr/lib64/python3.6/site-packages
|
||||
|
||||
# Install sostatus check cron
|
||||
sostatus_check_cron:
|
||||
# Install sostatus check cron. This is used to populate Grid.
|
||||
so-status_check_cron:
|
||||
cron.present:
|
||||
- name: '/usr/sbin/so-status -j > /opt/so/log/sostatus/status.log 2>&1'
|
||||
- identifier: so-status_check_cron
|
||||
- user: root
|
||||
- minute: '*/1'
|
||||
- hour: '*'
|
||||
@@ -220,7 +180,7 @@ sostatus_check_cron:
|
||||
|
||||
remove_post_setup_cron:
|
||||
cron.absent:
|
||||
- name: 'salt-call state.highstate'
|
||||
- name: 'PATH=$PATH:/usr/sbin salt-call state.highstate'
|
||||
- identifier: post_setup_cron
|
||||
|
||||
{% if GLOBALS.role not in ['eval', 'manager', 'managersearch', 'standalone'] %}
|
||||
@@ -234,7 +194,7 @@ soversionfile:
|
||||
|
||||
{% endif %}
|
||||
|
||||
{% if GLOBALS.so_model %}
|
||||
{% if GLOBALS.so_model and GLOBALS.so_model not in ['SO2AMI01', 'SO2AZI01', 'SO2GCI01'] %}
|
||||
{% if GLOBALS.os == 'Rocky' %}
|
||||
# Install Raid tools
|
||||
raidpkgs:
|
||||
@@ -246,9 +206,10 @@ raidpkgs:
|
||||
{% endif %}
|
||||
|
||||
# Install raid check cron
|
||||
so_raid_status:
|
||||
so-raid-status:
|
||||
cron.present:
|
||||
- name: '/usr/sbin/so-raid-status > /dev/null 2>&1'
|
||||
- identifier: so-raid-status
|
||||
- user: root
|
||||
- minute: '*/15'
|
||||
- hour: '*'
|
||||
|
||||
@@ -5,28 +5,37 @@ commonpkgs:
|
||||
pkg.installed:
|
||||
- skip_suggestions: True
|
||||
- pkgs:
|
||||
- chrony
|
||||
- apache2-utils
|
||||
- wget
|
||||
- ntpdate
|
||||
- jq
|
||||
- python3-docker
|
||||
- curl
|
||||
- ca-certificates
|
||||
- software-properties-common
|
||||
- apt-transport-https
|
||||
- openssl
|
||||
- netcat
|
||||
- python3-mysqldb
|
||||
- sqlite3
|
||||
- libssl-dev
|
||||
- python3-dateutil
|
||||
- python3-m2crypto
|
||||
- python3-mysqldb
|
||||
- python3-packaging
|
||||
- python3-watchdog
|
||||
- python3-lxml
|
||||
- git
|
||||
- vim
|
||||
|
||||
# since Ubuntu requires and internet connection we can use pip to install modules
|
||||
python3-pip:
|
||||
pkg.installed
|
||||
|
||||
python-rich:
|
||||
pip.installed:
|
||||
- name: rich
|
||||
- target: /usr/local/lib/python3.8/dist-packages/
|
||||
- require:
|
||||
- pkg: python3-pip
|
||||
|
||||
|
||||
{% elif GLOBALS.os == 'Rocky' %}
|
||||
commonpkgs:
|
||||
pkg.installed:
|
||||
@@ -51,6 +60,8 @@ commonpkgs:
|
||||
- python3-m2crypto
|
||||
- rsync
|
||||
- python3-rich
|
||||
- python3-pyyaml
|
||||
- python3-watchdog
|
||||
- python3-packaging
|
||||
- unzip
|
||||
{% endif %}
|
||||
@@ -8,6 +8,15 @@ soup_scripts:
|
||||
- source: salt://common/tools/sbin
|
||||
- include_pat:
|
||||
- so-common
|
||||
- so-firewall
|
||||
- so-image-common
|
||||
- soup
|
||||
|
||||
soup_manager_scripts:
|
||||
file.recurse:
|
||||
- name: /usr/sbin
|
||||
- user: root
|
||||
- group: root
|
||||
- file_mode: 755
|
||||
- source: salt://manager/tools/sbin
|
||||
- include_pat:
|
||||
- so-firewall
|
||||
- soup
|
||||
@@ -5,6 +5,7 @@
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
ELASTIC_AGENT_TARBALL_VERSION="8.7.1"
|
||||
DEFAULT_SALT_DIR=/opt/so/saltstack/default
|
||||
DOC_BASE_URL="https://docs.securityonion.net/en/2.4"
|
||||
|
||||
@@ -54,33 +55,37 @@ add_interface_bond0() {
|
||||
ethtool -K "$BNIC" $i off &>/dev/null
|
||||
fi
|
||||
done
|
||||
# Check if the bond slave connection has already been created
|
||||
nmcli -f name,uuid -p con | grep -q "bond0-slave-$BNIC"
|
||||
local found_int=$?
|
||||
|
||||
if [[ $found_int != 0 ]]; then
|
||||
# Create the slave interface and assign it to the bond
|
||||
nmcli con add type ethernet ifname "$BNIC" con-name "bond0-slave-$BNIC" master bond0 -- \
|
||||
ethernet.mtu "$MTU" \
|
||||
connection.autoconnect "yes"
|
||||
else
|
||||
local int_uuid
|
||||
int_uuid=$(nmcli -f name,uuid -p con | sed -n "s/bond0-slave-$BNIC //p" | tr -d ' ')
|
||||
if ! [[ $is_cloud ]]; then
|
||||
# Check if the bond slave connection has already been created
|
||||
nmcli -f name,uuid -p con | grep -q "bond0-slave-$BNIC"
|
||||
local found_int=$?
|
||||
|
||||
nmcli con mod "$int_uuid" \
|
||||
ethernet.mtu "$MTU" \
|
||||
connection.autoconnect "yes"
|
||||
fi
|
||||
if [[ $found_int != 0 ]]; then
|
||||
# Create the slave interface and assign it to the bond
|
||||
nmcli con add type ethernet ifname "$BNIC" con-name "bond0-slave-$BNIC" master bond0 -- \
|
||||
ethernet.mtu "$MTU" \
|
||||
connection.autoconnect "yes"
|
||||
else
|
||||
local int_uuid
|
||||
int_uuid=$(nmcli -f name,uuid -p con | sed -n "s/bond0-slave-$BNIC //p" | tr -d ' ')
|
||||
|
||||
nmcli con mod "$int_uuid" \
|
||||
ethernet.mtu "$MTU" \
|
||||
connection.autoconnect "yes"
|
||||
fi
|
||||
fi
|
||||
|
||||
ip link set dev "$BNIC" arp off multicast off allmulticast off promisc on
|
||||
|
||||
# Bring the slave interface up
|
||||
if [[ $verbose == true ]]; then
|
||||
nmcli con up "bond0-slave-$BNIC"
|
||||
else
|
||||
nmcli con up "bond0-slave-$BNIC" &>/dev/null
|
||||
|
||||
if ! [[ $is_cloud ]]; then
|
||||
# Bring the slave interface up
|
||||
if [[ $verbose == true ]]; then
|
||||
nmcli con up "bond0-slave-$BNIC"
|
||||
else
|
||||
nmcli con up "bond0-slave-$BNIC" &>/dev/null
|
||||
fi
|
||||
fi
|
||||
|
||||
if [ "$nic_error" != 0 ]; then
|
||||
return "$nic_error"
|
||||
fi
|
||||
@@ -201,7 +206,7 @@ gpg_rpm_import() {
|
||||
local RPMKEYSLOC="$UPDATE_DIR/salt/repo/client/files/rocky/keys"
|
||||
fi
|
||||
|
||||
RPMKEYS=('RPM-GPG-KEY-EPEL-9' 'SALTSTACK-GPG-KEY2.pub' 'docker.pub' 'securityonion.pub')
|
||||
RPMKEYS=('RPM-GPG-KEY-rockyofficial' 'RPM-GPG-KEY-EPEL-9' 'SALT-PROJECT-GPG-PUBKEY-2023.pub' 'docker.pub' 'securityonion.pub')
|
||||
|
||||
for RPMKEY in "${RPMKEYS[@]}"; do
|
||||
rpm --import $RPMKEYSLOC/$RPMKEY
|
||||
@@ -238,7 +243,7 @@ is_manager_node() {
|
||||
is_sensor_node() {
|
||||
# Check to see if this is a sensor (forward) node
|
||||
is_single_node_grid && return 0
|
||||
grep "role: so-" /etc/salt/grains | grep -E "sensor|heavynode|helix" &> /dev/null
|
||||
grep "role: so-" /etc/salt/grains | grep -E "sensor|heavynode" &> /dev/null
|
||||
}
|
||||
|
||||
is_single_node_grid() {
|
||||
@@ -296,6 +301,17 @@ lookup_role() {
|
||||
echo ${pieces[1]}
|
||||
}
|
||||
|
||||
is_feature_enabled() {
|
||||
feature=$1
|
||||
enabled=$(lookup_salt_value features)
|
||||
for cur in $enabled; do
|
||||
if [[ "$feature" == "$cur" ]]; then
|
||||
return 0
|
||||
fi
|
||||
done
|
||||
return 1
|
||||
}
|
||||
|
||||
require_manager() {
|
||||
if is_manager_node; then
|
||||
echo "This is a manager, so we can proceed."
|
||||
|
||||
@@ -1,34 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0; you may not use
|
||||
# this file except in compliance with the Elastic License 2.0.
|
||||
|
||||
#so-elastic-agent-gen-installers $FleetHost $EnrollmentToken
|
||||
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
ENROLLMENTOKEN=$(curl -K /opt/so/conf/elasticsearch/curl.config -L "localhost:5601/api/fleet/enrollment_api_keys" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' | jq .list | jq -r -c '.[] | select(.policy_id | contains("endpoints")) | .api_key')
|
||||
|
||||
FLEETHOST=$(lookup_pillar "server:url" "elasticfleet")
|
||||
|
||||
#FLEETHOST=$1
|
||||
#ENROLLMENTOKEN=$2
|
||||
CONTAINERGOOS=( "linux" "darwin" "windows" )
|
||||
|
||||
rm -rf /tmp/elastic-agent-workspace
|
||||
mkdir -p /tmp/elastic-agent-workspace
|
||||
|
||||
for OS in "${CONTAINERGOOS[@]}"
|
||||
do
|
||||
printf "\n\nGenerating $OS Installer..."
|
||||
cp /opt/so/saltstack/default/salt/elasticfleet/files/elastic-agent/so-elastic-agent-*-$OS-x86_64.tar.gz /tmp/elastic-agent-workspace/$OS.tar.gz
|
||||
docker run -e CGO_ENABLED=0 -e GOOS=$OS \
|
||||
--mount type=bind,source=/etc/ssl/certs/,target=/workspace/files/cert/ \
|
||||
--mount type=bind,source=/tmp/elastic-agent-workspace/,target=/workspace/files/elastic-agent/ \
|
||||
--mount type=bind,source=/opt/so/saltstack/local/salt/elasticfleet/files/so_agent-installers/,target=/output/ \
|
||||
{{ GLOBALS.registry_host }}:5000/{{ GLOBALS.image_repo }}/so-elastic-agent-builder:{{ GLOBALS.so_version }} go build -ldflags "-X main.fleetHost=$FLEETHOST -X main.enrollmentToken=$ENROLLMENTOKEN" -o /output/so-elastic-agent_$OS
|
||||
printf "\n $OS Installer Generated..."
|
||||
done
|
||||
@@ -1,94 +0,0 @@
|
||||
#!/bin/bash
|
||||
#
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{%- set NODEIP = salt['pillar.get']('host:mainip', '') %}
|
||||
. /usr/sbin/so-common
|
||||
|
||||
SKIP=0
|
||||
#########################################
|
||||
# Options
|
||||
#########################################
|
||||
usage()
|
||||
{
|
||||
cat <<EOF
|
||||
Security Onion Elastic Clear
|
||||
Options:
|
||||
-h This message
|
||||
-y Skip interactive mode
|
||||
EOF
|
||||
}
|
||||
while getopts "h:y" OPTION
|
||||
do
|
||||
case $OPTION in
|
||||
h)
|
||||
usage
|
||||
exit 0
|
||||
;;
|
||||
|
||||
y)
|
||||
SKIP=1
|
||||
;;
|
||||
*)
|
||||
usage
|
||||
exit 0
|
||||
;;
|
||||
esac
|
||||
done
|
||||
if [ $SKIP -ne 1 ]; then
|
||||
# List indices
|
||||
echo
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -k -L https://{{ NODEIP }}:9200/_cat/indices?v
|
||||
echo
|
||||
# Inform user we are about to delete all data
|
||||
echo
|
||||
echo "This script will delete all data (documents, indices, etc.) in the Elasticsearch database."
|
||||
echo
|
||||
echo "If you would like to proceed, please type "AGREE" and hit ENTER."
|
||||
echo
|
||||
# Read user input
|
||||
read INPUT
|
||||
if [ "$INPUT" != "AGREE" ] ; then exit 0; fi
|
||||
fi
|
||||
|
||||
# Check to see if Logstash are running
|
||||
LS_ENABLED=$(so-status | grep logstash)
|
||||
EA_ENABLED=$(so-status | grep elastalert)
|
||||
|
||||
if [ ! -z "$LS_ENABLED" ]; then
|
||||
|
||||
/usr/sbin/so-logstash-stop
|
||||
|
||||
fi
|
||||
|
||||
if [ ! -z "$EA_ENABLED" ]; then
|
||||
|
||||
/usr/sbin/so-elastalert-stop
|
||||
|
||||
fi
|
||||
|
||||
# Delete data
|
||||
echo "Deleting data..."
|
||||
|
||||
INDXS=$(curl -K /opt/so/conf/elasticsearch/curl.config -s -XGET -k -L https://{{ NODEIP }}:9200/_cat/indices?v | egrep 'logstash|elastalert|so-' | awk '{ print $3 }')
|
||||
for INDX in ${INDXS}
|
||||
do
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config-XDELETE -k -L https://"{{ NODEIP }}:9200/${INDX}" > /dev/null 2>&1
|
||||
done
|
||||
|
||||
#Start Logstash
|
||||
if [ ! -z "$LS_ENABLED" ]; then
|
||||
|
||||
/usr/sbin/so-logstash-start
|
||||
|
||||
fi
|
||||
|
||||
if [ ! -z "$EA_ENABLED" ]; then
|
||||
|
||||
/usr/sbin/so-elastalert-start
|
||||
|
||||
fi
|
||||
|
||||
@@ -1,137 +0,0 @@
|
||||
#!/bin/bash
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
{%- set ZEEKVER = salt['pillar.get']('global:mdengine', '') %}
|
||||
{%- set STRELKAENABLED = salt['pillar.get']('strelka:enabled', '0') %}
|
||||
{%- set RITAENABLED = salt['pillar.get']('rita:enabled', False) %}
|
||||
|
||||
wait_for_web_response "http://localhost:5601/api/spaces/space/default" "default" 300 "curl -K /opt/so/conf/elasticsearch/curl.config"
|
||||
|
||||
# Let's snag a cookie from Kibana
|
||||
SESSIONCOOKIE=$(curl -K /opt/so/conf/elasticsearch/curl.config -c - -X GET http://localhost:5601/ | grep sid | awk '{print $7}')
|
||||
|
||||
# Disable certain Features from showing up in the Kibana UI
|
||||
echo
|
||||
echo "Disable certain Features from showing up in the Kibana UI"
|
||||
so-kibana-space-defaults
|
||||
echo
|
||||
|
||||
# Suricata logs
|
||||
echo
|
||||
echo "Setting up Suricata package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "id": "suricata-logs", "name": "suricata-logs", "description": "Suricata integration", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": [ "/nsm/suricata/eve*.json" ], "data_stream.dataset": "suricata", "tags": [],"processors": "- add_fields:\n target: event\n fields:\n category: network\n module: suricata", "custom": "pipeline: suricata.common" }}}}}}'
|
||||
echo
|
||||
|
||||
# Zeek logs
|
||||
echo
|
||||
echo "Setting up Zeek package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "name": "zeek-logs", "description": "Zeek logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": ["/nsm/zeek/logs/current/*.log"], "data_stream.dataset": "zeek", "tags": [], "processors": "- dissect:\n tokenizer: \"/nsm/zeek/logs/current/%{pipeline}.log\"\n field: \"log.file.path\"\n trim_chars: \".log\"\n target_prefix: \"\"\n- script:\n lang: javascript\n source: >\n function process(event) {\n var pl = event.Get(\"pipeline\");\n event.Put(\"@metadata.pipeline\", \"zeek.\" + pl);\n }\n- add_fields:\n target: event\n fields:\n category: network\n module: zeek\n- add_tags:\n tags: \"ics\"\n when:\n regexp:\n pipeline: \"^bacnet*|^bsap*|^cip*|^cotp*|^dnp3*|^ecat*|^enip*|^modbus*|^opcua*|^profinet*|^s7comm*\"", "custom": "exclude_files: [\"broker|capture_loss|ecat_arp_info|loaded_scripts|packet_filter|stats|stderr|stdout.log$\"]\n" } } } } } }'
|
||||
echo
|
||||
|
||||
|
||||
# Import - EVTX
|
||||
echo
|
||||
echo "Setting up EVTX import package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d '{ "package": { "name": "log", "version": "1.1.0" }, "name": "import-evtx-logs", "namespace": "so", "description": "Import Windows EVTX logs", "policy_id": "so-grid-nodes", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": [ "/nsm/import/*/evtx/data.json" ], "data_stream.dataset": "import", "custom": "pipeline: import.wel", "processors": "- dissect:\n tokenizer: \"/nsm/import/%{import.id}/evtx/%{import.file}\"\n field: \"log.file.path\"\n target_prefix: \"\"\n- decode_json_fields:\n fields: [\"message\"]\n target: \"\"\n- add_fields:\n target: event\n fields:\n module: windows_eventlog\n imported: true", "tags": [] } } } } } }'
|
||||
echo
|
||||
|
||||
# Import - Suricata logs
|
||||
echo
|
||||
echo "Setting up Suricata import package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d '{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "id": "import-suricata-logs", "name": "import-suricata-logs", "description": "Import Suricata logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": ["/nsm/import/*/suricata/eve*.json"], "data_stream.dataset": "import", "tags": [], "processors": "- add_fields:\n target: event\n fields:\n category: network\n module: suricata\n imported: true\n- dissect:\n tokenizer: \"/nsm/import/%{import.id}/suricata/%{import.file}\"\n field: \"log.file.path\"\n target_prefix: \"\"", "custom": "pipeline: suricata.common" } } } } } }'
|
||||
echo
|
||||
|
||||
# Import - Zeek logs
|
||||
echo
|
||||
echo "Setting up Zeek import package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "name": "import-zeek-logs", "description": "Zeek Import logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": ["/nsm/import/*/zeek/logs/*.log"], "data_stream.dataset": "import", "tags": [], "processors": "- dissect:\n tokenizer: \"/nsm/import/%{import.id}/zeek/logs/%{import.file}\"\n field: \"log.file.path\"\n target_prefix: \"\"\n- script:\n lang: javascript\n source: >\n function process(event) {\n var pl = event.Get(\"import.file\").slice(0,-4);\n event.Put(\"@metadata.pipeline\", \"zeek.\" + pl);\n }\n- add_fields:\n target: event\n fields:\n category: network\n module: zeek\n imported: true\n- add_tags:\n tags: \"ics\"\n when:\n regexp:\n import.file: \"^bacnet*|^bsap*|^cip*|^cotp*|^dnp3*|^ecat*|^enip*|^modbus*|^opcua*|^profinet*|^s7comm*\"", "custom": "exclude_files: [\"broker|capture_loss|ecat_arp_info|loaded_scripts|packet_filter|stats|stderr|stdout.log$\"]\n" } } } } } }'
|
||||
echo
|
||||
|
||||
# Strelka logs
|
||||
echo
|
||||
echo "Setting up Strelka package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "id": "strelka-logs", "name": "strelka-logs", "description": "Strelka logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": [ "/nsm/strelka/log/strelka.log" ], "data_stream.dataset": "strelka", "tags": [],"processors": "- add_fields:\n target: event\n fields:\n category: file\n module: strelka", "custom": "pipeline: strelka.file" }}}}}}'
|
||||
echo
|
||||
|
||||
# Syslog TCP Port 514
|
||||
echo
|
||||
echo "Setting up Syslog TCP package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d '{ "policy_id": "so-grid-nodes", "package": { "name": "tcp", "version": "1.5.0" }, "id": "syslog-tcp-514", "name": "syslog-tcp-514", "description": "Syslog Over TCP Port 514", "namespace": "so", "inputs": { "tcp-tcp": { "enabled": true, "streams": { "tcp.generic": { "enabled": true, "vars": { "listen_address": "0.0.0.0", "listen_port": "514", "data_stream.dataset": "syslog", "pipeline": "syslog", "processors": "- add_fields:\n target: event\n fields:\n module: syslog", "tags": [ "syslog" ], "syslog_options": "field: message\n#format: auto\n#timezone: Local" } } } } } }'
|
||||
echo
|
||||
|
||||
# Syslog UDP Port 514
|
||||
echo
|
||||
echo "Setting up Syslog UDP package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d '{ "policy_id": "so-grid-nodes", "package": { "name": "udp", "version": "1.5.0" }, "id": "syslog-udp-514", "name": "syslog-udp-514", "description": "Syslog over UDP Port 514", "namespace": "so", "inputs": { "udp-udp": { "enabled": true, "streams": { "udp.generic": { "enabled": true, "vars": { "listen_address": "0.0.0.0", "listen_port": "514", "data_stream.dataset": "syslog", "pipeline": "syslog", "max_message_size": "10KiB", "keep_null": false, "processors": "- add_fields:\n target: event\n fields: \n module: syslog\n", "tags": [ "syslog" ], "syslog_options": "field: message\n#format: auto\n#timezone: Local" } } } } } }'
|
||||
echo
|
||||
|
||||
# Kratos logs
|
||||
echo
|
||||
echo "Setting up Kratos package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "id": "kratos-logs", "name": "kratos-logs", "description": "Kratos logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": [ "/opt/so/log/kratos/kratos.log" ], "data_stream.dataset": "kratos", "tags": [],"custom":"pipeline: kratos","processors": "- decode_json_fields:\n fields: [\"message\"]\n target: \"\"\n add_error_key: true \n- add_fields:\n target: event\n fields:\n category: iam\n module: kratos" }}}}}}'
|
||||
echo
|
||||
|
||||
# RITA Logs
|
||||
#echo
|
||||
#echo "Setting up RITA package policy..."
|
||||
#curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "log", "version": "1.1.0" }, "id": "rita-logs", "name": "rita-logs", "description": "RITA Beacon logs", "namespace": "so", "inputs": { "logs-logfile": { "enabled": true, "streams": { "log.log": { "enabled": true, "vars": { "paths": [ "/nsm/rita/beacons.csv", "/nsm/rita/long-connections.csv", "/nsm/rita/short-connections.csv", "/nsm/rita/exploded-dns.csv" ], "data_stream.dataset": "rita", "tags": [], "processors": "- add_fields:\n target: event\n fields:\n category: network\n module: rita\n- if:\n log.file.path: beacons.csv\n then: \n - add_fields:\n target: \"@metadata\"\n fields:\n pipeline: rita.beacon\n- if:\n regexp:\n log.file.path: \"*connections.csv\"\n then: \n - add_fields:\n target: \"@metadata\"\n fields:\n pipeline: rita.connection\n- if:\n log.file.path: \"exploded-dns.csv\"\n then: \n - add_fields:\n target: \"@metadata\"\n fields:\n pipeline: rita.dns" }}}}}}'
|
||||
#echo
|
||||
|
||||
# Elasticsearch logs
|
||||
echo
|
||||
echo "Setting up Elasticsearch package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "elasticsearch", "version": "1.0.0" }, "id": "elasticsearch-logs", "name": "elasticsearch-logs", "description": "Elasticsearch Logs", "namespace": "default", "inputs": { "elasticsearch-logfile": { "enabled": true, "streams": { "elasticsearch.audit": { "enabled": false, "vars": { "paths": [ "/var/log/elasticsearch/*_audit.json" ] } }, "elasticsearch.deprecation": { "enabled": false, "vars": { "paths": [ "/var/log/elasticsearch/*_deprecation.json" ] } }, "elasticsearch.gc": { "enabled": false, "vars": { "paths": [ "/var/log/elasticsearch/gc.log.[0-9]*", "/var/log/elasticsearch/gc.log" ] } }, "elasticsearch.server": { "enabled": true, "vars": { "paths": [ "/opt/so/log/elasticsearch/*.log" ] } }, "elasticsearch.slowlog": { "enabled": false, "vars": { "paths": [ "/var/log/elasticsearch/*_index_search_slowlog.json", "/var/log/elasticsearch/*_index_indexing_slowlog.json" ] } } } }, "elasticsearch-elasticsearch/metrics": { "enabled": false, "vars": { "hosts": [ "http://localhost:9200" ], "scope": "node" }, "streams": { "elasticsearch.stack_monitoring.ccr": { "enabled": false }, "elasticsearch.stack_monitoring.cluster_stats": { "enabled": false }, "elasticsearch.stack_monitoring.enrich": { "enabled": false }, "elasticsearch.stack_monitoring.index": { "enabled": false }, "elasticsearch.stack_monitoring.index_recovery": { "enabled": false, "vars": { "active.only": true } }, "elasticsearch.stack_monitoring.index_summary": { "enabled": false }, "elasticsearch.stack_monitoring.ml_job": { "enabled": false }, "elasticsearch.stack_monitoring.node": { "enabled": false }, "elasticsearch.stack_monitoring.node_stats": { "enabled": false }, "elasticsearch.stack_monitoring.pending_tasks": { "enabled": false }, "elasticsearch.stack_monitoring.shard": { "enabled": false } } } } }'
|
||||
echo
|
||||
|
||||
# Logstash logs
|
||||
#echo
|
||||
#echo "Setting up Logstash package policy..."
|
||||
#curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "logstash", "version": "2.0.0" }, "id": "logstash-logs", "name": "logstash-logs", "description": "Logstash logs", "namespace": "default", "inputs": { "logstash-logfile": { "enabled": true, "streams": { "logstash.log": { "enabled": true, "vars": { "paths": [ "/opt/so/logs/logstash/logstash.log" ] } }, "logstash.slowlog": { "enabled": false, "vars": { "paths": [ "/var/log/logstash/logstash-slowlog-plain*.log", "/var/log/logstash/logstash-slowlog-json*.log" ] } } } }, "logstash-logstash/metrics": { "enabled": false, "vars": { "hosts": [ "http://localhost:9600" ], "period": "10s" }, "streams": { "logstash.stack_monitoring.node": { "enabled": false }, "logstash.stack_monitoring.node_stats": { "enabled": false } } } } }'
|
||||
#echo
|
||||
|
||||
# Kibana logs
|
||||
#echo
|
||||
#echo "Setting up Kibana package policy..."
|
||||
#curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "kibana", "version": "2.0.0" }, "id": "kibana-logs", "name": "kibana-logs", "description": "Kibana logs", "namespace": "default", "inputs": { "kibana-logfile": { "enabled": true, "streams": { "kibana.audit": { "enabled": false, "vars": { "paths": [ "/opt/so/log/kibana/kibana.log" ] } }, "kibana.log": { "enabled": true, "vars": { "paths": [ "/opt/so/log/kibana/kibana.log" ] } } } }, "kibana-kibana/metrics": { "enabled": false, "vars": { "hosts": [ "http://localhost:5601" ] }, "streams": { "kibana.stack_monitoring.cluster_actions": { "enabled": false }, "kibana.stack_monitoring.cluster_rules": { "enabled": false }, "kibana.stack_monitoring.node_actions": { "enabled": false }, "kibana.stack_monitoring.node_rules": { "enabled": false }, "kibana.stack_monitoring.stats": { "enabled": false }, "kibana.stack_monitoring.status": { "enabled": false } } } } }'
|
||||
#echo
|
||||
|
||||
# Redis logs
|
||||
echo
|
||||
echo "Setting up Redis package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{ "policy_id": "so-grid-nodes", "package": { "name": "redis", "version": "1.4.0" }, "id": "redis-logs", "name": "redis-logs", "description": "Redis logs", "namespace": "default", "inputs": { "redis-logfile": { "enabled": true, "streams": { "redis.log": { "enabled": true, "vars": { "paths": [ "/opt/so/log/redis/redis.log" ], "tags": [ "redis-log" ], "preserve_original_event": false } } } }, "redis-redis": { "enabled": false, "streams": { "redis.slowlog": { "enabled": false, "vars": { "hosts": [ "127.0.0.1:6379" ], "password": "" } } } }, "redis-redis/metrics": { "enabled": false, "vars": { "hosts": [ "127.0.0.1:6379" ], "idle_timeout": "20s", "maxconn": 10, "network": "tcp", "password": "" }, "streams": { "redis.info": { "enabled": false, "vars": { "period": "10s" } }, "redis.key": { "enabled": false, "vars": { "key.patterns": "- limit: 20\n pattern: '*'\n", "period": "10s" } }, "redis.keyspace": { "enabled": false, "vars": { "period": "10s" } } } } } }'
|
||||
echo
|
||||
|
||||
# IDH logs
|
||||
echo
|
||||
echo "Setting up IDH package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{"policy_id":"so-grid-nodes","package":{"name":"log","version":"1.1.1"},"id":"idh-logs","name":"idh-logs","namespace":"so","description":"IDH integration","inputs":{"logs-logfile":{"enabled":true,"streams":{"log.log":{"enabled":true,"vars":{"paths":["/nsm/idh/opencanary.log"],"data_stream.dataset":"idh","custom":"pipeline: common","processors": "\n- decode_json_fields:\n fields: [\"message\"]\n target: \"\"\n add_error_key: true\n- drop_fields:\n when:\n equals:\n logtype: \"1001\"\n fields: [\"src_host\", \"src_port\", \"dst_host\", \"dst_port\" ]\n ignore_missing: true\n- rename:\n fields:\n - from: \"src_host\"\n to: \"source.ip\"\n - from: \"src_port\"\n to: \"source.port\"\n - from: \"dst_host\"\n to: \"destination.host\"\n - from: \"dst_port\"\n to: \"destination.port\"\n ignore_missing: true\n- convert:\n fields:\n - {from: \"logtype\", to: \"event.code\", type: \"string\"}\n ignore_missing: true\n- drop_fields:\n fields: '\''[\"prospector\", \"input\", \"offset\", \"beat\"]'\''\n- add_fields:\n target: event\n fields:\n category: host\n module: opencanary","tags":[]}}}}}}'
|
||||
echo
|
||||
|
||||
# SOC - Server logs
|
||||
echo
|
||||
echo "Setting up SOC - Server Logs package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{"package":{"name":"log","version":"1.1.2"},"name":"soc-server-logs","namespace":"so","description":"Security Onion Console Logs","policy_id":"so-grid-nodes","inputs":{"logs-logfile":{"enabled":true,"streams":{"log.log":{"enabled":true,"vars":{"paths":["/opt/so/log/soc/sensoroni-server.log"],"data_stream.dataset":"soc","custom":"pipeline: common","processors": "- decode_json_fields:\n fields: [\"message\"]\n target: \"soc\"\n process_array: true\n max_depth: 2\n add_error_key: true \n- add_fields:\n target: event\n fields:\n category: host\n module: soc\n dataset_temp: server\n- rename:\n fields:\n - from: \"soc.fields.sourceIp\"\n to: \"source.ip\"\n - from: \"soc.fields.status\"\n to: \"http.response.status_code\"\n - from: \"soc.fields.method\"\n to: \"http.request.method\"\n - from: \"soc.fields.path\"\n to: \"url.path\"\n - from: \"soc.message\"\n to: \"event.action\"\n - from: \"soc.level\"\n to: \"log.level\"\n ignore_missing: true","tags":[]}}}}}}'
|
||||
echo
|
||||
|
||||
# SOC - Sensoroni logs
|
||||
echo
|
||||
echo "Setting up SOC - Sensoroni Logs package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{"package":{"name":"log","version":"1.1.2"},"name":"soc-sensoroni-logs","namespace":"so","description":"Security Onion - Sensoroni - Logs","policy_id":"so-grid-nodes","inputs":{"logs-logfile":{"enabled":true,"streams":{"log.log":{"enabled":true,"vars":{"paths":["/opt/so/log/sensoroni/sensoroni.log"],"data_stream.dataset":"soc","custom":"pipeline: common","processors": "- decode_json_fields:\n fields: [\"message\"]\n target: \"sensoroni\"\n process_array: true\n max_depth: 2\n add_error_key: true \n- add_fields:\n target: event\n fields:\n category: host\n module: soc\n dataset_temp: sensoroni\n- rename:\n fields:\n - from: \"sensoroni.fields.sourceIp\"\n to: \"source.ip\"\n - from: \"sensoroni.fields.status\"\n to: \"http.response.status_code\"\n - from: \"sensoroni.fields.method\"\n to: \"http.request.method\"\n - from: \"sensoroni.fields.path\"\n to: \"url.path\"\n - from: \"sensoroni.message\"\n to: \"event.action\"\n - from: \"sensoroni.level\"\n to: \"log.level\"\n ignore_missing: true","tags":[]}}}}}}'
|
||||
echo
|
||||
|
||||
# SOC - Elastic Auth Sync logs
|
||||
echo
|
||||
echo "Setting up SOC - Elastic Auth Sync Logs package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{"package":{"name":"log","version":"1.1.2"},"name":"soc-auth-sync-logs","namespace":"so","description":"Security Onion - Elastic Auth Sync - Logs","policy_id":"so-grid-nodes","inputs":{"logs-logfile":{"enabled":true,"streams":{"log.log":{"enabled":true,"vars":{"paths":["/opt/so/log/soc/sync.log"],"data_stream.dataset":"soc","custom":"pipeline: common","processors": "- dissect:\n tokenizer: \"%{event.action}\"\n field: \"message\"\n target_prefix: \"\"\n- add_fields:\n target: event\n fields:\n category: host\n module: soc\n dataset_temp: auth_sync","tags":[]}}}}}}'
|
||||
echo
|
||||
|
||||
# SOC - Salt Relay logs
|
||||
echo
|
||||
echo "Setting up SOC - Salt_Relay Logs package policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -L -X POST "localhost:5601/api/fleet/package_policies" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d'{"package":{"name":"log","version":"1.1.2"},"name":"soc-salt-relay-logs","namespace":"so","description":"Security Onion - Salt Relay - Logs","policy_id":"so-grid-nodes","inputs":{"logs-logfile":{"enabled":true,"streams":{"log.log":{"enabled":true,"vars":{"paths":["/opt/so/log/soc/salt-relay.log"],"data_stream.dataset":"soc","custom":"pipeline: common","processors": "- dissect:\n tokenizer: \"%{soc.ts} | %{event.action}\"\n field: \"message\"\n target_prefix: \"\"\n- add_fields:\n target: event\n fields:\n category: host\n module: soc\n dataset_temp: salt_relay","tags":[]}}}}}}'
|
||||
echo
|
||||
@@ -1,109 +0,0 @@
|
||||
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0; you may not use
|
||||
# this file except in compliance with the Elastic License 2.0.
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
|
||||
# Create ES Token
|
||||
ESTOKEN=$(curl -K /opt/so/conf/elasticsearch/curl.config -L -X POST "localhost:5601/api/fleet/service_tokens" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' | jq -r .value)
|
||||
printf "ESTOKEN = $ESTOKEN \n"
|
||||
|
||||
# Add SO-Manager Fleet URL
|
||||
## This array replaces whatever URLs are currently configured
|
||||
printf "\n"
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -L -X PUT "localhost:5601/api/fleet/settings" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d '{"fleet_server_hosts":["https://{{ GLOBALS.manager_ip }}:8220"]}'
|
||||
printf "\n\n"
|
||||
|
||||
# Configure certificates
|
||||
mkdir -p /opt/so/conf/elastic-fleet/certs
|
||||
cp /etc/ssl/certs/intca.crt /opt/so/conf/elastic-fleet/certs
|
||||
cp /etc/pki/elasticfleet* /opt/so/conf/elastic-fleet/certs
|
||||
|
||||
{% if grains.role in ['so-import', 'so-standalone', 'so-eval', 'so-manager', 'so-managersearch'] %}
|
||||
# Add SO-Manager Elasticsearch Ouput
|
||||
ESCACRT=$(openssl x509 -in /opt/so/conf/elastic-fleet/certs/intca.crt)
|
||||
JSON_STRING=$( jq -n \
|
||||
--arg ESCACRT "$ESCACRT" \
|
||||
'{"name":"so-manager_elasticsearch","id":"so-manager_elasticsearch","type":"elasticsearch","hosts":["https://{{ GLOBALS.manager_ip }}:9200"],"is_default":true,"is_default_monitoring":true,"config_yaml":"","ssl":{"certificate_authorities": [$ESCACRT]}}' )
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -L -X POST "localhost:5601/api/fleet/outputs" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d "$JSON_STRING"
|
||||
printf "\n\n"
|
||||
|
||||
{% else %}
|
||||
# Create Logstash Output payload
|
||||
LOGSTASHCRT=$(openssl x509 -in /opt/so/conf/elastic-fleet/certs/elasticfleet.crt)
|
||||
LOGSTASHKEY=$(openssl rsa -in /opt/so/conf/elastic-fleet/certs/elasticfleet.key)
|
||||
LOGSTASHCA=$(openssl x509 -in /opt/so/conf/elastic-fleet/certs/intca.crt)
|
||||
JSON_STRING=$( jq -n \
|
||||
--arg LOGSTASHCRT "$LOGSTASHCRT" \
|
||||
--arg LOGSTASHKEY "$LOGSTASHKEY" \
|
||||
--arg LOGSTASHCA "$LOGSTASHCA" \
|
||||
'{"name":"so-manager_logstash","id":"so-manager_logstash","type":"logstash","hosts":["{{ GLOBALS.manager_ip }}:5055"],"is_default":true,"is_default_monitoring":true,"config_yaml":"","ssl":{"certificate": $LOGSTASHCRT,"key": $LOGSTASHKEY,"certificate_authorities":[ $LOGSTASHCA ]}}'
|
||||
)
|
||||
|
||||
# Add SO-Manager Logstash Ouput
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -L -X POST "localhost:5601/api/fleet/outputs" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' -d "$JSON_STRING"
|
||||
printf "\n\n"
|
||||
{%- endif %}
|
||||
|
||||
# Add Elastic Fleet Integrations
|
||||
|
||||
# Add Elastic Fleet Server Agent Policy
|
||||
#curl -vv -K /opt/so/conf/elasticsearch/curl.config -L \
|
||||
#-X POST "localhost:5601/api/fleet/agent_policies" \
|
||||
#-H 'kbn-xsrf: true' -H 'Content-Type: application/json' \
|
||||
#-d '{"name":"SO-Manager","id":"so-manager","description":"SO Manager Fleet Server Policy","namespace":"default","monitoring_enabled":["logs"],"has_fleet_server":true}'
|
||||
|
||||
# Add Agent Policy - SOS Grid Nodes
|
||||
#curl -vv -K /opt/so/conf/elasticsearch/curl.config -L \
|
||||
#-X POST "localhost:5601/api/fleet/agent_policies" \
|
||||
#-H 'kbn-xsrf: true' -H 'Content-Type: application/json' \
|
||||
#-d '{"name":"SO-Grid","id":"so-grid","description":"SO Grid Endpoint Policy","namespace":"default","monitoring_enabled":["logs"]}'
|
||||
|
||||
# Add Agent Policy - Default endpoints
|
||||
#curl -vv -K /opt/so/conf/elasticsearch/curl.config -L \
|
||||
#-X POST "localhost:5601/api/fleet/agent_policies" \
|
||||
#-H 'kbn-xsrf: true' -H 'Content-Type: application/json' \
|
||||
#-d '{"name":"Endpoints-Initalization","id":"endpoints","description":"Initial Endpoint Policy","namespace":"default","monitoring_enabled":["logs"]}'
|
||||
|
||||
ENDPOINTSENROLLMENTOKEN=$(curl -K /opt/so/conf/elasticsearch/curl.config -L "localhost:5601/api/fleet/enrollment_api_keys" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' | jq .list | jq -r -c '.[] | select(.policy_id | contains("endpoints-default")) | .api_key')
|
||||
GRIDNODESENROLLMENTOKEN=$(curl -K /opt/so/conf/elasticsearch/curl.config -L "localhost:5601/api/fleet/enrollment_api_keys" -H 'kbn-xsrf: true' -H 'Content-Type: application/json' | jq .list | jq -r -c '.[] | select(.policy_id | contains("so-grid-nodes")) | .api_key')
|
||||
|
||||
# Store needed data in minion pillar
|
||||
pillar_file=/opt/so/saltstack/local/pillar/minions/{{ GLOBALS.minion_id }}.sls
|
||||
printf '%s\n'\
|
||||
"elasticfleet:"\
|
||||
" server:"\
|
||||
" es_token: '$ESTOKEN'"\
|
||||
" endpoints_enrollment: '$ENDPOINTSENROLLMENTOKEN'"\
|
||||
" grid_enrollment: '$GRIDNODESENROLLMENTOKEN'"\
|
||||
" url: '{{ GLOBALS.manager_ip }}'"\
|
||||
"" >> "$pillar_file"
|
||||
|
||||
#Store Grid Nodes Enrollment token in Global pillar
|
||||
global_pillar_file=/opt/so/saltstack/local/pillar/soc_global.sls
|
||||
printf '%s\n'\
|
||||
" fleet_grid_enrollment_token: '$GRIDNODESENROLLMENTOKEN'"\
|
||||
"" >> "$global_pillar_file"
|
||||
|
||||
# Call Elastic-Fleet Salt State
|
||||
salt-call state.apply elasticfleet queue=True
|
||||
|
||||
# Load Elastic Fleet integrations
|
||||
/usr/sbin/so-elastic-fleet-integration-policy-load
|
||||
|
||||
# Temp
|
||||
wget --progress=bar:force:noscroll -P /opt/so/saltstack/default/salt/elasticfleet/files/elastic-agent/ https://github.com/Security-Onion-Solutions/securityonion-docker-rpm/releases/download/so_elastic-agent-8.6.2/so-elastic-agent-8.6.2-darwin-x86_64.tar.gz
|
||||
wget --progress=bar:force:noscroll -P /opt/so/saltstack/default/salt/elasticfleet/files/elastic-agent/ https://github.com/Security-Onion-Solutions/securityonion-docker-rpm/releases/download/so_elastic-agent-8.6.2/so-elastic-agent-8.6.2-linux-x86_64.tar.gz
|
||||
wget --progress=bar:force:noscroll -P /opt/so/saltstack/default/salt/elasticfleet/files/elastic-agent/ https://github.com/Security-Onion-Solutions/securityonion-docker-rpm/releases/download/so_elastic-agent-8.6.2/so-elastic-agent-8.6.2-windows-x86_64.tar.gz
|
||||
|
||||
#git clone -b 2.4-so-elastic-agent https://github.com/Security-Onion-Solutions/securityonion-image.git
|
||||
#cd securityonion-image/so-elastic-agent-builder
|
||||
#docker build -t so-elastic-agent-builder .
|
||||
|
||||
so-elastic-agent-gen-installers
|
||||
salt-call state.apply elasticfleet.install_agent_grid queue=True
|
||||
@@ -1,31 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode', 'so-import']%}
|
||||
/usr/sbin/so-restart elasticsearch $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval', 'so-manager', 'so-managersearch', 'so-standalone', 'so-import']%}
|
||||
/usr/sbin/so-restart kibana $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-restart logstash $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-restart curator $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone']%}
|
||||
/usr/sbin/so-restart elastalert $1
|
||||
{%- endif %}
|
||||
@@ -1,31 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode', 'so-import']%}
|
||||
/usr/sbin/so-start elasticsearch $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval', 'so-manager', 'so-managersearch', 'so-standalone', 'so-import']%}
|
||||
/usr/sbin/so-start kibana $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-start logstash $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-start curator $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone']%}
|
||||
/usr/sbin/so-start elastalert $1
|
||||
{%- endif %}
|
||||
@@ -1,31 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode', 'so-import']%}
|
||||
/usr/sbin/so-stop elasticsearch $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval', 'so-manager', 'so-managersearch', 'so-standalone', 'so-import']%}
|
||||
/usr/sbin/so-stop kibana $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-stop logstash $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-manager', 'so-managersearch', 'so-standalone', 'so-heavynode', 'so-searchnode']%}
|
||||
/usr/sbin/so-stop curator $1
|
||||
{%- endif %}
|
||||
|
||||
{%- if grains['role'] in ['so-eval','so-manager', 'so-managersearch', 'so-standalone']%}
|
||||
/usr/sbin/so-stop elastalert $1
|
||||
{%- endif %}
|
||||
@@ -1,21 +0,0 @@
|
||||
#!/bin/bash
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
{% import_yaml 'elasticsearch/defaults.yaml' as ESCONFIG with context %}
|
||||
{%- set ES_INDEX_SETTINGS = salt['pillar.get']('elasticsearch:index_settings', default=ESCONFIG.elasticsearch.index_settings, merge=True) %}
|
||||
{%- set NODEIP = salt['pillar.get']('host:mainip', '') %}
|
||||
|
||||
{%- for index, settings in ES_INDEX_SETTINGS.items() %}
|
||||
{%- if settings.policy is defined %}
|
||||
echo
|
||||
echo "Setting up {{ index }}-logs policy..."
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -b "sid=$SESSIONCOOKIE" -s -k -L -X PUT "https://{{ NODEIP }}:9200/_ilm/policy/{{ index }}-logs" -H 'Content-Type: application/json' -d'{ "policy": {{ settings.policy | tojson(true) }} }'
|
||||
echo
|
||||
{%- endif %}
|
||||
{%- endfor %}
|
||||
echo
|
||||
@@ -1,15 +0,0 @@
|
||||
#!/bin/bash
|
||||
#
|
||||
#
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
IP={{ salt['grains.get']('ip_interfaces').get(salt['pillar.get']('sensor:mainint', salt['pillar.get']('manager:mainint', salt['pillar.get']('elasticsearch:mainint', salt['pillar.get']('host:mainint')))))[0] }}
|
||||
ESPORT=9200
|
||||
|
||||
echo "Removing read only attributes for indices..."
|
||||
echo
|
||||
curl -K /opt/so/conf/elasticsearch/curl.config -s -k -XPUT -H "Content-Type: application/json" -L https://$IP:9200/_all/_settings -d '{"index.blocks.read_only_allow_delete": null}' 2>&1 | if grep -q ack; then echo "Index settings updated..."; else echo "There was any issue updating the read-only attribute. Please ensure Elasticsearch is running.";fi;
|
||||
@@ -1,104 +0,0 @@
|
||||
#!/usr/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
if [[ $# -lt 1 ]]; then
|
||||
echo "Usage: $0 --role=<ROLE> --ip=<IP ADDRESS> --apply=<true|false>"
|
||||
echo ""
|
||||
echo " Example: so-firewall --role=sensor --ip=192.168.254.100 --apply=true"
|
||||
echo ""
|
||||
exit 1
|
||||
fi
|
||||
|
||||
for i in "$@"; do
|
||||
case $i in
|
||||
-r=*|--role=*)
|
||||
ROLE="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-i=*|--ip=*)
|
||||
IP="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-a=*|--apply*)
|
||||
APPLY="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-*|--*)
|
||||
echo "Unknown option $i"
|
||||
exit 1
|
||||
;;
|
||||
*)
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
ROLE=${ROLE,,}
|
||||
APPLY=${APPLY,,}
|
||||
|
||||
function rolecall() {
|
||||
THEROLE=$1
|
||||
THEROLES="analyst analyst_workstations beats_endpoint beats_endpoint_ssl elastic_agent_endpoint elasticsearch_rest endgame eval heavynodes idh manager managersearch receivers searchnodes sensors standalone strelka_frontend syslog"
|
||||
|
||||
for AROLE in $THEROLES; do
|
||||
if [ "$AROLE" = "$THEROLE" ]; then
|
||||
return 0
|
||||
fi
|
||||
done
|
||||
return 1
|
||||
}
|
||||
|
||||
# Make sure the required options are specified
|
||||
if [ -z "$ROLE" ]; then
|
||||
echo "Please specify a role with --role="
|
||||
exit 1
|
||||
fi
|
||||
if [ -z "$IP" ]; then
|
||||
echo "Please specify an IP address with --ip="
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Are we dealing with a role that this script supports?
|
||||
if rolecall "$ROLE"; then
|
||||
echo "$ROLE is a supported role"
|
||||
else
|
||||
echo "This is not a supported role"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# Are we dealing with an IP?
|
||||
if verify_ip4 "$IP"; then
|
||||
echo "$IP is a valid IP or CIDR"
|
||||
else
|
||||
echo "$IP is not a valid IP or CIDR"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
local_salt_dir=/opt/so/saltstack/local/salt/firewall
|
||||
|
||||
# Let's see if the file exists and if it does, let's see if the IP exists.
|
||||
if [ -f "$local_salt_dir/hostgroups/$ROLE" ]; then
|
||||
if grep -q $IP "$local_salt_dir/hostgroups/$ROLE"; then
|
||||
echo "Host already exists"
|
||||
exit 0
|
||||
fi
|
||||
fi
|
||||
|
||||
# If you have reached this part of your quest then let's add the IP
|
||||
echo "Adding $IP to the $ROLE role"
|
||||
echo "$IP" >> $local_salt_dir/hostgroups/$ROLE
|
||||
|
||||
# Check to see if we are applying this right away.
|
||||
if [ "$APPLY" = "true" ]; then
|
||||
echo "Applying the firewall rules"
|
||||
salt-call state.apply firewall queue=True
|
||||
echo "Firewall rules have been applied... Review logs further if there were errors."
|
||||
echo ""
|
||||
else
|
||||
echo "Firewall rules will be applied next salt run"
|
||||
fi
|
||||
@@ -1,27 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
local_salt_dir=/opt/so/saltstack/local
|
||||
|
||||
got_root() {
|
||||
|
||||
# Make sure you are root
|
||||
if [ "$(id -u)" -ne 0 ]; then
|
||||
echo "This script must be run using sudo!"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
}
|
||||
|
||||
got_root
|
||||
if [ ! -f $local_salt_dir/pillar/fireeye/init.sls ]; then
|
||||
echo "This is nto configured for Helix Mode. Please re-install."
|
||||
exit
|
||||
else
|
||||
echo "Enter your Helix API Key: "
|
||||
read APIKEY
|
||||
sed -i "s/^ api_key.*/ api_key: $APIKEY/g" $local_salt_dir/pillar/fireeye/init.sls
|
||||
docker stop so-logstash
|
||||
docker rm so-logstash
|
||||
echo "Restarting Logstash for updated key"
|
||||
salt-call state.apply logstash queue=True
|
||||
fi
|
||||
@@ -38,6 +38,7 @@ container_list() {
|
||||
"so-zeek"
|
||||
"so-elastic-agent"
|
||||
"so-elastic-agent-builder"
|
||||
"so-elastic-fleet-package-registry"
|
||||
)
|
||||
elif [ $MANAGERCHECK != 'so-helix' ]; then
|
||||
TRUSTED_CONTAINERS=(
|
||||
@@ -45,6 +46,7 @@ container_list() {
|
||||
"so-elastalert"
|
||||
"so-elastic-agent"
|
||||
"so-elastic-agent-builder"
|
||||
"so-elastic-fleet-package-registry"
|
||||
"so-elasticsearch"
|
||||
"so-idh"
|
||||
"so-idstools"
|
||||
|
||||
@@ -1,155 +0,0 @@
|
||||
#!/bin/bash
|
||||
#
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{%- set MANAGER = salt['grains.get']('master') %}
|
||||
{%- set VERSION = salt['pillar.get']('global:soversion') %}
|
||||
{%- set IMAGEREPO = salt['pillar.get']('global:imagerepo') %}
|
||||
{%- set MANAGERIP = salt['pillar.get']('global:managerip') %}
|
||||
{%- set URLBASE = salt['pillar.get']('global:url_base') %}
|
||||
{%- set ES_USER = salt['pillar.get']('elasticsearch:auth:users:so_elastic_user:user', '') %}
|
||||
{%- set ES_PASS = salt['pillar.get']('elasticsearch:auth:users:so_elastic_user:pass', '') %}
|
||||
|
||||
INDEX_DATE=$(date +'%Y.%m.%d')
|
||||
RUNID=$(cat /dev/urandom | tr -dc 'a-z0-9' | fold -w 8 | head -n 1)
|
||||
LOG_FILE=/nsm/import/evtx-import.log
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
function usage {
|
||||
cat << EOF
|
||||
Usage: $0 <evtx-file-1> [evtx-file-2] [evtx-file-*]
|
||||
|
||||
Imports one or more evtx files into Security Onion. The evtx files will be analyzed and made available for review in the Security Onion toolset.
|
||||
EOF
|
||||
}
|
||||
|
||||
|
||||
function evtx2es() {
|
||||
EVTX=$1
|
||||
HASH=$2
|
||||
|
||||
docker run --rm \
|
||||
-v "$EVTX:/tmp/data.evtx" \
|
||||
-v "/nsm/import/$HASH/evtx/:/tmp/evtx/" \
|
||||
-v "/nsm/import/evtx-end_newest:/tmp/newest" \
|
||||
-v "/nsm/import/evtx-start_oldest:/tmp/oldest" \
|
||||
--entrypoint "/evtx_calc_timestamps.sh" \
|
||||
{{ MANAGER }}:5000/{{ IMAGEREPO }}/so-pcaptools:{{ VERSION }} >> $LOG_FILE 2>&1
|
||||
}
|
||||
|
||||
# if no parameters supplied, display usage
|
||||
if [ $# -eq 0 ]; then
|
||||
usage
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# ensure this is a Manager node
|
||||
require_manager
|
||||
|
||||
# verify that all parameters are files
|
||||
for i in "$@"; do
|
||||
if ! [ -f "$i" ]; then
|
||||
usage
|
||||
echo "\"$i\" is not a valid file!"
|
||||
exit 2
|
||||
fi
|
||||
done
|
||||
|
||||
# track if we have any valid or invalid evtx
|
||||
INVALID_EVTXS="no"
|
||||
VALID_EVTXS="no"
|
||||
|
||||
# track oldest start and newest end so that we can generate the Kibana search hyperlink at the end
|
||||
START_OLDEST="2050-12-31"
|
||||
END_NEWEST="1971-01-01"
|
||||
|
||||
touch /nsm/import/evtx-start_oldest
|
||||
touch /nsm/import/evtx-end_newest
|
||||
|
||||
echo $START_OLDEST > /nsm/import/evtx-start_oldest
|
||||
echo $END_NEWEST > /nsm/import/evtx-end_newest
|
||||
|
||||
# paths must be quoted in case they include spaces
|
||||
for EVTX in "$@"; do
|
||||
EVTX=$(/usr/bin/realpath "$EVTX")
|
||||
echo "Processing Import: ${EVTX}"
|
||||
|
||||
# generate a unique hash to assist with dedupe checks
|
||||
HASH=$(md5sum "${EVTX}" | awk '{ print $1 }')
|
||||
HASH_DIR=/nsm/import/${HASH}
|
||||
echo "- assigning unique identifier to import: $HASH"
|
||||
|
||||
if [ -d $HASH_DIR ]; then
|
||||
echo "- this EVTX has already been imported; skipping"
|
||||
INVALID_EVTXS="yes"
|
||||
else
|
||||
VALID_EVTXS="yes"
|
||||
|
||||
EVTX_DIR=$HASH_DIR/evtx
|
||||
mkdir -p $EVTX_DIR
|
||||
|
||||
# import evtx and write them to import ingest pipeline
|
||||
echo "- importing logs to Elasticsearch..."
|
||||
evtx2es "${EVTX}" $HASH
|
||||
|
||||
# compare $START to $START_OLDEST
|
||||
START=$(cat /nsm/import/evtx-start_oldest)
|
||||
START_COMPARE=$(date -d $START +%s)
|
||||
START_OLDEST_COMPARE=$(date -d $START_OLDEST +%s)
|
||||
if [ $START_COMPARE -lt $START_OLDEST_COMPARE ]; then
|
||||
START_OLDEST=$START
|
||||
fi
|
||||
|
||||
# compare $ENDNEXT to $END_NEWEST
|
||||
END=$(cat /nsm/import/evtx-end_newest)
|
||||
ENDNEXT=`date +%Y-%m-%d --date="$END 1 day"`
|
||||
ENDNEXT_COMPARE=$(date -d $ENDNEXT +%s)
|
||||
END_NEWEST_COMPARE=$(date -d $END_NEWEST +%s)
|
||||
if [ $ENDNEXT_COMPARE -gt $END_NEWEST_COMPARE ]; then
|
||||
END_NEWEST=$ENDNEXT
|
||||
fi
|
||||
|
||||
cp -f "${EVTX}" "${EVTX_DIR}"/data.evtx
|
||||
chmod 644 "${EVTX_DIR}"/data.evtx
|
||||
|
||||
fi # end of valid evtx
|
||||
|
||||
echo
|
||||
|
||||
done # end of for-loop processing evtx files
|
||||
|
||||
# remove temp files
|
||||
echo "Cleaning up:"
|
||||
for TEMP_EVTX in ${TEMP_EVTXS[@]}; do
|
||||
echo "- removing temporary evtx $TEMP_EVTX"
|
||||
rm -f $TEMP_EVTX
|
||||
done
|
||||
|
||||
# output final messages
|
||||
if [ "$INVALID_EVTXS" = "yes" ]; then
|
||||
echo
|
||||
echo "Please note! One or more evtx was invalid! You can scroll up to see which ones were invalid."
|
||||
fi
|
||||
|
||||
START_OLDEST_FORMATTED=`date +%Y-%m-%d --date="$START_OLDEST"`
|
||||
START_OLDEST_SLASH=$(echo $START_OLDEST_FORMATTED | sed -e 's/-/%2F/g')
|
||||
END_NEWEST_SLASH=$(echo $END_NEWEST | sed -e 's/-/%2F/g')
|
||||
|
||||
if [ "$VALID_EVTXS" = "yes" ]; then
|
||||
cat << EOF
|
||||
|
||||
Import complete!
|
||||
|
||||
You can use the following hyperlink to view data in the time range of your import. You can triple-click to quickly highlight the entire hyperlink and you can then copy it into your browser:
|
||||
https://{{ URLBASE }}/#/dashboards?q=import.id:${RUNID}%20%7C%20groupby%20-sankey%20event.dataset%20event.category%2a%20%7C%20groupby%20-pie%20event.category%20%7C%20groupby%20-bar%20event.module%20%7C%20groupby%20event.dataset%20%7C%20groupby%20event.module%20%7C%20groupby%20event.category%20%7C%20groupby%20observer.name%20%7C%20groupby%20source.ip%20%7C%20groupby%20destination.ip%20%7C%20groupby%20destination.port&t=${START_OLDEST_SLASH}%2000%3A00%3A00%20AM%20-%20${END_NEWEST_SLASH}%2000%3A00%3A00%20AM&z=UTC
|
||||
|
||||
or you can manually set your Time Range to be (in UTC):
|
||||
From: $START_OLDEST_FORMATTED To: $END_NEWEST
|
||||
|
||||
Please note that it may take 30 seconds or more for events to appear in Security Onion Console.
|
||||
EOF
|
||||
fi
|
||||
@@ -1,17 +0,0 @@
|
||||
#!/bin/bash
|
||||
#
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% set MAININT = salt['pillar.get']('host:mainint') -%}
|
||||
{% set NODEIP = salt['grains.get']('ip_interfaces').get(MAININT)[0] -%}
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
if [ "$1" == "" ]; then
|
||||
for i in $(curl -s -L http://{{ NODEIP }}:9600/_node/stats | jq .pipelines | jq '. | to_entries | .[].key' | sed 's/\"//g'); do echo ${i^}:; curl -s localhost:9600/_node/stats | jq .pipelines.$i.events; done
|
||||
else
|
||||
curl -s -L http://{{ NODEIP }}:9600/_node/stats | jq .pipelines.$1.events
|
||||
fi
|
||||
@@ -1,304 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
if [ -f /usr/sbin/so-common ]; then
|
||||
. /usr/sbin/so-common
|
||||
fi
|
||||
|
||||
if [ "$(id -u)" -ne 0 ]; then
|
||||
echo "This script must be run using sudo!"
|
||||
exit 1
|
||||
fi
|
||||
|
||||
if [[ $# -lt 1 ]]; then
|
||||
echo "Usage: $0 -o=<operation> -m=[id]"
|
||||
echo ""
|
||||
echo " where <operation> is one of the following:"
|
||||
echo ""
|
||||
echo " list: Lists all keys with hashes"
|
||||
echo " accept: Accepts a new key and adds the minion files"
|
||||
echo " delete: Removes the key and deletes the minion files"
|
||||
echo " reject: Rejects a key"
|
||||
echo " test: Perform minion test"
|
||||
echo ""
|
||||
exit 1
|
||||
fi
|
||||
|
||||
for i in "$@"; do
|
||||
case $i in
|
||||
-o=*|--operation=*)
|
||||
OPERATION="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-m=*|--minionid=*)
|
||||
MINION_ID="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-e=*|--esheap=*)
|
||||
ES_HEAP_SIZE="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-n=*|--mgmtnic=*)
|
||||
MNIC="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-d=*|--description=*)
|
||||
NODE_DESCRIPTION="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-a=*|--monitor=*)
|
||||
INTERFACE="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-i=*|--ip=*)
|
||||
MAINIP="${i#*=}"
|
||||
shift
|
||||
;;
|
||||
-*|--*)
|
||||
echo "Unknown option $i"
|
||||
exit 1
|
||||
;;
|
||||
*)
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
PILLARFILE=/opt/so/saltstack/local/pillar/minions/$MINION_ID.sls
|
||||
ADVPILLARFILE=/opt/so/saltstack/local/pillar/minions/adv_$MINION_ID.sls
|
||||
|
||||
function getinstallinfo() {
|
||||
# Pull from file
|
||||
INSTALLVARS=$(sudo salt "$MINION_ID" cp.get_file_str /opt/so/install.txt --out=newline_values_only)
|
||||
source <(echo $INSTALLVARS)
|
||||
}
|
||||
|
||||
function testminion() {
|
||||
# Always run on the host, since this is going to be the manager of a distributed grid, or an eval/standalone.
|
||||
# Distributed managers must run this in order for the sensor nodes to have access to the so-tcpreplay image.
|
||||
so-test
|
||||
result=$?
|
||||
|
||||
# If this so-minion script is not running on the given minion ID, run so-test remotely on the sensor as well
|
||||
local_id=$(lookup_grain id)
|
||||
if [[ ! "$local_id" =~ "${MINION_ID}_" ]]; then
|
||||
salt "$MINION_ID" cmd.run 'so-test'
|
||||
result=$?
|
||||
fi
|
||||
|
||||
exit $result
|
||||
}
|
||||
|
||||
function listminions() {
|
||||
salt-key list -F --out=json
|
||||
exit $?
|
||||
}
|
||||
|
||||
function rejectminion() {
|
||||
salt-key -y -r $MINION_ID
|
||||
exit $?
|
||||
}
|
||||
|
||||
function acceptminion() {
|
||||
salt-key -y -a $MINION_ID
|
||||
}
|
||||
|
||||
function deleteminion() {
|
||||
salt-key -y -d $MINION_ID
|
||||
}
|
||||
|
||||
function deleteminionfiles () {
|
||||
rm -f $PILLARFILE
|
||||
rm -f $ADVPILLARFILE
|
||||
}
|
||||
|
||||
# Create the minion file
|
||||
function create_minion_files() {
|
||||
mkdir -p /opt/so/saltstack/local/pillar/minions
|
||||
touch $ADVPILLARFILE
|
||||
if [ -f "$PILLARFILE" ]; then
|
||||
rm $PILLARFILE
|
||||
fi
|
||||
}
|
||||
|
||||
# Add Elastic settings to the minion file
|
||||
function add_elastic_to_minion() {
|
||||
printf '%s\n'\
|
||||
"elasticsearch:"\
|
||||
" esheap: '$ES_HEAP_SIZE'"\
|
||||
" " >> $PILLARFILE
|
||||
}
|
||||
|
||||
# Add IDH Services info to the minion file
|
||||
function add_idh_to_minion() {
|
||||
printf '%s\n'\
|
||||
"idh:"\
|
||||
" restrict_management_ip: $IDH_MGTRESTRICT"\
|
||||
" services:" >> "$PILLARFILE"
|
||||
IFS=',' read -ra IDH_SERVICES_ARRAY <<< "$IDH_SERVICES"
|
||||
for service in ${IDH_SERVICES_ARRAY[@]}; do
|
||||
echo " - $service" | tr '[:upper:]' '[:lower:]' | tr -d '"' >> "$PILLARFILE"
|
||||
done
|
||||
}
|
||||
|
||||
function add_logstash_to_minion() {
|
||||
# Create the logstash advanced pillar
|
||||
printf '%s\n'\
|
||||
"logstash_settings:"\
|
||||
" ls_host: '$LSHOSTNAME'"\
|
||||
" ls_pipeline_batch_size: 125"\
|
||||
" ls_input_threads: 1"\
|
||||
" lsheap: $LSHEAP"\
|
||||
" ls_pipeline_workers: $CPUCORES"\
|
||||
" " >> $PILLARFILE
|
||||
}
|
||||
|
||||
# Analyst Workstation
|
||||
function add_analyst_to_minion() {
|
||||
printf '%s\n'\
|
||||
"host:"\
|
||||
" mainint: '$MNIC'"\
|
||||
"workstation:"\
|
||||
" gui:"\
|
||||
" enabled: true"\
|
||||
"sensoroni:"\
|
||||
" node_description: '${NODE_DESCRIPTION//\'/''}'" >> $PILLARFILE
|
||||
}
|
||||
|
||||
# Add basic host info to the minion file
|
||||
function add_host_to_minion() {
|
||||
printf '%s\n'\
|
||||
"host:"\
|
||||
" mainip: '$MAINIP'"\
|
||||
" mainint: '$MNIC'" >> $PILLARFILE
|
||||
}
|
||||
|
||||
# Add sensoroni specific information - Can we pull node_adrees from the host pillar?
|
||||
function add_sensoroni_to_minion() {
|
||||
|
||||
printf '%s\n'\
|
||||
"sensoroni:"\
|
||||
" node_description: '${NODE_DESCRIPTION//\'/''}'"\
|
||||
" " >> $PILLARFILE
|
||||
}
|
||||
|
||||
# Sensor settings for the minion pillar
|
||||
function add_sensor_to_minion() {
|
||||
echo "sensor:" >> $PILLARFILE
|
||||
echo " interface: '$INTERFACE'" >> $PILLARFILE
|
||||
echo " mtu: 9000" >> $PILLARFILE
|
||||
echo "zeek:" >> $PILLARFILE
|
||||
echo " config:" >> $PILLARFILE
|
||||
echo " node:" >> $PILLARFILE
|
||||
echo " lb_procs: '$CORECOUNT'" >> $PILLARFILE
|
||||
echo "suricata:" >> $PILLARFILE
|
||||
echo " config:" >> $PILLARFILE
|
||||
echo " af-packet:" >> $PILLARFILE
|
||||
echo " threads: '$CORECOUNT'" >> $PILLARFILE
|
||||
echo "pcap:" >> $PILLARFILE
|
||||
echo " enabled: True" >> $PILLARFILE
|
||||
}
|
||||
|
||||
function updateMine() {
|
||||
salt "$MINION_ID" mine.send network.ip_addrs interface="$MNIC"
|
||||
}
|
||||
function apply_ES_state() {
|
||||
salt-call state.apply elasticsearch concurrent=True
|
||||
}
|
||||
function createEVAL() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
add_sensor_to_minion
|
||||
}
|
||||
|
||||
function createIDH() {
|
||||
add_idh_to_minion
|
||||
}
|
||||
|
||||
function createIMPORT() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
add_sensor_to_minion
|
||||
}
|
||||
|
||||
function createHEAVYNODE() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
add_sensor_to_minion
|
||||
}
|
||||
|
||||
function createMANAGER() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
}
|
||||
|
||||
function createMANAGERSEARCH() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
}
|
||||
|
||||
function createSENSOR() {
|
||||
add_sensor_to_minion
|
||||
}
|
||||
|
||||
function createSEARCHNODE() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
updateMine
|
||||
apply_ES_state
|
||||
}
|
||||
|
||||
function createSTANDALONE() {
|
||||
add_elastic_to_minion
|
||||
add_logstash_to_minion
|
||||
add_sensor_to_minion
|
||||
}
|
||||
|
||||
function testConnection() {
|
||||
retry 15 3 "salt '$MINION_ID' test.ping" True
|
||||
local ret=$?
|
||||
if [[ $ret != 0 ]]; then
|
||||
echo "The Minion has been accepted but is not online. Try again later"
|
||||
echo "Deleting the key"
|
||||
deleteminion
|
||||
exit 1
|
||||
fi
|
||||
}
|
||||
|
||||
if [[ "$OPERATION" = 'list' ]]; then
|
||||
listminions
|
||||
fi
|
||||
|
||||
if [[ "$OPERATION" = 'delete' ]]; then
|
||||
deleteminionfiles
|
||||
deleteminion
|
||||
fi
|
||||
|
||||
if [[ "$OPERATION" = 'add' || "$OPERATION" = 'setup' ]]; then
|
||||
# Skip this if its setup
|
||||
if [ $OPERATION != 'setup' ]; then
|
||||
# Accept the salt key
|
||||
acceptminion
|
||||
# Test to see if the minion was accepted
|
||||
testConnection
|
||||
# Pull the info from the file to build what is needed
|
||||
getinstallinfo
|
||||
fi
|
||||
# Check to see if nodetype is set
|
||||
if [ -z $NODETYPE ]; then
|
||||
echo "No node type specified"
|
||||
exit 1
|
||||
fi
|
||||
create_minion_files
|
||||
add_host_to_minion
|
||||
add_sensoroni_to_minion
|
||||
create$NODETYPE
|
||||
echo "Minion file created for $MINION_ID"
|
||||
fi
|
||||
|
||||
if [[ "$OPERATION" = 'test' ]]; then
|
||||
testminion
|
||||
fi
|
||||
@@ -24,6 +24,7 @@ if [ $# -ge 1 ]; then
|
||||
|
||||
case $1 in
|
||||
"steno") docker stop so-steno && docker rm so-steno && salt-call state.apply pcap queue=True;;
|
||||
"elastic-fleet") docker stop so-elastic-fleet && docker rm so-elastic-fleet && salt-call state.apply elasticfleet queue=True;;
|
||||
*) docker stop so-$1 ; docker rm so-$1 ; salt-call state.apply $1 queue=True;;
|
||||
esac
|
||||
else
|
||||
|
||||
@@ -1,10 +0,0 @@
|
||||
#!/bin/bash
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
argstr=""
|
||||
for arg in "$@"; do
|
||||
argstr="${argstr} \"${arg}\""
|
||||
done
|
||||
|
||||
docker exec so-idstools /bin/bash -c "cd /opt/so/idstools/etc && idstools-rulecat --force ${argstr}"
|
||||
@@ -24,6 +24,7 @@ if [ $# -ge 1 ]; then
|
||||
case $1 in
|
||||
"all") salt-call state.highstate queue=True;;
|
||||
"steno") if docker ps | grep -q so-$1; then printf "\n$1 is already running!\n\n"; else docker rm so-$1 >/dev/null 2>&1 ; salt-call state.apply pcap queue=True; fi ;;
|
||||
"elastic-fleet") if docker ps | grep -q so-$1; then printf "\n$1 is already running!\n\n"; else docker rm so-$1 >/dev/null 2>&1 ; salt-call state.apply elasticfleet queue=True; fi ;;
|
||||
*) if docker ps | grep -E -q '^so-$1$'; then printf "\n$1 is already running\n\n"; else docker rm so-$1 >/dev/null 2>&1 ; salt-call state.apply $1 queue=True; fi ;;
|
||||
esac
|
||||
else
|
||||
|
||||
@@ -170,7 +170,8 @@ def main():
|
||||
if "-h" in options or "--help" in options or "-?" in options:
|
||||
showUsage(options, None)
|
||||
|
||||
if os.environ["USER"] != "root":
|
||||
proc = subprocess.run(['id', '-u'], stdout=subprocess.PIPE, encoding="utf-8")
|
||||
if proc.stdout.strip() != "0":
|
||||
fail("This program must be run as root")
|
||||
|
||||
console = Console()
|
||||
|
||||
+18
-18
@@ -6,17 +6,17 @@
|
||||
# Elastic License 2.0.
|
||||
|
||||
|
||||
{# we only want the script to install the workstation if it is Rocky -#}
|
||||
{# we only want the script to install the desktop if it is Rocky -#}
|
||||
{% if grains.os == 'Rocky' -%}
|
||||
{# if this is a manager -#}
|
||||
{% if grains.master == grains.id.split('_')|first -%}
|
||||
|
||||
source /usr/sbin/so-common
|
||||
doc_workstation_url="$DOC_BASE_URL/analyst-vm.html"
|
||||
doc_desktop_url="$DOC_BASE_URL/desktop.html"
|
||||
pillar_file="/opt/so/saltstack/local/pillar/minions/{{grains.id}}.sls"
|
||||
|
||||
if [ -f "$pillar_file" ]; then
|
||||
if ! grep -q "^workstation:$" "$pillar_file"; then
|
||||
if ! grep -q "^desktop:$" "$pillar_file"; then
|
||||
|
||||
FIRSTPASS=yes
|
||||
while [[ $INSTALL != "yes" ]] && [[ $INSTALL != "no" ]]; do
|
||||
@@ -26,7 +26,7 @@ if [ -f "$pillar_file" ]; then
|
||||
echo "## _______________________________ ##"
|
||||
echo "## ##"
|
||||
echo "## Installing the Security Onion ##"
|
||||
echo "## analyst node on this device will ##"
|
||||
echo "## Desktop on this device will ##"
|
||||
echo "## make permanent changes to ##"
|
||||
echo "## the system. ##"
|
||||
echo "## A system reboot will be required ##"
|
||||
@@ -42,40 +42,40 @@ if [ -f "$pillar_file" ]; then
|
||||
done
|
||||
|
||||
if [[ $INSTALL == "no" ]]; then
|
||||
echo "Exiting analyst node installation."
|
||||
echo "Exiting desktop node installation."
|
||||
exit 0
|
||||
fi
|
||||
|
||||
# Add workstation pillar to the minion's pillar file
|
||||
# Add desktop pillar to the minion's pillar file
|
||||
printf '%s\n'\
|
||||
"workstation:"\
|
||||
"desktop:"\
|
||||
" gui:"\
|
||||
" enabled: true"\
|
||||
"" >> "$pillar_file"
|
||||
echo "Applying the workstation state. This could take some time since there are many packages that need to be installed."
|
||||
if salt-call state.apply workstation -linfo queue=True; then # make sure the state ran successfully
|
||||
echo "Applying the desktop state. This could take some time since there are many packages that need to be installed."
|
||||
if salt-call state.apply desktop -linfo queue=True; then # make sure the state ran successfully
|
||||
echo ""
|
||||
echo "Analyst workstation has been installed!"
|
||||
echo "Security Onion Desktop has been installed!"
|
||||
echo "Press ENTER to reboot or Ctrl-C to cancel."
|
||||
read pause
|
||||
|
||||
reboot;
|
||||
else
|
||||
echo "There was an issue applying the workstation state. Please review the log above or at /opt/so/logs/salt/minion."
|
||||
echo "There was an issue applying the desktop state. Please review the log above or at /opt/so/log/salt/minion."
|
||||
fi
|
||||
else # workstation is already added
|
||||
echo "The workstation pillar already exists in $pillar_file."
|
||||
echo "To enable/disable the gui, set 'workstation:gui:enabled' to true or false in $pillar_file."
|
||||
echo "Additional documentation can be found at $doc_workstation_url."
|
||||
else # desktop is already added
|
||||
echo "The desktop pillar already exists in $pillar_file."
|
||||
echo "To enable/disable the gui, set 'desktop:gui:enabled' to true or false in $pillar_file."
|
||||
echo "Additional documentation can be found at $doc_desktop_url."
|
||||
fi
|
||||
else # if the pillar file doesn't exist
|
||||
echo "Could not find $pillar_file and add the workstation pillar."
|
||||
echo "Could not find $pillar_file and add the desktop pillar."
|
||||
fi
|
||||
|
||||
{#- if this is not a manager #}
|
||||
{% else -%}
|
||||
|
||||
echo "Since this is not a manager, the pillar values to enable analyst workstation must be set manually. Please view the documentation at $doc_workstation_url."
|
||||
echo "Since this is not a manager, the pillar values to enable Security Onion Desktop must be set manually. Please view the documentation at $doc_desktop_url."
|
||||
|
||||
{#- endif if this is a manager #}
|
||||
{% endif -%}
|
||||
@@ -83,7 +83,7 @@ echo "Since this is not a manager, the pillar values to enable analyst workstati
|
||||
{#- if not Rocky #}
|
||||
{%- else %}
|
||||
|
||||
echo "The Analyst Workstation can only be installed on Rocky. Please view the documentation at $doc_workstation_url."
|
||||
echo "The Security Onion Desktop can only be installed on Rocky Linux. Please view the documentation at $doc_desktop_url."
|
||||
|
||||
{#- endif grains.os == Rocky #}
|
||||
{% endif -%}
|
||||
Executable
+225
@@ -0,0 +1,225 @@
|
||||
#!/bin/bash
|
||||
#
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{%- set MANAGER = salt['grains.get']('master') %}
|
||||
{%- set VERSION = salt['pillar.get']('global:soversion') %}
|
||||
{%- set IMAGEREPO = salt['pillar.get']('global:imagerepo') %}
|
||||
{%- set MANAGERIP = salt['pillar.get']('global:managerip') %}
|
||||
{%- set URLBASE = salt['pillar.get']('global:url_base') %}
|
||||
{%- set ES_USER = salt['pillar.get']('elasticsearch:auth:users:so_elastic_user:user', '') %}
|
||||
{%- set ES_PASS = salt['pillar.get']('elasticsearch:auth:users:so_elastic_user:pass', '') %}
|
||||
|
||||
INDEX_DATE=$(date +'%Y.%m.%d')
|
||||
LOG_FILE=/nsm/import/evtx-import.log
|
||||
|
||||
. /usr/sbin/so-common
|
||||
|
||||
function usage {
|
||||
cat << EOF
|
||||
Usage: $0 [options] <evtx-file-1> [evtx-file-2] [evtx-file-*]
|
||||
|
||||
Imports one or more evtx files into Security Onion. The evtx files will be analyzed and made available for review in the Security Onion toolset.
|
||||
|
||||
Options:
|
||||
--json Outputs summary in JSON format. Implies --quiet.
|
||||
--quiet Silences progress information to stdout.
|
||||
EOF
|
||||
}
|
||||
|
||||
quiet=0
|
||||
json=0
|
||||
INPUT_FILES=
|
||||
while [[ $# -gt 0 ]]; do
|
||||
param=$1
|
||||
shift
|
||||
case "$param" in
|
||||
--json)
|
||||
json=1
|
||||
quiet=1
|
||||
;;
|
||||
--quiet)
|
||||
quiet=1
|
||||
;;
|
||||
-*)
|
||||
echo "Encountered unexpected parameter: $param"
|
||||
usage
|
||||
exit 1
|
||||
;;
|
||||
*)
|
||||
if [[ "$INPUT_FILES" != "" ]]; then
|
||||
INPUT_FILES="$INPUT_FILES $param"
|
||||
else
|
||||
INPUT_FILES="$param"
|
||||
fi
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
function status {
|
||||
msg=$1
|
||||
[[ $quiet -eq 1 ]] && return
|
||||
echo "$msg"
|
||||
}
|
||||
|
||||
function evtx2es() {
|
||||
EVTX=$1
|
||||
HASH=$2
|
||||
|
||||
docker run --rm \
|
||||
-v "$EVTX:/tmp/data.evtx" \
|
||||
-v "/nsm/import/$HASH/evtx/:/tmp/evtx/" \
|
||||
-v "/nsm/import/evtx-end_newest:/tmp/newest" \
|
||||
-v "/nsm/import/evtx-start_oldest:/tmp/oldest" \
|
||||
--entrypoint "/evtx_calc_timestamps.sh" \
|
||||
{{ MANAGER }}:5000/{{ IMAGEREPO }}/so-pcaptools:{{ VERSION }} >> $LOG_FILE 2>&1
|
||||
}
|
||||
|
||||
# if no parameters supplied, display usage
|
||||
if [ "$INPUT_FILES" == "" ]; then
|
||||
usage
|
||||
exit 1
|
||||
fi
|
||||
|
||||
# ensure this is a Manager node
|
||||
require_manager @> /dev/null
|
||||
|
||||
# verify that all parameters are files
|
||||
for i in $INPUT_FILES; do
|
||||
if ! [ -f "$i" ]; then
|
||||
echo "\"$i\" is not a valid file!"
|
||||
exit 2
|
||||
fi
|
||||
done
|
||||
|
||||
# track oldest start and newest end so that we can generate the Kibana search hyperlink at the end
|
||||
START_OLDEST="2050-12-31"
|
||||
END_NEWEST="1971-01-01"
|
||||
|
||||
INVALID_EVTXS_COUNT=0
|
||||
VALID_EVTXS_COUNT=0
|
||||
SKIPPED_EVTXS_COUNT=0
|
||||
|
||||
touch /nsm/import/evtx-start_oldest
|
||||
touch /nsm/import/evtx-end_newest
|
||||
|
||||
echo $START_OLDEST > /nsm/import/evtx-start_oldest
|
||||
echo $END_NEWEST > /nsm/import/evtx-end_newest
|
||||
|
||||
# paths must be quoted in case they include spaces
|
||||
for EVTX in $INPUT_FILES; do
|
||||
EVTX=$(/usr/bin/realpath "$EVTX")
|
||||
status "Processing Import: ${EVTX}"
|
||||
|
||||
# generate a unique hash to assist with dedupe checks
|
||||
HASH=$(md5sum "${EVTX}" | awk '{ print $1 }')
|
||||
HASH_DIR=/nsm/import/${HASH}
|
||||
status "- assigning unique identifier to import: $HASH"
|
||||
|
||||
if [[ "$HASH_FILTERS" == "" ]]; then
|
||||
HASH_FILTERS="import.id:${HASH}"
|
||||
HASHES="${HASH}"
|
||||
else
|
||||
HASH_FILTERS="$HASH_FILTERS%20OR%20import.id:${HASH}"
|
||||
HASHES="${HASHES} ${HASH}"
|
||||
fi
|
||||
|
||||
if [ -d $HASH_DIR ]; then
|
||||
status "- this EVTX has already been imported; skipping"
|
||||
SKIPPED_EVTXS_COUNT=$((SKIPPED_EVTXS_COUNT + 1))
|
||||
else
|
||||
EVTX_DIR=$HASH_DIR/evtx
|
||||
mkdir -p $EVTX_DIR
|
||||
|
||||
# import evtx and write them to import ingest pipeline
|
||||
status "- importing logs to Elasticsearch..."
|
||||
evtx2es "${EVTX}" $HASH
|
||||
if [[ $? -ne 0 ]]; then
|
||||
INVALID_EVTXS_COUNT=$((INVALID_EVTXS_COUNT + 1))
|
||||
status "- WARNING: This evtx file may not have fully imported successfully"
|
||||
else
|
||||
VALID_EVTXS_COUNT=$((VALID_EVTXS_COUNT + 1))
|
||||
fi
|
||||
|
||||
# compare $START to $START_OLDEST
|
||||
START=$(cat /nsm/import/evtx-start_oldest)
|
||||
START_COMPARE=$(date -d $START +%s)
|
||||
START_OLDEST_COMPARE=$(date -d $START_OLDEST +%s)
|
||||
if [ $START_COMPARE -lt $START_OLDEST_COMPARE ]; then
|
||||
START_OLDEST=$START
|
||||
fi
|
||||
|
||||
# compare $ENDNEXT to $END_NEWEST
|
||||
END=$(cat /nsm/import/evtx-end_newest)
|
||||
ENDNEXT=`date +%Y-%m-%d --date="$END 1 day"`
|
||||
ENDNEXT_COMPARE=$(date -d $ENDNEXT +%s)
|
||||
END_NEWEST_COMPARE=$(date -d $END_NEWEST +%s)
|
||||
if [ $ENDNEXT_COMPARE -gt $END_NEWEST_COMPARE ]; then
|
||||
END_NEWEST=$ENDNEXT
|
||||
fi
|
||||
|
||||
cp -f "${EVTX}" "${EVTX_DIR}"/data.evtx
|
||||
chmod 644 "${EVTX_DIR}"/data.evtx
|
||||
|
||||
fi # end of valid evtx
|
||||
|
||||
status
|
||||
|
||||
done # end of for-loop processing evtx files
|
||||
|
||||
# output final messages
|
||||
if [[ $INVALID_EVTXS_COUNT -gt 0 ]]; then
|
||||
status
|
||||
status "Please note! One or more evtx was invalid! You can scroll up to see which ones were invalid."
|
||||
fi
|
||||
|
||||
START_OLDEST_FORMATTED=`date +%Y-%m-%d --date="$START_OLDEST"`
|
||||
START_OLDEST_SLASH=$(echo $START_OLDEST_FORMATTED | sed -e 's/-/%2F/g')
|
||||
END_NEWEST_SLASH=$(echo $END_NEWEST | sed -e 's/-/%2F/g')
|
||||
|
||||
if [[ $VALID_EVTXS_COUNT -gt 0 ]] || [[ $SKIPPED_EVTXS_COUNT -gt 0 ]]; then
|
||||
URL="https://{{ URLBASE }}/#/dashboards?q=$HASH_FILTERS%20%7C%20groupby%20-sankey%20event.dataset%20event.category%2a%20%7C%20groupby%20-pie%20event.category%20%7C%20groupby%20-bar%20event.module%20%7C%20groupby%20event.dataset%20%7C%20groupby%20event.module%20%7C%20groupby%20event.category%20%7C%20groupby%20observer.name%20%7C%20groupby%20source.ip%20%7C%20groupby%20destination.ip%20%7C%20groupby%20destination.port&t=${START_OLDEST_SLASH}%2000%3A00%3A00%20AM%20-%20${END_NEWEST_SLASH}%2000%3A00%3A00%20AM&z=UTC"
|
||||
|
||||
status "Import complete!"
|
||||
status
|
||||
status "Use the following hyperlink to view the imported data. Triple-click to quickly highlight the entire hyperlink and then copy it into a browser:"
|
||||
status
|
||||
status "$URL"
|
||||
status
|
||||
status "or, manually set the Time Range to be (in UTC):"
|
||||
status
|
||||
status "From: $START_OLDEST_FORMATTED To: $END_NEWEST"
|
||||
status
|
||||
status "Note: It can take 30 seconds or more for events to appear in Security Onion Console."
|
||||
RESULT=0
|
||||
else
|
||||
START_OLDEST=
|
||||
END_NEWEST=
|
||||
URL=
|
||||
RESULT=1
|
||||
fi
|
||||
|
||||
if [[ $json -eq 1 ]]; then
|
||||
jq -n \
|
||||
--arg success_count "$VALID_EVTXS_COUNT" \
|
||||
--arg fail_count "$INVALID_EVTXS_COUNT" \
|
||||
--arg skipped_count "$SKIPPED_EVTXS_COUNT" \
|
||||
--arg begin_date "$START_OLDEST" \
|
||||
--arg end_date "$END_NEWEST" \
|
||||
--arg url "$URL" \
|
||||
--arg hashes "$HASHES" \
|
||||
'''{
|
||||
success_count: $success_count,
|
||||
fail_count: $fail_count,
|
||||
skipped_count: $skipped_count,
|
||||
begin_date: $begin_date,
|
||||
end_date: $end_date,
|
||||
url: $url,
|
||||
hash: ($hashes / " ")
|
||||
}'''
|
||||
fi
|
||||
|
||||
exit $RESULT
|
||||
+125
-51
@@ -15,12 +15,51 @@
|
||||
|
||||
function usage {
|
||||
cat << EOF
|
||||
Usage: $0 <pcap-file-1> [pcap-file-2] [pcap-file-N]
|
||||
Usage: $0 [options] <pcap-file-1> [pcap-file-2] [pcap-file-N]
|
||||
|
||||
Imports one or more PCAP files onto a sensor node. The PCAP traffic will be analyzed and made available for review in the Security Onion toolset.
|
||||
|
||||
Options:
|
||||
--json Outputs summary in JSON format. Implies --quiet.
|
||||
--quiet Silences progress information to stdout.
|
||||
EOF
|
||||
}
|
||||
|
||||
quiet=0
|
||||
json=0
|
||||
INPUT_FILES=
|
||||
while [[ $# -gt 0 ]]; do
|
||||
param=$1
|
||||
shift
|
||||
case "$param" in
|
||||
--json)
|
||||
json=1
|
||||
quiet=1
|
||||
;;
|
||||
--quiet)
|
||||
quiet=1
|
||||
;;
|
||||
-*)
|
||||
echo "Encountered unexpected parameter: $param"
|
||||
usage
|
||||
exit 1
|
||||
;;
|
||||
*)
|
||||
if [[ "$INPUT_FILES" != "" ]]; then
|
||||
INPUT_FILES="$INPUT_FILES $param"
|
||||
else
|
||||
INPUT_FILES="$param"
|
||||
fi
|
||||
;;
|
||||
esac
|
||||
done
|
||||
|
||||
function status {
|
||||
msg=$1
|
||||
[[ $quiet -eq 1 ]] && return
|
||||
echo "$msg"
|
||||
}
|
||||
|
||||
function pcapinfo() {
|
||||
PCAP=$1
|
||||
ARGS=$2
|
||||
@@ -84,7 +123,7 @@ function zeek() {
|
||||
}
|
||||
|
||||
# if no parameters supplied, display usage
|
||||
if [ $# -eq 0 ]; then
|
||||
if [ "$INPUT_FILES" == "" ]; then
|
||||
usage
|
||||
exit 1
|
||||
fi
|
||||
@@ -96,31 +135,30 @@ if [ ! -d /opt/so/conf/suricata ]; then
|
||||
fi
|
||||
|
||||
# verify that all parameters are files
|
||||
for i in "$@"; do
|
||||
for i in $INPUT_FILES; do
|
||||
if ! [ -f "$i" ]; then
|
||||
usage
|
||||
echo "\"$i\" is not a valid file!"
|
||||
exit 2
|
||||
fi
|
||||
done
|
||||
|
||||
# track if we have any valid or invalid pcaps
|
||||
INVALID_PCAPS="no"
|
||||
VALID_PCAPS="no"
|
||||
|
||||
# track oldest start and newest end so that we can generate the Kibana search hyperlink at the end
|
||||
START_OLDEST="2050-12-31"
|
||||
END_NEWEST="1971-01-01"
|
||||
|
||||
INVALID_PCAPS_COUNT=0
|
||||
VALID_PCAPS_COUNT=0
|
||||
SKIPPED_PCAPS_COUNT=0
|
||||
|
||||
# paths must be quoted in case they include spaces
|
||||
for PCAP in "$@"; do
|
||||
for PCAP in $INPUT_FILES; do
|
||||
PCAP=$(/usr/bin/realpath "$PCAP")
|
||||
echo "Processing Import: ${PCAP}"
|
||||
echo "- verifying file"
|
||||
status "Processing Import: ${PCAP}"
|
||||
status "- verifying file"
|
||||
if ! pcapinfo "${PCAP}" > /dev/null 2>&1; then
|
||||
# try to fix pcap and then process the fixed pcap directly
|
||||
PCAP_FIXED=`mktemp /tmp/so-import-pcap-XXXXXXXXXX.pcap`
|
||||
echo "- attempting to recover corrupted PCAP file"
|
||||
status "- attempting to recover corrupted PCAP file"
|
||||
pcapfix "${PCAP}" "${PCAP_FIXED}"
|
||||
# Make fixed file world readable since the Suricata docker container will runas a non-root user
|
||||
chmod a+r "${PCAP_FIXED}"
|
||||
@@ -131,33 +169,44 @@ for PCAP in "$@"; do
|
||||
# generate a unique hash to assist with dedupe checks
|
||||
HASH=$(md5sum "${PCAP}" | awk '{ print $1 }')
|
||||
HASH_DIR=/nsm/import/${HASH}
|
||||
echo "- assigning unique identifier to import: $HASH"
|
||||
status "- assigning unique identifier to import: $HASH"
|
||||
|
||||
if [ -d $HASH_DIR ]; then
|
||||
echo "- this PCAP has already been imported; skipping"
|
||||
INVALID_PCAPS="yes"
|
||||
elif pcapinfo "${PCAP}" |egrep -q "Last packet time: 1970-01-01|Last packet time: n/a"; then
|
||||
echo "- this PCAP file is invalid; skipping"
|
||||
INVALID_PCAPS="yes"
|
||||
pcap_data=$(pcapinfo "${PCAP}")
|
||||
if ! echo "$pcap_data" | grep -q "First packet time:" || echo "$pcap_data" |egrep -q "Last packet time: 1970-01-01|Last packet time: n/a"; then
|
||||
status "- this PCAP file is invalid; skipping"
|
||||
INVALID_PCAPS_COUNT=$((INVALID_PCAPS_COUNT + 1))
|
||||
else
|
||||
VALID_PCAPS="yes"
|
||||
if [ -d $HASH_DIR ]; then
|
||||
status "- this PCAP has already been imported; skipping"
|
||||
SKIPPED_PCAPS_COUNT=$((SKIPPED_PCAPS_COUNT + 1))
|
||||
else
|
||||
VALID_PCAPS_COUNT=$((VALID_PCAPS_COUNT + 1))
|
||||
|
||||
PCAP_DIR=$HASH_DIR/pcap
|
||||
mkdir -p $PCAP_DIR
|
||||
PCAP_DIR=$HASH_DIR/pcap
|
||||
mkdir -p $PCAP_DIR
|
||||
|
||||
# generate IDS alerts and write them to standard pipeline
|
||||
echo "- analyzing traffic with Suricata"
|
||||
suricata "${PCAP}" $HASH
|
||||
{% if salt['pillar.get']('global:mdengine') == 'ZEEK' %}
|
||||
# generate Zeek logs and write them to a unique subdirectory in /nsm/import/zeek/
|
||||
# since each run writes to a unique subdirectory, there is no need for a lock file
|
||||
echo "- analyzing traffic with Zeek"
|
||||
zeek "${PCAP}" $HASH
|
||||
{% endif %}
|
||||
# generate IDS alerts and write them to standard pipeline
|
||||
status "- analyzing traffic with Suricata"
|
||||
suricata "${PCAP}" $HASH
|
||||
{% if salt['pillar.get']('global:mdengine') == 'ZEEK' %}
|
||||
# generate Zeek logs and write them to a unique subdirectory in /nsm/import/zeek/
|
||||
# since each run writes to a unique subdirectory, there is no need for a lock file
|
||||
status "- analyzing traffic with Zeek"
|
||||
zeek "${PCAP}" $HASH
|
||||
{% endif %}
|
||||
fi
|
||||
|
||||
if [[ "$HASH_FILTERS" == "" ]]; then
|
||||
HASH_FILTERS="import.id:${HASH}"
|
||||
HASHES="${HASH}"
|
||||
else
|
||||
HASH_FILTERS="$HASH_FILTERS%20OR%20import.id:${HASH}"
|
||||
HASHES="${HASHES} ${HASH}"
|
||||
fi
|
||||
|
||||
START=$(pcapinfo "${PCAP}" -a |grep "First packet time:" | awk '{print $4}')
|
||||
END=$(pcapinfo "${PCAP}" -e |grep "Last packet time:" | awk '{print $4}')
|
||||
echo "- saving PCAP data spanning dates $START through $END"
|
||||
status "- found PCAP data spanning dates $START through $END"
|
||||
|
||||
# compare $START to $START_OLDEST
|
||||
START_COMPARE=$(date -d $START +%s)
|
||||
@@ -179,37 +228,62 @@ for PCAP in "$@"; do
|
||||
|
||||
fi # end of valid pcap
|
||||
|
||||
echo
|
||||
status
|
||||
|
||||
done # end of for-loop processing pcap files
|
||||
|
||||
# remove temp files
|
||||
echo "Cleaning up:"
|
||||
for TEMP_PCAP in ${TEMP_PCAPS[@]}; do
|
||||
echo "- removing temporary pcap $TEMP_PCAP"
|
||||
status "- removing temporary pcap $TEMP_PCAP"
|
||||
rm -f $TEMP_PCAP
|
||||
done
|
||||
|
||||
# output final messages
|
||||
if [ "$INVALID_PCAPS" = "yes" ]; then
|
||||
echo
|
||||
echo "Please note! One or more pcaps was invalid! You can scroll up to see which ones were invalid."
|
||||
if [[ $INVALID_PCAPS_COUNT -gt 0 ]]; then
|
||||
status
|
||||
status "WARNING: One or more pcaps was invalid. Scroll up to see which ones were invalid."
|
||||
fi
|
||||
|
||||
START_OLDEST_SLASH=$(echo $START_OLDEST | sed -e 's/-/%2F/g')
|
||||
END_NEWEST_SLASH=$(echo $END_NEWEST | sed -e 's/-/%2F/g')
|
||||
if [[ $VALID_PCAPS_COUNT -gt 0 ]] || [[ $SKIPPED_PCAPS_COUNT -gt 0 ]]; then
|
||||
URL="https://{{ URLBASE }}/#/dashboards?q=$HASH_FILTERS%20%7C%20groupby%20-sankey%20event.dataset%20event.category%2a%20%7C%20groupby%20-pie%20event.category%20%7C%20groupby%20-bar%20event.module%20%7C%20groupby%20event.dataset%20%7C%20groupby%20event.module%20%7C%20groupby%20event.category%20%7C%20groupby%20observer.name%20%7C%20groupby%20source.ip%20%7C%20groupby%20destination.ip%20%7C%20groupby%20destination.port&t=${START_OLDEST_SLASH}%2000%3A00%3A00%20AM%20-%20${END_NEWEST_SLASH}%2000%3A00%3A00%20AM&z=UTC"
|
||||
|
||||
if [ "$VALID_PCAPS" = "yes" ]; then
|
||||
cat << EOF
|
||||
|
||||
Import complete!
|
||||
|
||||
You can use the following hyperlink to view data in the time range of your import. You can triple-click to quickly highlight the entire hyperlink and you can then copy it into your browser:
|
||||
https://{{ URLBASE }}/#/dashboards?q=import.id:${HASH}%20%7C%20groupby%20-sankey%20event.dataset%20event.category%2a%20%7C%20groupby%20-pie%20event.category%20%7C%20groupby%20-bar%20event.module%20%7C%20groupby%20event.dataset%20%7C%20groupby%20event.module%20%7C%20groupby%20event.category%20%7C%20groupby%20observer.name%20%7C%20groupby%20source.ip%20%7C%20groupby%20destination.ip%20%7C%20groupby%20destination.port&t=${START_OLDEST_SLASH}%2000%3A00%3A00%20AM%20-%20${END_NEWEST_SLASH}%2000%3A00%3A00%20AM&z=UTC
|
||||
|
||||
or you can manually set your Time Range to be (in UTC):
|
||||
From: $START_OLDEST To: $END_NEWEST
|
||||
|
||||
Please note that it may take 30 seconds or more for events to appear in Security Onion Console.
|
||||
EOF
|
||||
status "Import complete!"
|
||||
status
|
||||
status "Use the following hyperlink to view the imported data. Triple-click to quickly highlight the entire hyperlink and then copy it into a browser:"
|
||||
status "$URL"
|
||||
status
|
||||
status "or, manually set the Time Range to be (in UTC):"
|
||||
status "From: $START_OLDEST To: $END_NEWEST"
|
||||
status
|
||||
status "Note: It can take 30 seconds or more for events to appear in Security Onion Console."
|
||||
RESULT=0
|
||||
else
|
||||
START_OLDEST=
|
||||
END_NEWEST=
|
||||
URL=
|
||||
RESULT=1
|
||||
fi
|
||||
|
||||
if [[ $json -eq 1 ]]; then
|
||||
jq -n \
|
||||
--arg success_count "$VALID_PCAPS_COUNT" \
|
||||
--arg fail_count "$INVALID_PCAPS_COUNT" \
|
||||
--arg skipped_count "$SKIPPED_PCAPS_COUNT" \
|
||||
--arg begin_date "$START_OLDEST" \
|
||||
--arg end_date "$END_NEWEST" \
|
||||
--arg url "$URL" \
|
||||
--arg hashes "$HASHES" \
|
||||
'''{
|
||||
success_count: $success_count,
|
||||
fail_count: $fail_count,
|
||||
skipped_count: $skipped_count,
|
||||
begin_date: $begin_date,
|
||||
end_date: $end_date,
|
||||
url: $url,
|
||||
hash: ($hashes / " ")
|
||||
}'''
|
||||
fi
|
||||
|
||||
exit $RESULT
|
||||
File renamed without changes.
@@ -0,0 +1,81 @@
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'allowed_states.map.jinja' import allowed_states %}
|
||||
{% if sls.split('.')[0] in allowed_states %}
|
||||
{% from "curator/map.jinja" import CURATORMERGED %}
|
||||
|
||||
# Create the group
|
||||
curatorgroup:
|
||||
group.present:
|
||||
- name: curator
|
||||
- gid: 934
|
||||
|
||||
# Add user
|
||||
curator:
|
||||
user.present:
|
||||
- uid: 934
|
||||
- gid: 934
|
||||
- home: /opt/so/conf/curator
|
||||
- createhome: False
|
||||
|
||||
# Create the log directory
|
||||
curlogdir:
|
||||
file.directory:
|
||||
- name: /opt/so/log/curator
|
||||
- user: 934
|
||||
- group: 939
|
||||
|
||||
curactiondir:
|
||||
file.directory:
|
||||
- name: /opt/so/conf/curator/action
|
||||
- user: 934
|
||||
- group: 939
|
||||
- makedirs: True
|
||||
|
||||
actionconfs:
|
||||
file.recurse:
|
||||
- name: /opt/so/conf/curator/action
|
||||
- source: salt://curator/files/action
|
||||
- user: 934
|
||||
- group: 939
|
||||
- template: jinja
|
||||
- defaults:
|
||||
CURATORMERGED: {{ CURATORMERGED.elasticsearch.index_settings }}
|
||||
|
||||
curconf:
|
||||
file.managed:
|
||||
- name: /opt/so/conf/curator/curator.yml
|
||||
- source: salt://curator/files/curator.yml
|
||||
- user: 934
|
||||
- group: 939
|
||||
- mode: 660
|
||||
- template: jinja
|
||||
- show_changes: False
|
||||
|
||||
curator_sbin:
|
||||
file.recurse:
|
||||
- name: /usr/sbin
|
||||
- source: salt://curator/tools/sbin
|
||||
- user: 934
|
||||
- group: 939
|
||||
- file_mode: 755
|
||||
|
||||
curator_sbin_jinja:
|
||||
file.recurse:
|
||||
- name: /usr/sbin
|
||||
- source: salt://curator/tools/sbin_jinja
|
||||
- user: 934
|
||||
- group: 939
|
||||
- file_mode: 755
|
||||
- template: jinja
|
||||
|
||||
{% else %}
|
||||
|
||||
{{sls}}_state_not_allowed:
|
||||
test.fail_without_changes:
|
||||
- name: {{sls}}_state_not_allowed
|
||||
|
||||
{% endif %}
|
||||
+100
-98
@@ -1,98 +1,100 @@
|
||||
elasticsearch:
|
||||
index_settings:
|
||||
logs-import-so:
|
||||
close: 73000
|
||||
delete: 73001
|
||||
logs-strelka-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-suricata-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-syslog-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-zeek-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-metricbeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-osquerybeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-fleet_server-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-filebeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-auth-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-application-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-security-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-system-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-syslog-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-windows-powershell-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-windows-sysmon_operational-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-beats:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-elasticsearch:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-firewall:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-ids:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-import:
|
||||
close: 73000
|
||||
delete: 73001
|
||||
so-kratos:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-kibana:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-logstash:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-netflow:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-osquery:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-ossec:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-redis:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-strelka:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-syslog:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-zeek:
|
||||
close: 30
|
||||
delete: 365
|
||||
curator:
|
||||
enabled: False
|
||||
elasticsearch:
|
||||
index_settings:
|
||||
logs-import-so:
|
||||
close: 73000
|
||||
delete: 73001
|
||||
logs-strelka-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-suricata-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-syslog-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-zeek-so:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-metricbeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-osquerybeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-fleet_server-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-filebeat-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-elastic_agent-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-auth-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-application-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-security-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-system-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-system-syslog-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-windows-powershell-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
logs-windows-sysmon_operational-default:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-beats:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-elasticsearch:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-firewall:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-ids:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-import:
|
||||
close: 73000
|
||||
delete: 73001
|
||||
so-kratos:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-kibana:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-logstash:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-netflow:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-osquery:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-ossec:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-redis:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-strelka:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-syslog:
|
||||
close: 30
|
||||
delete: 365
|
||||
so-zeek:
|
||||
close: 30
|
||||
delete: 365
|
||||
@@ -0,0 +1,35 @@
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'allowed_states.map.jinja' import allowed_states %}
|
||||
{% if sls.split('.')[0] in allowed_states %}
|
||||
|
||||
include:
|
||||
- curator.sostatus
|
||||
|
||||
so-curator:
|
||||
docker_container.absent:
|
||||
- force: True
|
||||
|
||||
so-curator_so-status.disabled:
|
||||
file.comment:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- regex: ^so-curator$
|
||||
|
||||
so-curator-cluster-close:
|
||||
cron.absent:
|
||||
- identifier: so-curator-cluster-close
|
||||
|
||||
so-curator-cluster-delete:
|
||||
cron.absent:
|
||||
- identifier: so-curator-cluster-delete
|
||||
|
||||
{% else %}
|
||||
|
||||
{{sls}}_state_not_allowed:
|
||||
test.fail_without_changes:
|
||||
- name: {{sls}}_state_not_allowed
|
||||
|
||||
{% endif %}
|
||||
@@ -0,0 +1,88 @@
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'allowed_states.map.jinja' import allowed_states %}
|
||||
{% if sls.split('.')[0] in allowed_states %}
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
{% from 'docker/docker.map.jinja' import DOCKER %}
|
||||
|
||||
include:
|
||||
- curator.config
|
||||
- curator.sostatus
|
||||
|
||||
so-curator:
|
||||
docker_container.running:
|
||||
- image: {{ GLOBALS.registry_host }}:5000/{{ GLOBALS.image_repo }}/so-curator:{{ GLOBALS.so_version }}
|
||||
- start: True
|
||||
- hostname: curator
|
||||
- name: so-curator
|
||||
- user: curator
|
||||
- networks:
|
||||
- sobridge:
|
||||
- ipv4_address: {{ DOCKER.containers['so-curator'].ip }}
|
||||
- interactive: True
|
||||
- tty: True
|
||||
- binds:
|
||||
- /opt/so/conf/curator/curator.yml:/etc/curator/config/curator.yml:ro
|
||||
- /opt/so/conf/curator/action/:/etc/curator/action:ro
|
||||
- /opt/so/log/curator:/var/log/curator:rw
|
||||
{% if DOCKER.containers['so-curator'].custom_bind_mounts %}
|
||||
{% for BIND in DOCKER.containers['so-curator'].custom_bind_mounts %}
|
||||
- {{ BIND }}
|
||||
{% endfor %}
|
||||
{% endif %}
|
||||
{% if DOCKER.containers['so-curator'].extra_hosts %}
|
||||
- extra_hosts:
|
||||
{% for XTRAHOST in DOCKER.containers['so-curator'].extra_hosts %}
|
||||
- {{ XTRAHOST }}
|
||||
{% endfor %}
|
||||
{% endif %}
|
||||
{% if DOCKER.containers['so-curator'].extra_env %}
|
||||
- environment:
|
||||
{% for XTRAENV in DOCKER.containers['so-curator'].extra_env %}
|
||||
- {{ XTRAENV }}
|
||||
{% endfor %}
|
||||
{% endif %}
|
||||
- require:
|
||||
- file: actionconfs
|
||||
- file: curconf
|
||||
- file: curlogdir
|
||||
- watch:
|
||||
- file: curconf
|
||||
|
||||
delete_so-curator_so-status.disabled:
|
||||
file.uncomment:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- regex: ^so-curator$
|
||||
|
||||
so-curator-cluster-close:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-curator-cluster-close > /opt/so/log/curator/cron-close.log 2>&1
|
||||
- identifier: so-curator-cluster-close
|
||||
- user: root
|
||||
- minute: '2'
|
||||
- hour: '*/1'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
so-curator-cluster-delete:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-curator-cluster-delete > /opt/so/log/curator/cron-cluster-delete.log 2>&1
|
||||
- identifier: so-curator-cluster-delete
|
||||
- user: root
|
||||
- minute: '*/5'
|
||||
- hour: '*'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
{% else %}
|
||||
|
||||
{{sls}}_state_not_allowed:
|
||||
test.fail_without_changes:
|
||||
- name: {{sls}}_state_not_allowed
|
||||
|
||||
{% endif %}
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -13,7 +13,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -13,7 +13,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -12,7 +12,7 @@ actions:
|
||||
options:
|
||||
delete_aliases: False
|
||||
timeout_override:
|
||||
continue_if_exception: False
|
||||
ignore_empty_list: True
|
||||
disable_action: False
|
||||
filters:
|
||||
- filtertype: pattern
|
||||
|
||||
@@ -1,85 +0,0 @@
|
||||
#!/bin/bash
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
{% import_yaml 'elasticsearch/defaults.yaml' as ELASTICDEFAULTS %}
|
||||
{%- set ELASTICSEARCH_HOST = GLOBALS.node_ip -%}
|
||||
{%- set RETENTION = salt['pillar.get']('elasticsearch:retention', ELASTICDEFAULTS.elasticsearch.retention, merge=true) -%}
|
||||
|
||||
LOG="/opt/so/log/curator/so-curator-cluster-delete.log"
|
||||
LOG_SIZE_LIMIT=$(/usr/sbin/so-elasticsearch-cluster-space-total {{ RETENTION.retention_pct}})
|
||||
|
||||
overlimit() {
|
||||
[[ $(/usr/sbin/so-elasticsearch-cluster-space-used) -gt "${LOG_SIZE_LIMIT}" ]]
|
||||
}
|
||||
|
||||
closedindices() {
|
||||
# If we can't query Elasticsearch, then immediately return false.
|
||||
/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep close > /dev/null 2>&1
|
||||
[ $? -eq 1 ] && return false
|
||||
# First, get the list of closed indices using _cat/indices?h=index,status | grep close | awk '{print $1}'.
|
||||
# Next, filter out any so-case indices.
|
||||
# Finally, use grep's -q option to return true if there are any remaining logstash-, so-, or .ds-logs- indices.
|
||||
/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep close | awk '{print $1}' | grep -v "so-case" | grep -q -E "(logstash-|so-|.ds-logs-)"
|
||||
}
|
||||
|
||||
# Check for 2 conditions:
|
||||
# 1. Are Elasticsearch indices using more disk space than LOG_SIZE_LIMIT?
|
||||
# 2. Are there any closed indices that we can delete?
|
||||
# If both conditions are true, keep on looping until one of the conditions is false.
|
||||
|
||||
while overlimit && closedindices; do
|
||||
CLOSED_INDICES=$(/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep close | awk '{print $1}' | grep -v "so-case" | grep -E "(logstash-|so-|.ds-logs-)" | sort -t- -k3)
|
||||
# We iterate through the closed indices
|
||||
for CLOSED_INDEX in ${CLOSED_INDICES}; do
|
||||
# Now that we've sorted the indices from oldest to newest, we need to check each index to see if it is assigned as the current write index for a data stream
|
||||
# To do so, we need to identify to which data stream this index is associated
|
||||
# We extract the data stream name using the pattern below
|
||||
DATASTREAM_PATTERN="logs-[a-zA-Z_.]+-[a-zA-Z_.]+"
|
||||
DATASTREAM=$(echo "${CLOSED_INDEX}" | grep -oE "$DATASTREAM_PATTERN")
|
||||
# We look up the data stream, and determine the write index
|
||||
CURRENT_WRITE_INDEX=$(/usr/sbin/so-elasticsearch-query _data_stream/$DATASTREAM | jq -r .data_streams[0].indices[-1].index_name)
|
||||
# We make sure we are not trying to delete a write index
|
||||
if [ "${CLOSED_INDEX}" != "${CURRENT_WRITE_INDEX}" ]; then
|
||||
# This should not be a write index, so we should be allowed to delete it
|
||||
/usr/sbin/so-elasticsearch-query ${CLOSED_INDEX} -XDELETE
|
||||
# Finally, write a log entry that says we deleted it.
|
||||
echo "$(date) - Used disk space exceeds LOG_SIZE_LIMIT (${LOG_SIZE_LIMIT} GB) - Index ${CLOSED_INDEX} deleted ..." >> ${LOG}
|
||||
fi
|
||||
if ! overlimit; then
|
||||
exit
|
||||
fi
|
||||
done
|
||||
done
|
||||
|
||||
while overlimit; do
|
||||
|
||||
# We need to determine the oldest open index.
|
||||
# First, get the list of open indices using _cat/indices?h=index,status | grep open | awk '{print $1}'.
|
||||
# Next, filter out any so-case indices and only select the remaining logstash-, so-, or .ds-logs- indices.
|
||||
# Then, sort by date by telling sort to use hyphen as delimiter and sort on the third field.
|
||||
OPEN_INDICES=$(/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep open | awk '{print $1}' | grep -v "so-case" | grep -E "(logstash-|so-|.ds-logs-)" | sort -t- -k3)
|
||||
# We iterate through the open indices
|
||||
for OPEN_INDEX in ${OPEN_INDICES}; do
|
||||
# Now that we've sorted the indices from oldest to newest, we need to check each index to see if it is assigned as the current write index for a data stream
|
||||
# To do so, we need to identify to which data stream this index is associated
|
||||
# We extract the data stream name using the pattern below
|
||||
DATASTREAM_PATTERN="logs-[a-zA-Z_.]+-[a-zA-Z_.]+"
|
||||
DATASTREAM=$(echo "${OPEN_INDEX}" | grep -oE "$DATASTREAM_PATTERN")
|
||||
# We look up the data stream, and determine the write index
|
||||
CURRENT_WRITE_INDEX=$(/usr/sbin/so-elasticsearch-query _data_stream/$DATASTREAM | jq -r .data_streams[0].indices[-1].index_name)
|
||||
# We make sure we are not trying to delete a write index
|
||||
if [ "${OPEN_INDEX}" != "${CURRENT_WRITE_INDEX}" ]; then
|
||||
# This should not be a write index, so we should be allowed to delete it
|
||||
/usr/sbin/so-elasticsearch-query ${OPEN_INDEX} -XDELETE
|
||||
# Finally, write a log entry that says we deleted it.
|
||||
echo "$(date) - Used disk space exceeds LOG_SIZE_LIMIT (${LOG_SIZE_LIMIT} GB) - Index ${OPEN_INDEX} deleted ..." >> ${LOG}
|
||||
fi
|
||||
if ! overlimit; then
|
||||
exit
|
||||
fi
|
||||
done
|
||||
done
|
||||
@@ -4,9 +4,9 @@
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
{% if grains['role'] in ['so-searchnode', 'so-heavynode'] %}
|
||||
{% if GLOBALS.role in ['so-searchnode', 'so-heavynode'] %}
|
||||
{%- set elasticsearch = GLOBALS.node_ip -%}
|
||||
{% elif grains['role'] in ['so-eval', 'so-managersearch', 'so-standalone', 'so-manager'] %}
|
||||
{% elif GLOBALS.role in ['so-eval', 'so-managersearch', 'so-standalone', 'so-manager'] %}
|
||||
{%- set elasticsearch = GLOBALS.manager_ip -%}
|
||||
{%- endif %}
|
||||
{%- set ES_USER = salt['pillar.get']('elasticsearch:auth:users:so_elastic_user:user', '') %}
|
||||
@@ -30,10 +30,8 @@ elasticsearch:
|
||||
id:
|
||||
api_key:
|
||||
master_only: False
|
||||
{%- if salt['pillar.get']('elasticsearch:auth:enabled') is sameas true %}
|
||||
username: "{{ ES_USER }}"
|
||||
password: "{{ ES_PASS }}"
|
||||
{%- endif %}
|
||||
|
||||
logging:
|
||||
loglevel: INFO
|
||||
|
||||
+5
-147
@@ -3,153 +3,11 @@
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'allowed_states.map.jinja' import allowed_states %}
|
||||
{% if sls in allowed_states %}
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
{% from 'docker/docker.map.jinja' import DOCKER %}
|
||||
{% from "curator/map.jinja" import CURATOROPTIONS %}
|
||||
{% from "curator/map.jinja" import CURATORMERGED %}
|
||||
{% set REMOVECURATORCRON = False %}
|
||||
|
||||
# Curator
|
||||
# Create the group
|
||||
curatorgroup:
|
||||
group.present:
|
||||
- name: curator
|
||||
- gid: 934
|
||||
|
||||
# Add user
|
||||
curator:
|
||||
user.present:
|
||||
- uid: 934
|
||||
- gid: 934
|
||||
- home: /opt/so/conf/curator
|
||||
- createhome: False
|
||||
|
||||
# Create the log directory
|
||||
curlogdir:
|
||||
file.directory:
|
||||
- name: /opt/so/log/curator
|
||||
- user: 934
|
||||
- group: 939
|
||||
|
||||
curactiondir:
|
||||
file.directory:
|
||||
- name: /opt/so/conf/curator/action
|
||||
- user: 934
|
||||
- group: 939
|
||||
- makedirs: True
|
||||
|
||||
actionconfs:
|
||||
file.recurse:
|
||||
- name: /opt/so/conf/curator/action
|
||||
- source: salt://curator/files/action
|
||||
- user: 934
|
||||
- group: 939
|
||||
- template: jinja
|
||||
- defaults:
|
||||
CURATORMERGED: {{ CURATORMERGED }}
|
||||
|
||||
curconf:
|
||||
file.managed:
|
||||
- name: /opt/so/conf/curator/curator.yml
|
||||
- source: salt://curator/files/curator.yml
|
||||
- user: 934
|
||||
- group: 939
|
||||
- mode: 660
|
||||
- template: jinja
|
||||
- show_changes: False
|
||||
|
||||
curclusterclose:
|
||||
file.managed:
|
||||
- name: /usr/sbin/so-curator-cluster-close
|
||||
- source: salt://curator/files/bin/so-curator-cluster-close
|
||||
- user: 934
|
||||
- group: 939
|
||||
- mode: 755
|
||||
- template: jinja
|
||||
|
||||
curclusterdelete:
|
||||
file.managed:
|
||||
- name: /usr/sbin/so-curator-cluster-delete
|
||||
- source: salt://curator/files/bin/so-curator-cluster-delete
|
||||
- user: 934
|
||||
- group: 939
|
||||
- mode: 755
|
||||
|
||||
curclusterdeletedelete:
|
||||
file.managed:
|
||||
- name: /usr/sbin/so-curator-cluster-delete-delete
|
||||
- source: salt://curator/files/bin/so-curator-cluster-delete-delete
|
||||
- user: 934
|
||||
- group: 939
|
||||
- mode: 755
|
||||
- template: jinja
|
||||
|
||||
so-curator:
|
||||
docker_container.{{ CURATOROPTIONS.status }}:
|
||||
- image: {{ GLOBALS.registry_host }}:5000/{{ GLOBALS.image_repo }}/so-curator:{{ GLOBALS.so_version }}
|
||||
- start: {{ CURATOROPTIONS.start }}
|
||||
- hostname: curator
|
||||
- name: so-curator
|
||||
- user: curator
|
||||
- networks:
|
||||
- sobridge:
|
||||
- ipv4_address: {{ DOCKER.containers['so-curator'].ip }}
|
||||
- interactive: True
|
||||
- tty: True
|
||||
- binds:
|
||||
- /opt/so/conf/curator/curator.yml:/etc/curator/config/curator.yml:ro
|
||||
- /opt/so/conf/curator/action/:/etc/curator/action:ro
|
||||
- /opt/so/log/curator:/var/log/curator:rw
|
||||
- require:
|
||||
- file: actionconfs
|
||||
- file: curconf
|
||||
- file: curlogdir
|
||||
- watch:
|
||||
- file: curconf
|
||||
|
||||
append_so-curator_so-status.conf:
|
||||
file.append:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- text: so-curator
|
||||
- unless: grep -q so-curator /opt/so/conf/so-status/so-status.conf
|
||||
{% if not CURATOROPTIONS.start %}
|
||||
so-curator_so-status.disabled:
|
||||
file.comment:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- regex: ^so-curator$
|
||||
{% else %}
|
||||
delete_so-curator_so-status.disabled:
|
||||
file.uncomment:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- regex: ^so-curator$
|
||||
{% endif %}
|
||||
|
||||
so-curatorclusterclose:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-curator-cluster-close > /opt/so/log/curator/cron-close.log 2>&1
|
||||
- user: root
|
||||
- minute: '2'
|
||||
- hour: '*/1'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
|
||||
so-curatorclusterdeletecron:
|
||||
cron.present:
|
||||
- name: /usr/sbin/so-curator-cluster-delete > /opt/so/log/curator/cron-cluster-delete.log 2>&1
|
||||
- user: root
|
||||
- minute: '*/5'
|
||||
- hour: '*'
|
||||
- daymonth: '*'
|
||||
- month: '*'
|
||||
- dayweek: '*'
|
||||
{% from 'curator/map.jinja' import CURATORMERGED %}
|
||||
|
||||
include:
|
||||
{% if CURATORMERGED.enabled %}
|
||||
- curator.enabled
|
||||
{% else %}
|
||||
|
||||
{{sls}}_state_not_allowed:
|
||||
test.fail_without_changes:
|
||||
- name: {{sls}}_state_not_allowed
|
||||
|
||||
- curator.disabled
|
||||
{% endif %}
|
||||
+5
-16
@@ -1,18 +1,7 @@
|
||||
{% set CURATOROPTIONS = {} %}
|
||||
{% set ENABLED = salt['pillar.get']('curator:enabled', True) %}
|
||||
{% do CURATOROPTIONS.update({'manage_sostatus': True}) %}
|
||||
|
||||
# don't start the docker container if curator is disabled via pillar
|
||||
{% if not ENABLED %}
|
||||
{% do CURATOROPTIONS.update({'start': False}) %}
|
||||
{% do CURATOROPTIONS.update({'status': 'absent'}) %}
|
||||
{% if (TRUECLUSTER and grains.id.split('_')|last == 'searchnode') or (not TRUECLUSTER and grains.id.split('_')|last == 'manager') %}
|
||||
{% do CURATOROPTIONS.update({'manage_sostatus': False}) %}
|
||||
{% endif %}
|
||||
{% else %}
|
||||
{% do CURATOROPTIONS.update({'start': True}) %}
|
||||
{% do CURATOROPTIONS.update({'status': 'running'}) %}
|
||||
{% endif %}
|
||||
{# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
Elastic License 2.0. #}
|
||||
|
||||
{% import_yaml 'curator/defaults.yaml' as CURATORDEFAULTS %}
|
||||
{% set CURATORMERGED = salt['pillar.get']('elasticsearch:index_settings', CURATORDEFAULTS.elasticsearch.index_settings, merge=true) %}
|
||||
{% set CURATORMERGED = salt['pillar.get']('curator', CURATORDEFAULTS.curator, merge=true) %}
|
||||
@@ -0,0 +1,108 @@
|
||||
curator:
|
||||
enabled:
|
||||
description: You can enable or disable Curator.
|
||||
helpLink: curator.html
|
||||
elasticsearch:
|
||||
index_settings:
|
||||
logs-import-so:
|
||||
close: &close
|
||||
description: Age, in days, when Curator closes the index.
|
||||
helpLink: curator.html
|
||||
forcedType: int
|
||||
delete: &delete
|
||||
description: Age, in days, when Curator deletes the index.
|
||||
helpLink: curator.html
|
||||
forcedType: int
|
||||
logs-strelka-so:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-suricata-so:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-syslog-so:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-zeek-so:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-elastic_agent-metricbeat-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-elastic_agent-osquerybeat-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-elastic_agent-fleet_server-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-elastic_agent-filebeat-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-elastic_agent-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-system-auth-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-system-application-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-system-security-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-system-system-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-system-syslog-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-windows-powershell-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
logs-windows-sysmon_operational-default:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-beats:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-elasticsearch:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-firewall:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-ids:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-import:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-kratos:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-kibana:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-logstash:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-netflow:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-osquery:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-ossec:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-redis:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-strelka:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-syslog:
|
||||
close: *close
|
||||
delete: *delete
|
||||
so-zeek:
|
||||
close: *close
|
||||
delete: *delete
|
||||
@@ -0,0 +1,21 @@
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'allowed_states.map.jinja' import allowed_states %}
|
||||
{% if sls.split('.')[0] in allowed_states %}
|
||||
|
||||
append_so-curator_so-status.conf:
|
||||
file.append:
|
||||
- name: /opt/so/conf/so-status/so-status.conf
|
||||
- text: so-curator
|
||||
- unless: grep -q so-curator /opt/so/conf/so-status/so-status.conf
|
||||
|
||||
{% else %}
|
||||
|
||||
{{sls}}_state_not_allowed:
|
||||
test.fail_without_changes:
|
||||
- name: {{sls}}_state_not_allowed
|
||||
|
||||
{% endif %}
|
||||
File renamed without changes.
File renamed without changes.
File renamed without changes.
File renamed without changes.
Executable → Regular
File renamed without changes.
Executable → Regular
File renamed without changes.
Executable → Regular
File renamed without changes.
@@ -0,0 +1,67 @@
|
||||
#!/bin/bash
|
||||
# Copyright Security Onion Solutions LLC and/or licensed to Security Onion Solutions LLC under one
|
||||
# or more contributor license agreements. Licensed under the Elastic License 2.0 as shown at
|
||||
# https://securityonion.net/license; you may not use this file except in compliance with the
|
||||
# Elastic License 2.0.
|
||||
|
||||
{% from 'vars/globals.map.jinja' import GLOBALS %}
|
||||
{% import_yaml 'elasticsearch/defaults.yaml' as ELASTICDEFAULTS %}
|
||||
{%- set ELASTICSEARCH_HOST = GLOBALS.node_ip -%}
|
||||
{%- set RETENTION = salt['pillar.get']('elasticsearch:retention', ELASTICDEFAULTS.elasticsearch.retention, merge=true) -%}
|
||||
|
||||
LOG="/opt/so/log/curator/so-curator-cluster-delete.log"
|
||||
ALERT_LOG="/opt/so/log/curator/alert.log"
|
||||
LOG_SIZE_LIMIT_GB=$(/usr/sbin/so-elasticsearch-cluster-space-total {{ RETENTION.retention_pct}})
|
||||
LOG_SIZE_LIMIT=$(( "$LOG_SIZE_LIMIT_GB" * 1000 * 1000 * 1000 ))
|
||||
ITERATION=0
|
||||
MAX_ITERATIONS=10
|
||||
|
||||
overlimit() {
|
||||
[[ $(/usr/sbin/so-elasticsearch-cluster-space-used) -gt ${LOG_SIZE_LIMIT} ]]
|
||||
}
|
||||
|
||||
###########################
|
||||
# Check for 2 conditions: #
|
||||
###########################
|
||||
# 1. Check if Elasticsearch indices are using more disk space than LOG_SIZE_LIMIT
|
||||
# 2. Check if the maximum number of iterations - MAX_ITERATIONS - has been exceeded. If so, exit.
|
||||
# Closed indices will be deleted first. If we are able to bring disk space under LOG_SIZE_LIMIT, or the number of iterations has exceeded the maximum allowed number of iterations, we will break out of the loop.
|
||||
|
||||
while overlimit && [[ $ITERATION -lt $MAX_ITERATIONS ]]; do
|
||||
|
||||
# If we can't query Elasticsearch, then immediately return false.
|
||||
/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status > /dev/null 2>&1
|
||||
[ $? -eq 1 ] && echo "$(date) - Could not query Elasticsearch." >> ${LOG} && exit
|
||||
|
||||
# We iterate through the closed and open indices
|
||||
CLOSED_INDICES=$(/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep 'close$' | awk '{print $1}' | grep -vE "playbook|so-case" | grep -E "(logstash-|so-|.ds-logs-)" | sort -t- -k3)
|
||||
OPEN_INDICES=$(/usr/sbin/so-elasticsearch-query _cat/indices?h=index,status | grep 'open$' | awk '{print $1}' | grep -vE "playbook|so-case" | grep -E "(logstash-|so-|.ds-logs-)" | sort -t- -k3)
|
||||
|
||||
for INDEX in ${CLOSED_INDICES} ${OPEN_INDICES}; do
|
||||
# Now that we've sorted the indices from oldest to newest, we need to check each index to see if it is assigned as the current write index for a data stream
|
||||
# To do so, we need to identify to which data stream this index is associated
|
||||
# We extract the data stream name using the pattern below
|
||||
DATASTREAM_PATTERN="logs-[a-zA-Z_.]+-[a-zA-Z_.]+"
|
||||
DATASTREAM=$(echo "${INDEX}" | grep -oE "$DATASTREAM_PATTERN")
|
||||
# We look up the data stream, and determine the write index. If there is only one backing index, we delete the entire data stream
|
||||
BACKING_INDICES=$(/usr/sbin/so-elasticsearch-query _data_stream/${DATASTREAM} | jq -r '.data_streams[0].indices | length')
|
||||
if [ "$BACKING_INDICES" -gt 1 ]; then
|
||||
CURRENT_WRITE_INDEX=$(/usr/sbin/so-elasticsearch-query _data_stream/$DATASTREAM | jq -r .data_streams[0].indices[-1].index_name)
|
||||
# We make sure we are not trying to delete a write index
|
||||
if [ "${INDEX}" != "${CURRENT_WRITE_INDEX}" ]; then
|
||||
# This should not be a write index, so we should be allowed to delete it
|
||||
printf "\n$(date) - Used disk space exceeds LOG_SIZE_LIMIT (${LOG_SIZE_LIMIT_GB} GB) - Deleting ${INDEX} index...\n" >> ${LOG}
|
||||
/usr/sbin/so-elasticsearch-query ${INDEX} -XDELETE >> ${LOG} 2>&1
|
||||
fi
|
||||
fi
|
||||
if ! overlimit ; then
|
||||
exit
|
||||
fi
|
||||
((ITERATION++))
|
||||
done
|
||||
if [[ $ITERATION -ge $MAX_ITERATIONS ]]; then
|
||||
alert_id=$(uuidgen)
|
||||
printf "\n$(date) -> Maximum iteration limit reached ($MAX_ITERATIONS). Unable to bring disk below threshold. Writing alert ($alert_id) to ${ALERT_LOG}\n" >> ${LOG}
|
||||
printf "\n$(date),$alert_id,Maximum iteration limit reached ($MAX_ITERATIONS). Unable to bring disk below threshold.\n" >> ${ALERT_LOG}
|
||||
fi
|
||||
done
|
||||

File renamed without changes.

File renamed without changes.

File renamed without changes.
Loaded 100 of 828 files, more files were not shown because too many files have changed in this diff.
Show more
Reference in new issue
Block a user